Secure today. Enable tomorrow.
No mock-ups and no slides. Every image here is the real Aavishield console, captured with demo data from a fictional company.
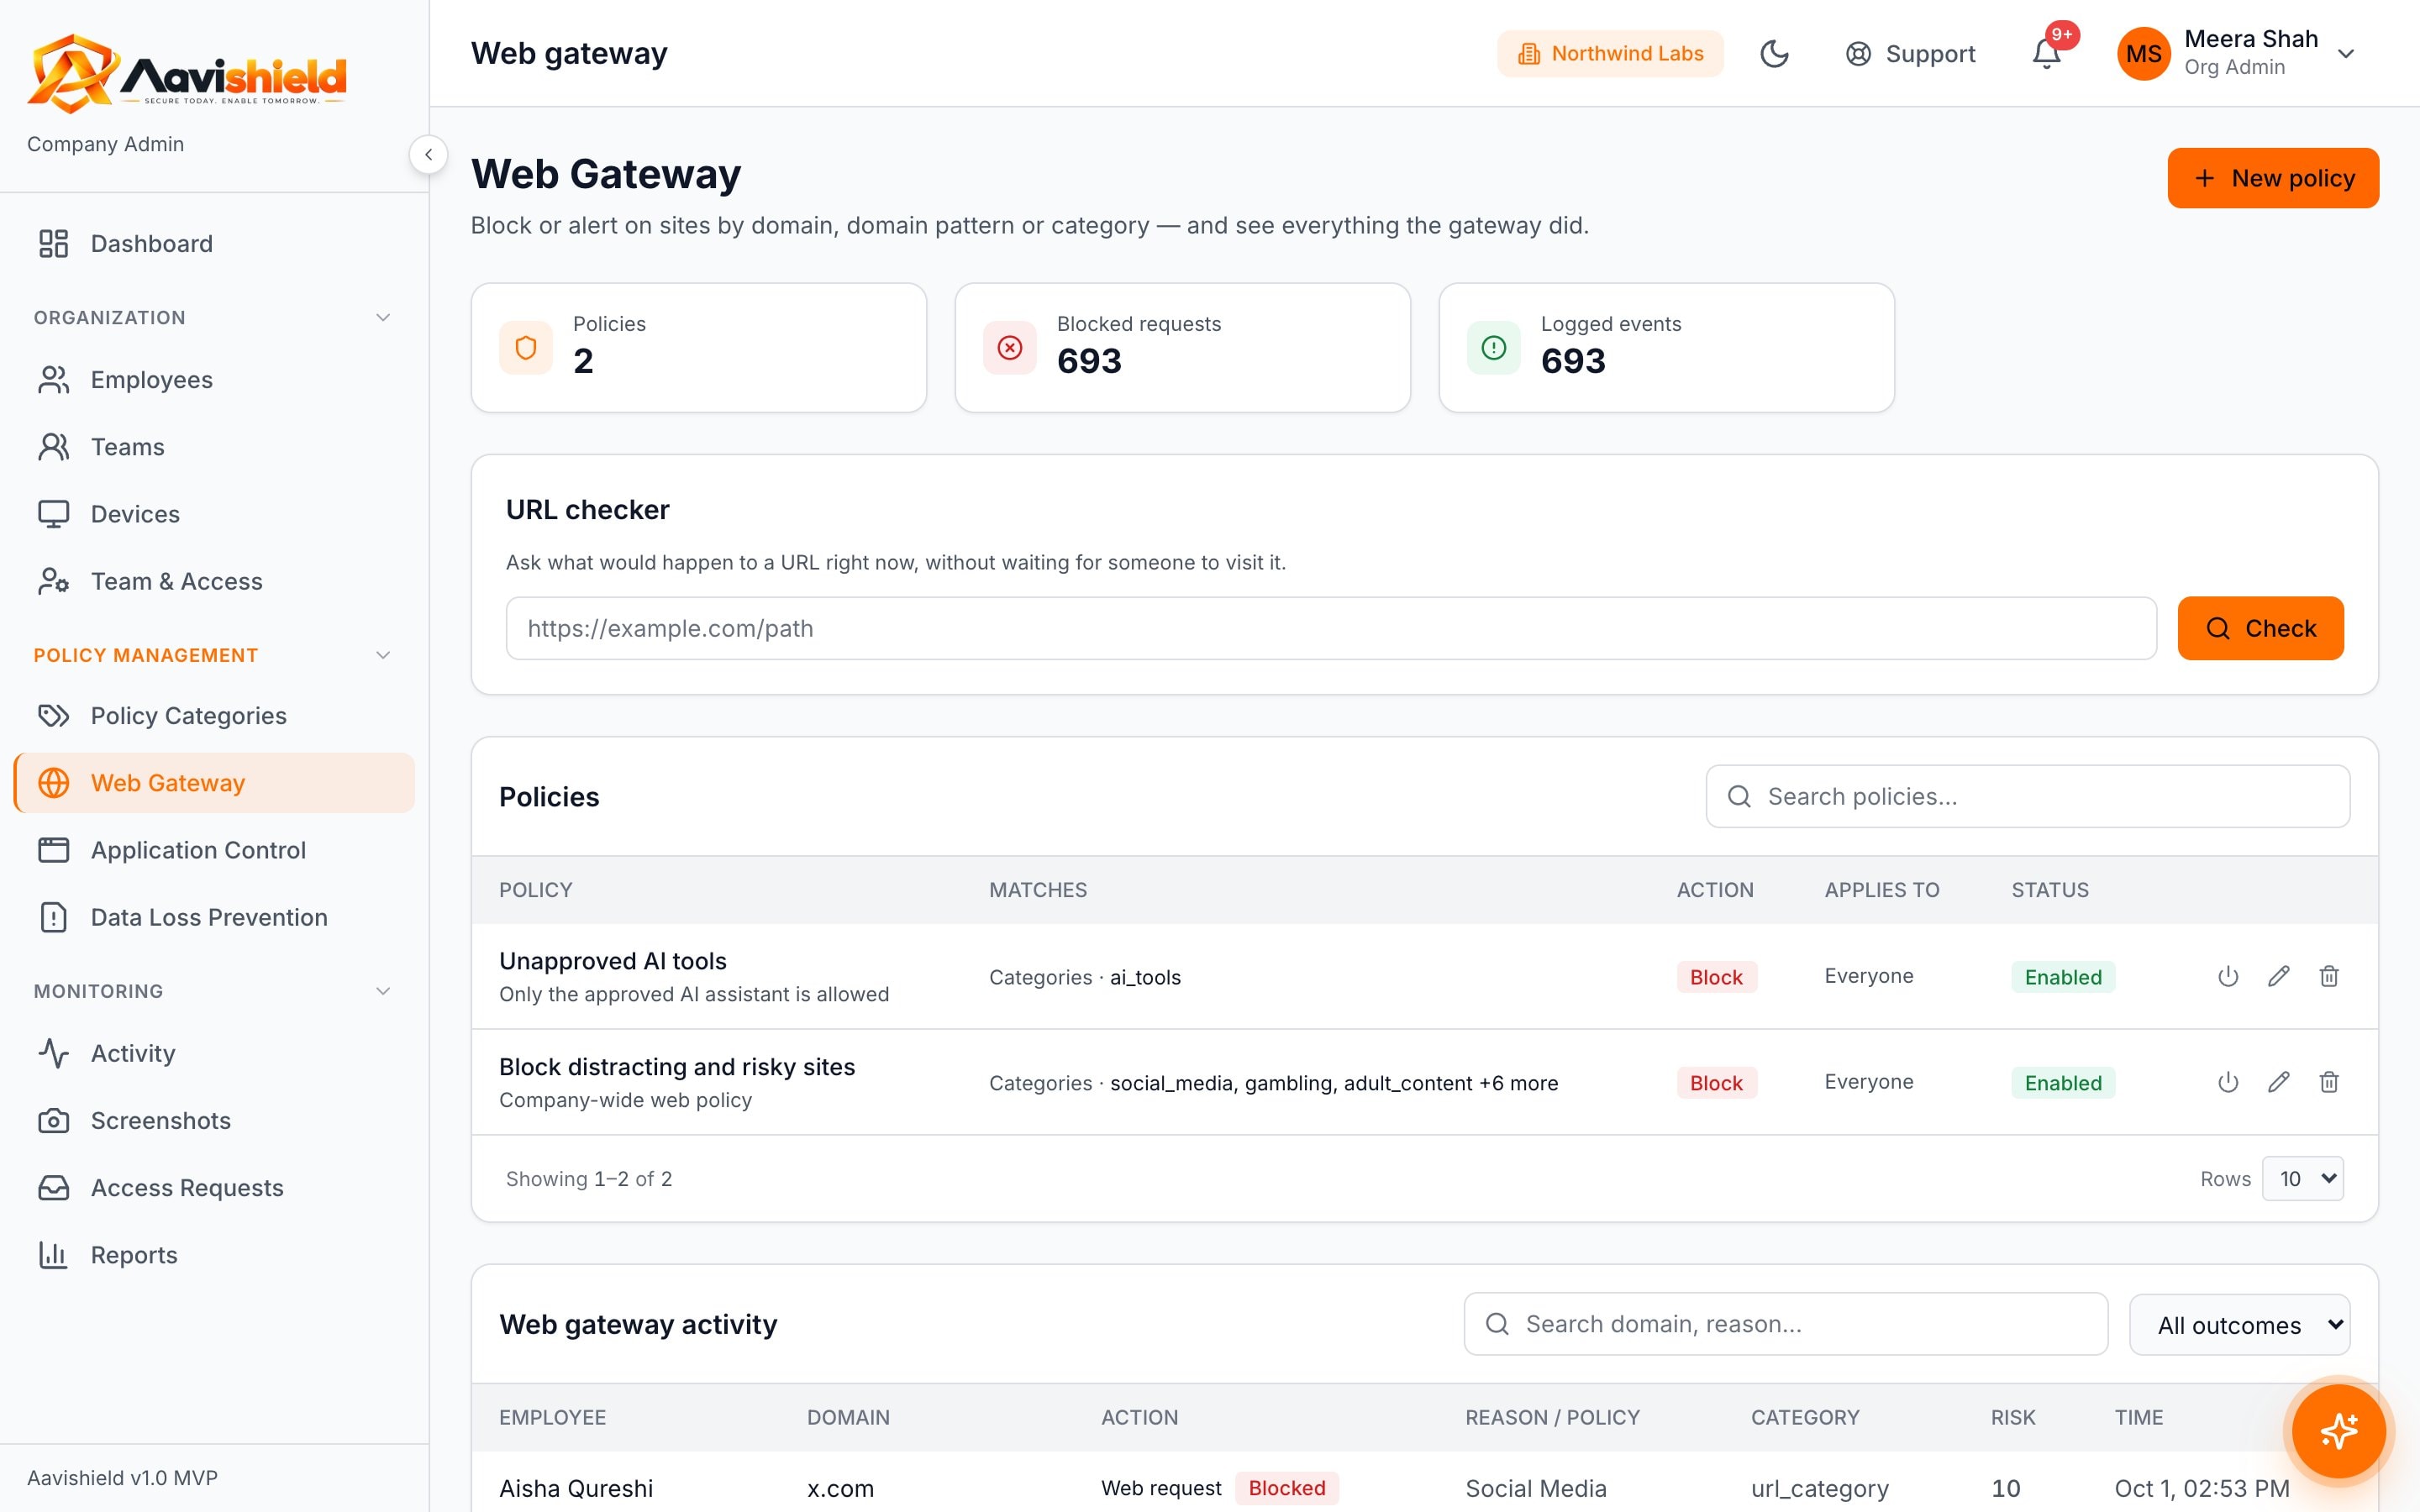
Web categories, custom domains, blocked applications and data detection, all from one place.
Each policy shows what it matches, the action, who it applies to and whether it is enabled. Counts of blocked and logged requests sit above.
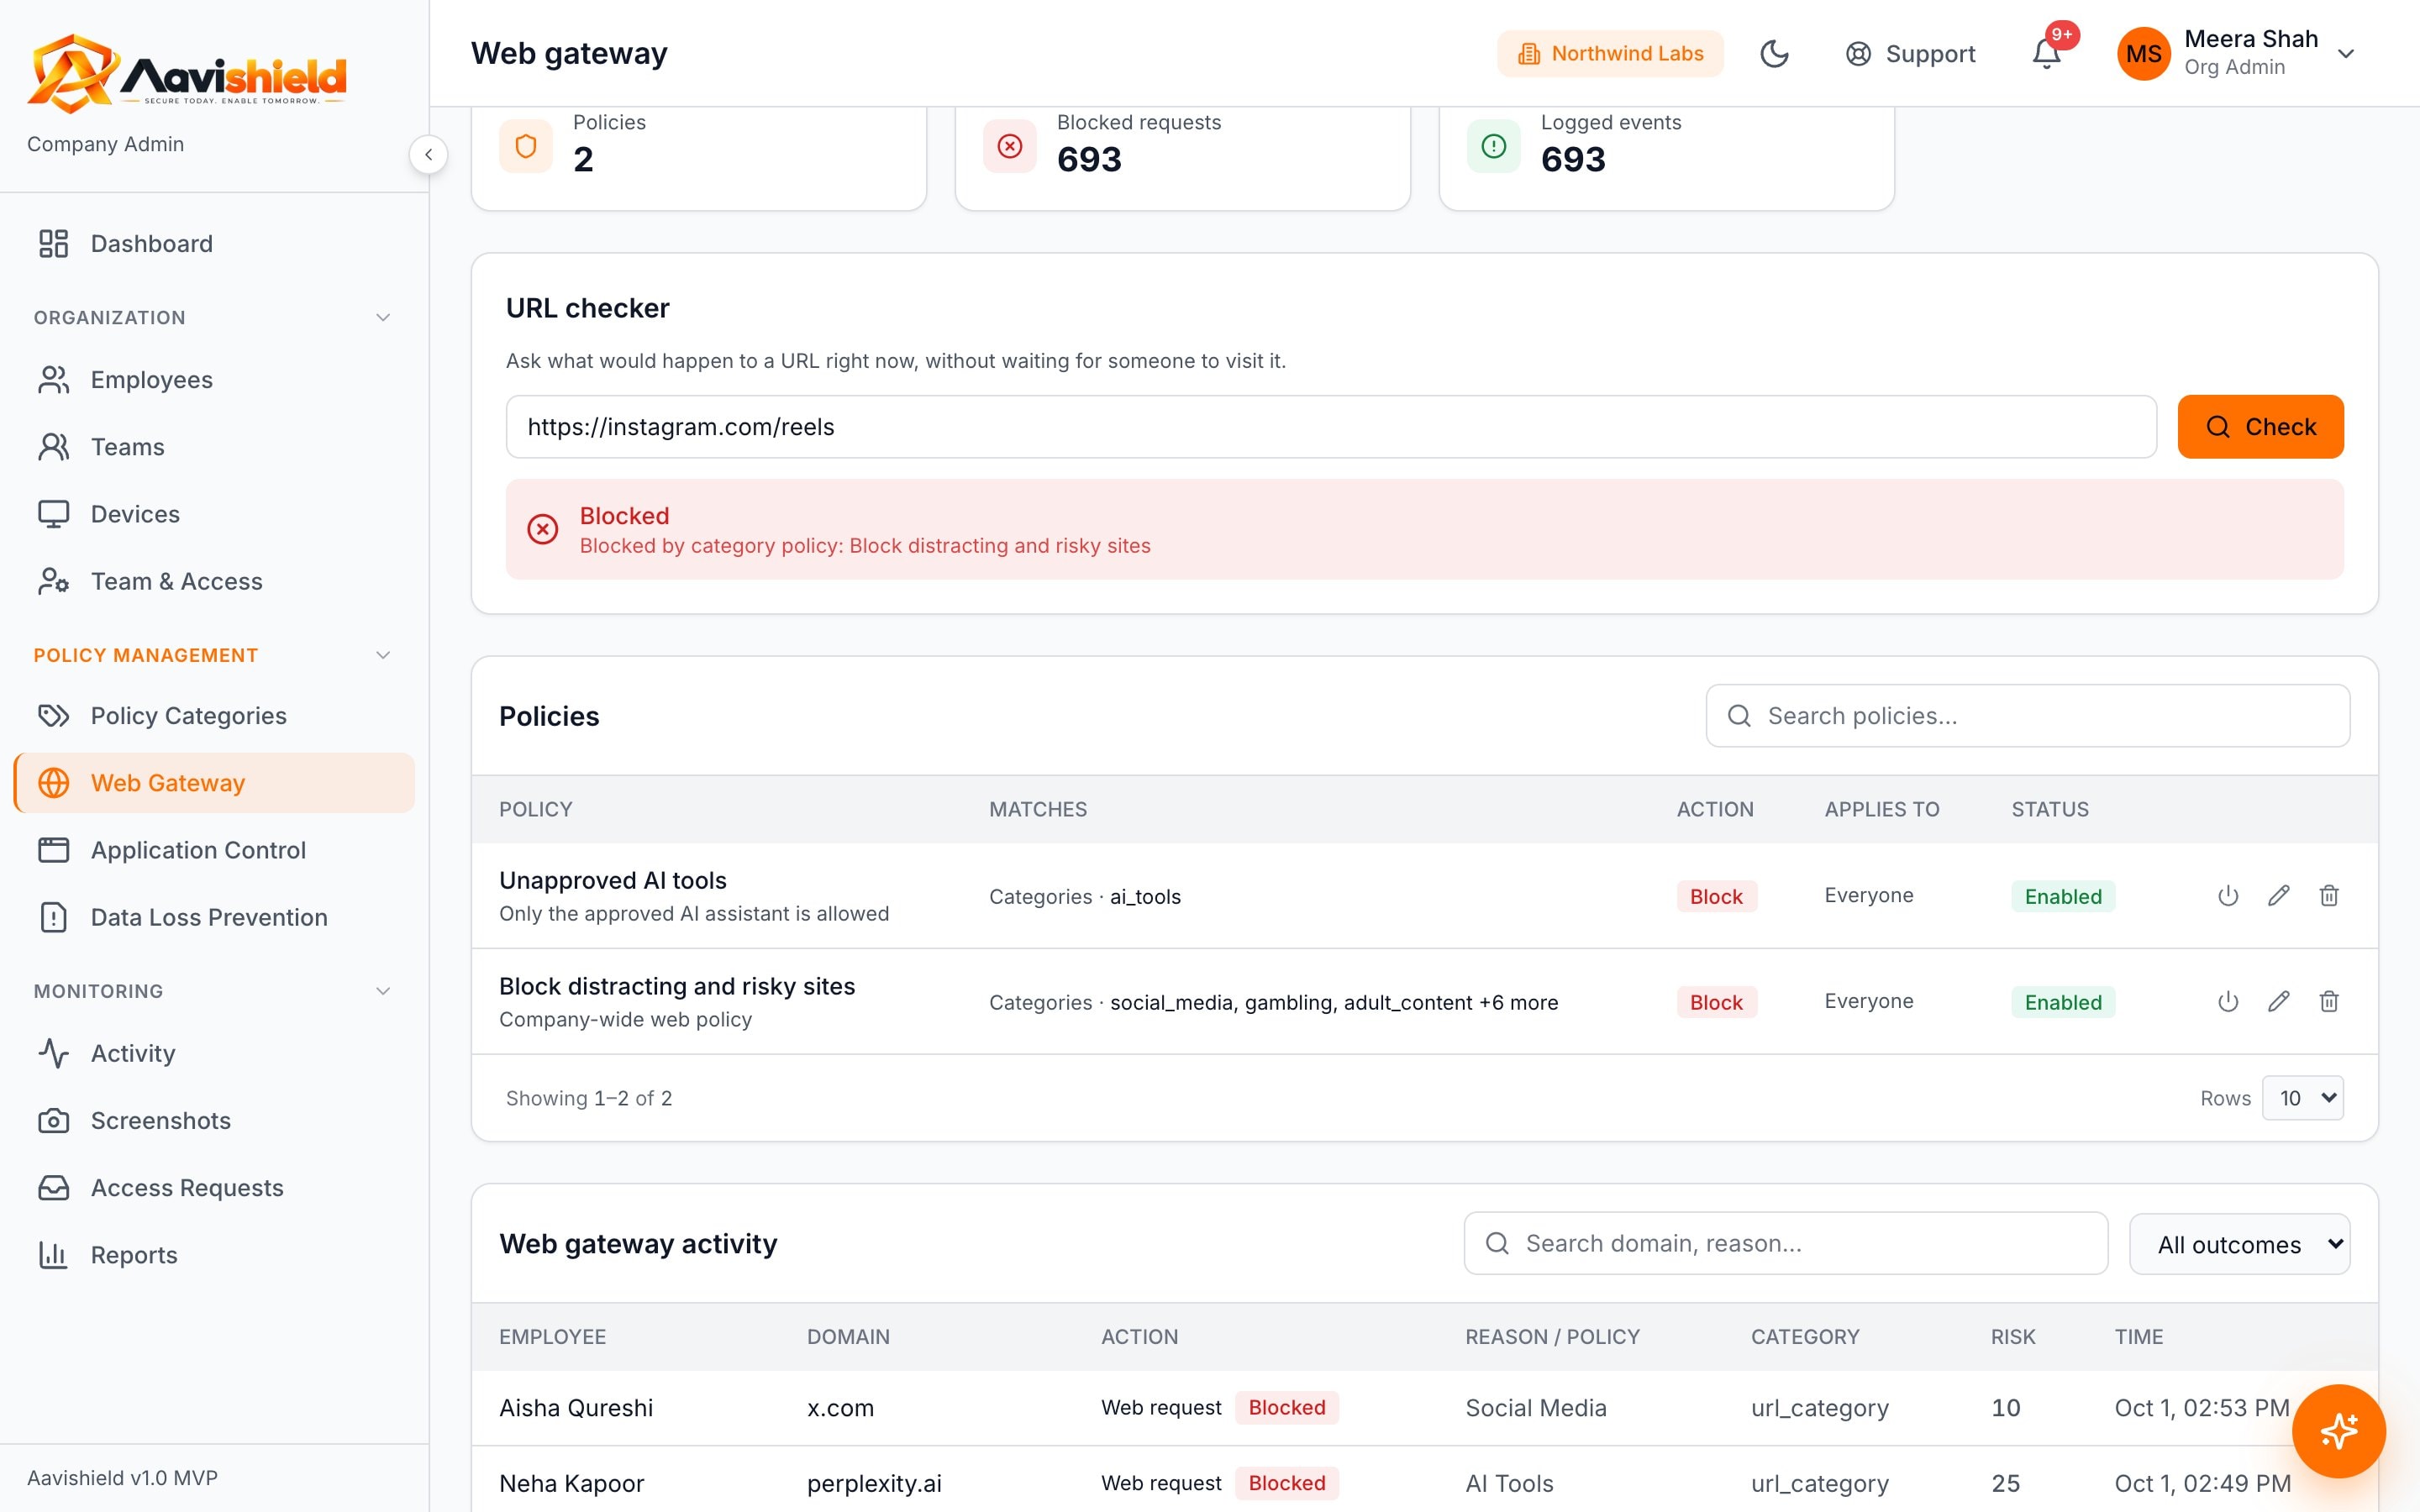
Type any address to see what would happen to it and which policy decides, before an employee asks.
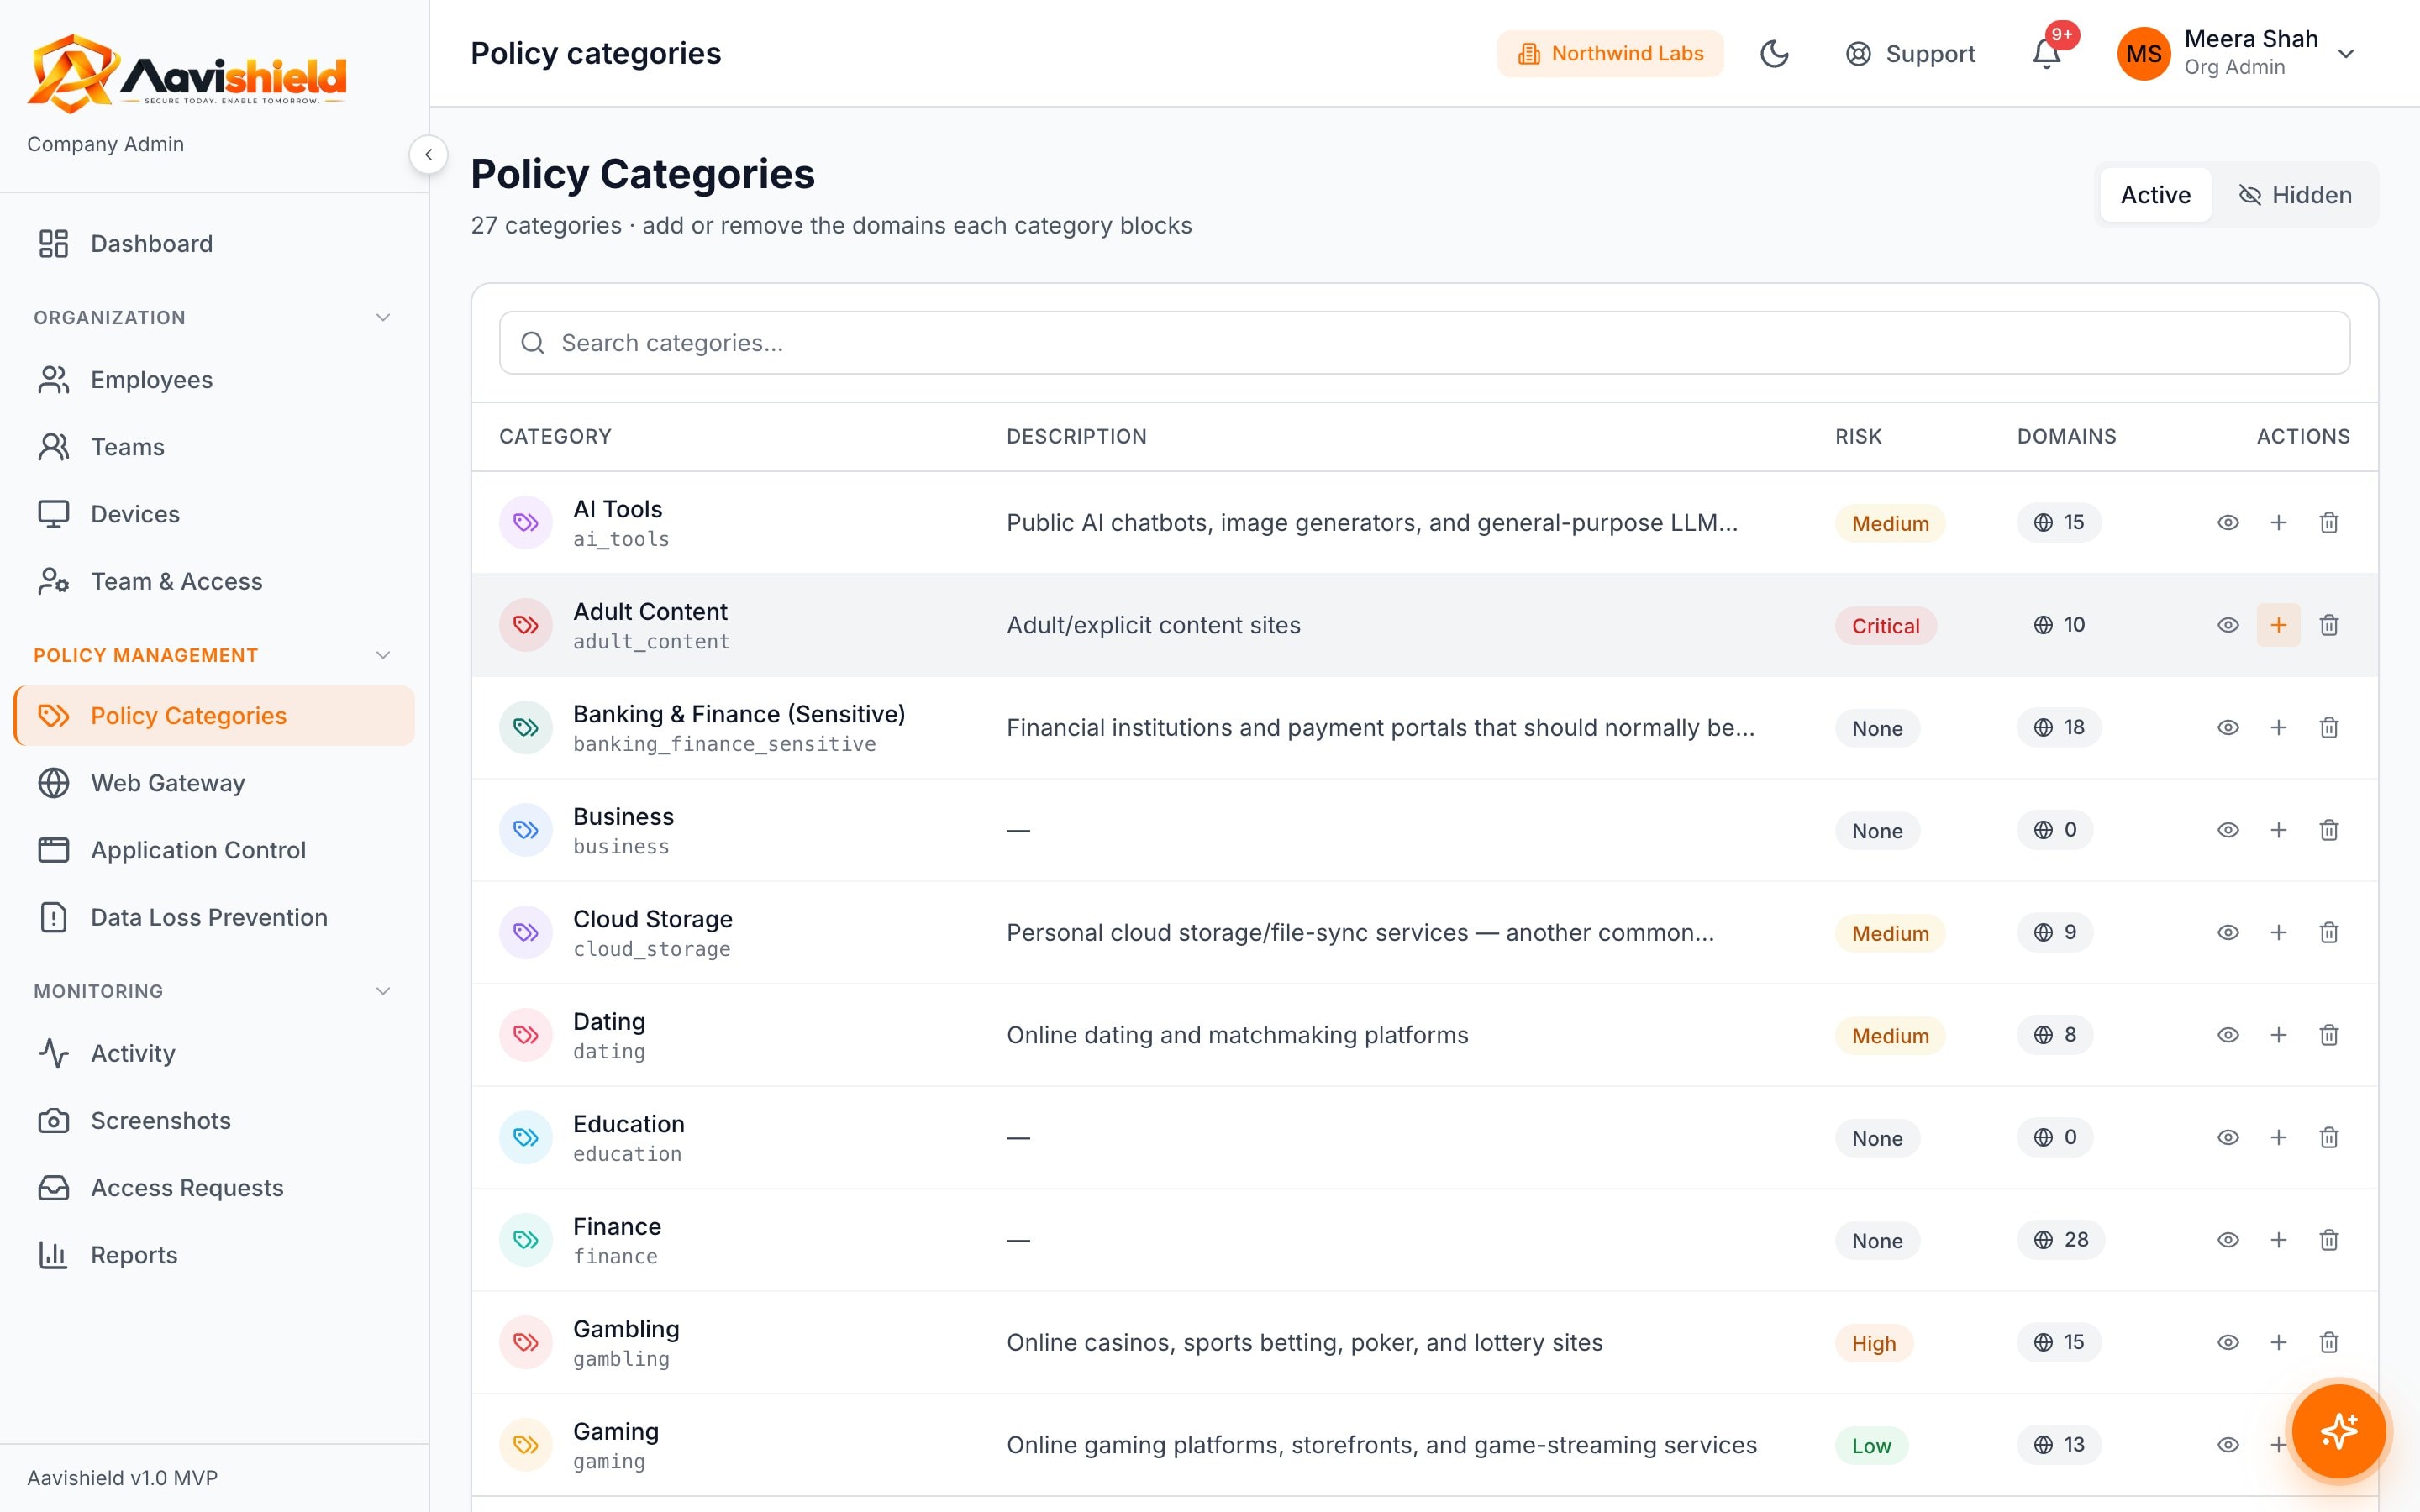
27 ready-made categories with their risk level and domain count. Add your own domains or hide categories you never use.
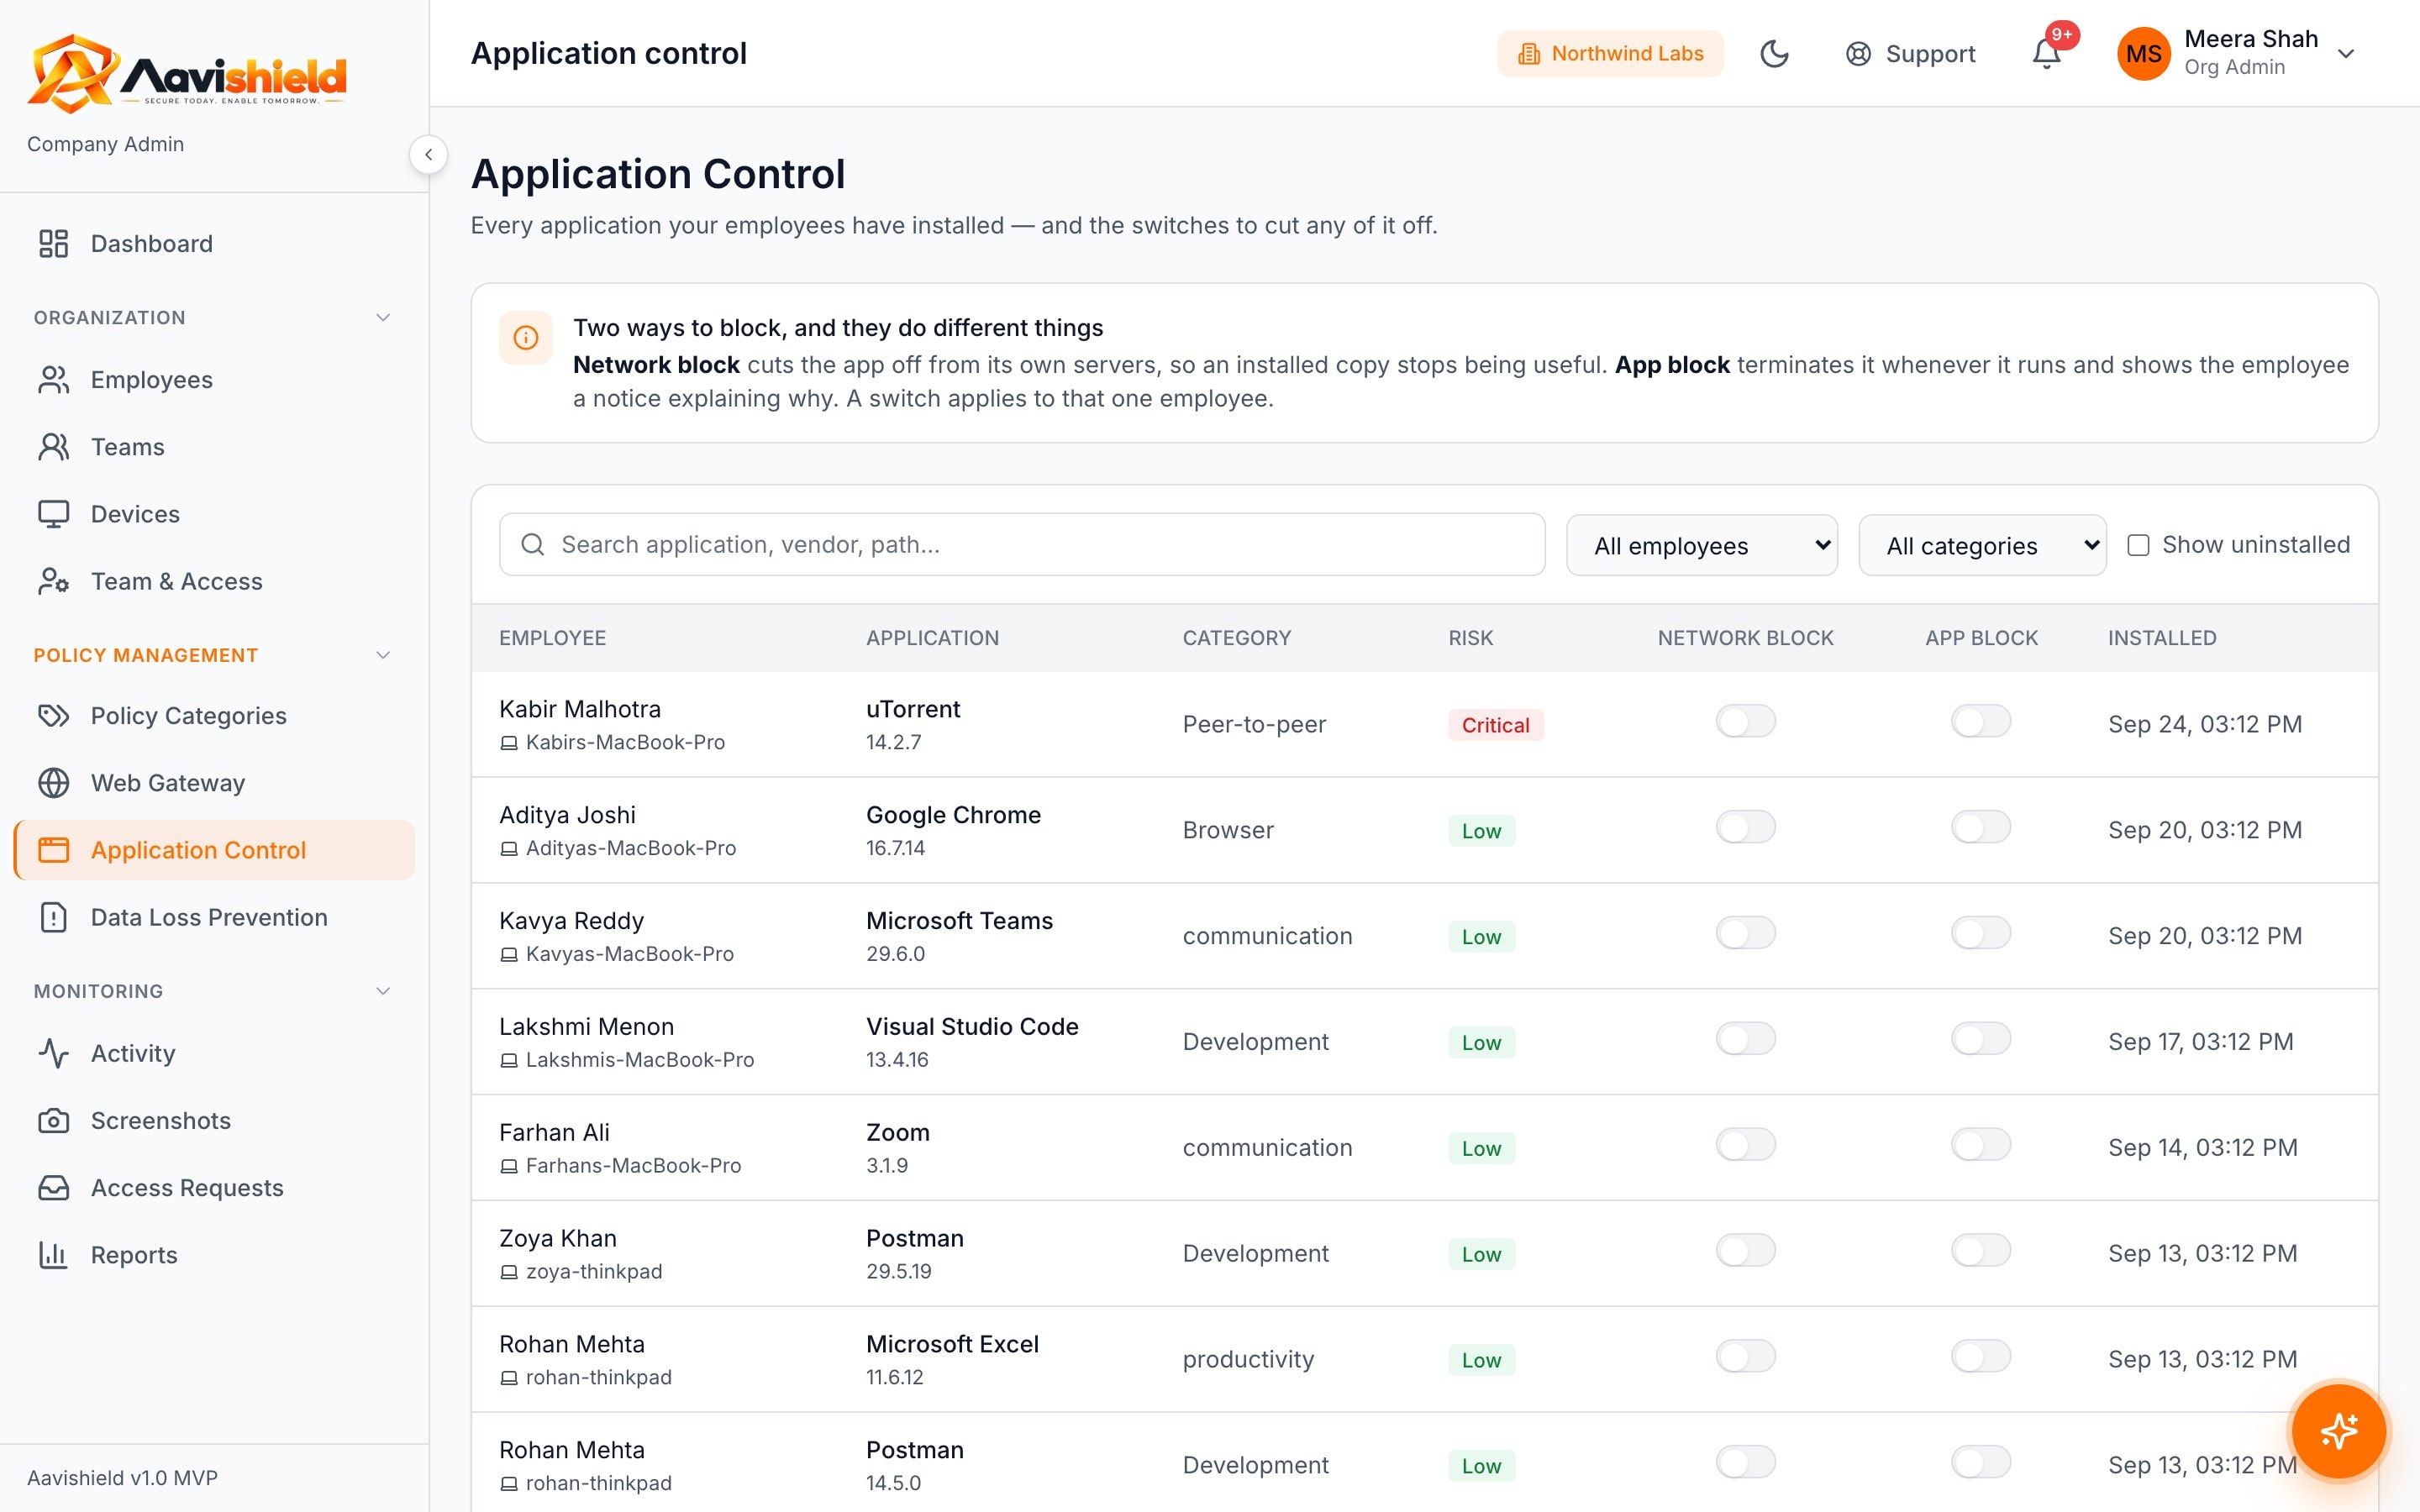
Every installed application across the fleet, with a network block and an app block switch for each.
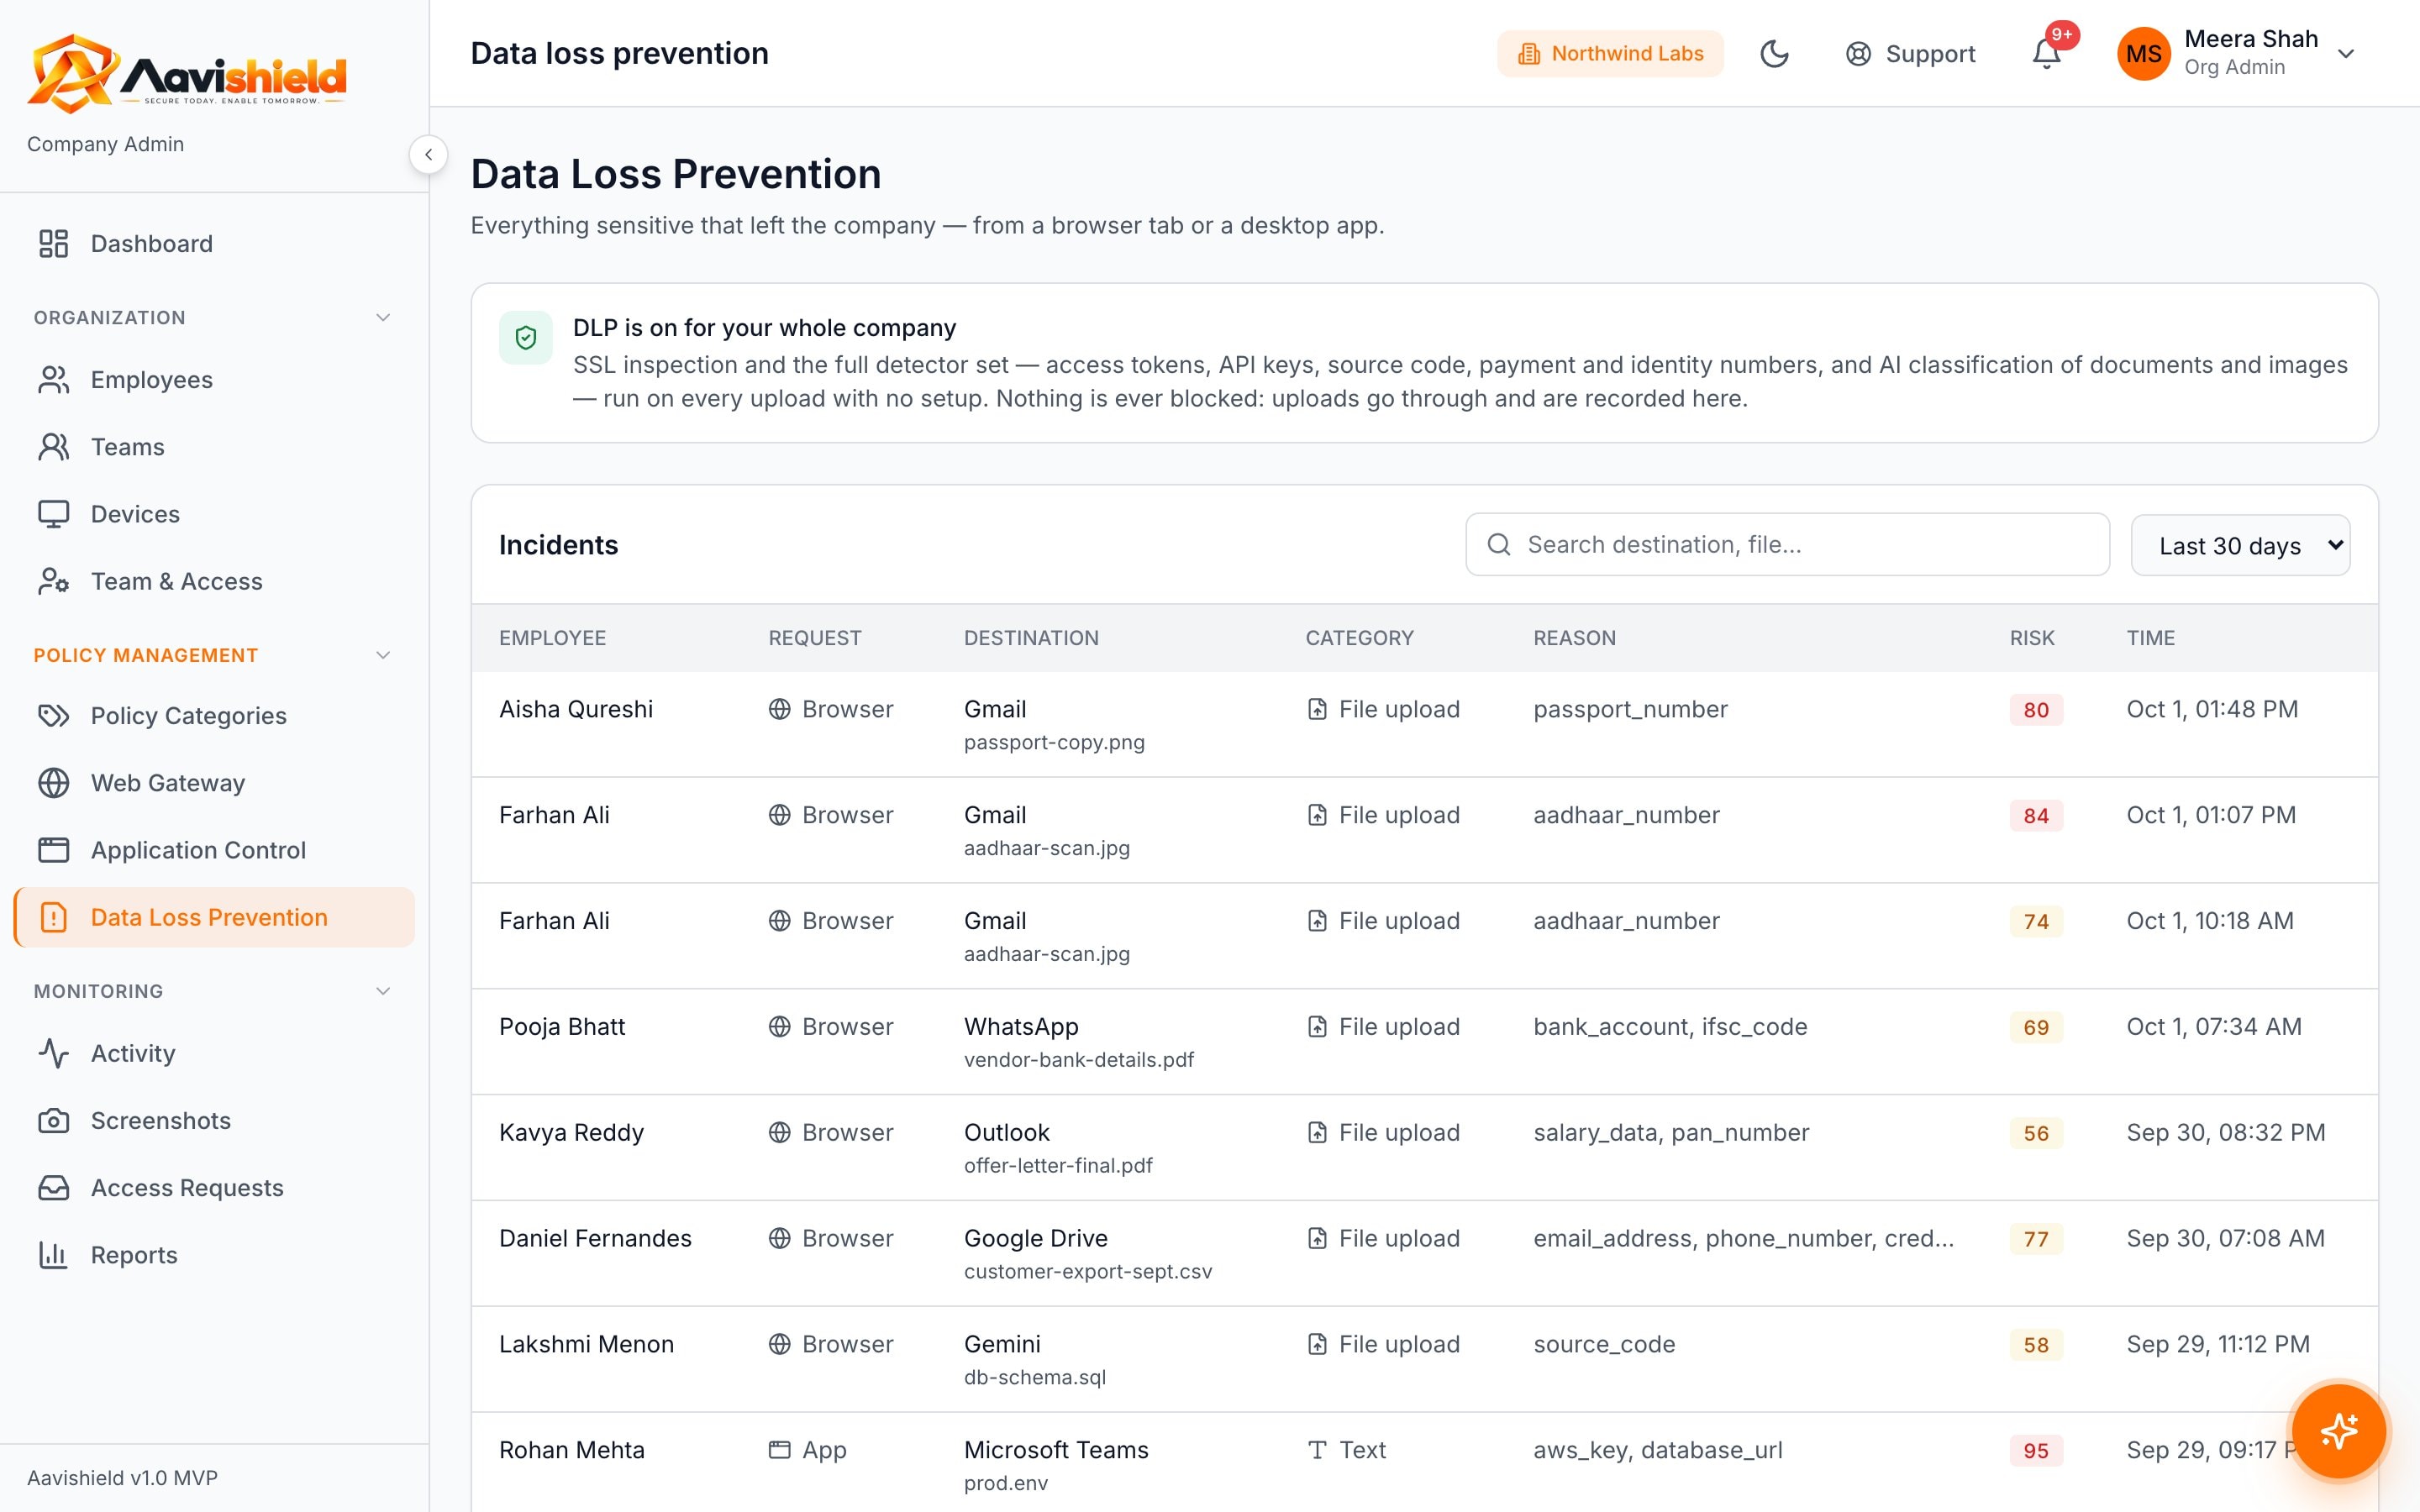
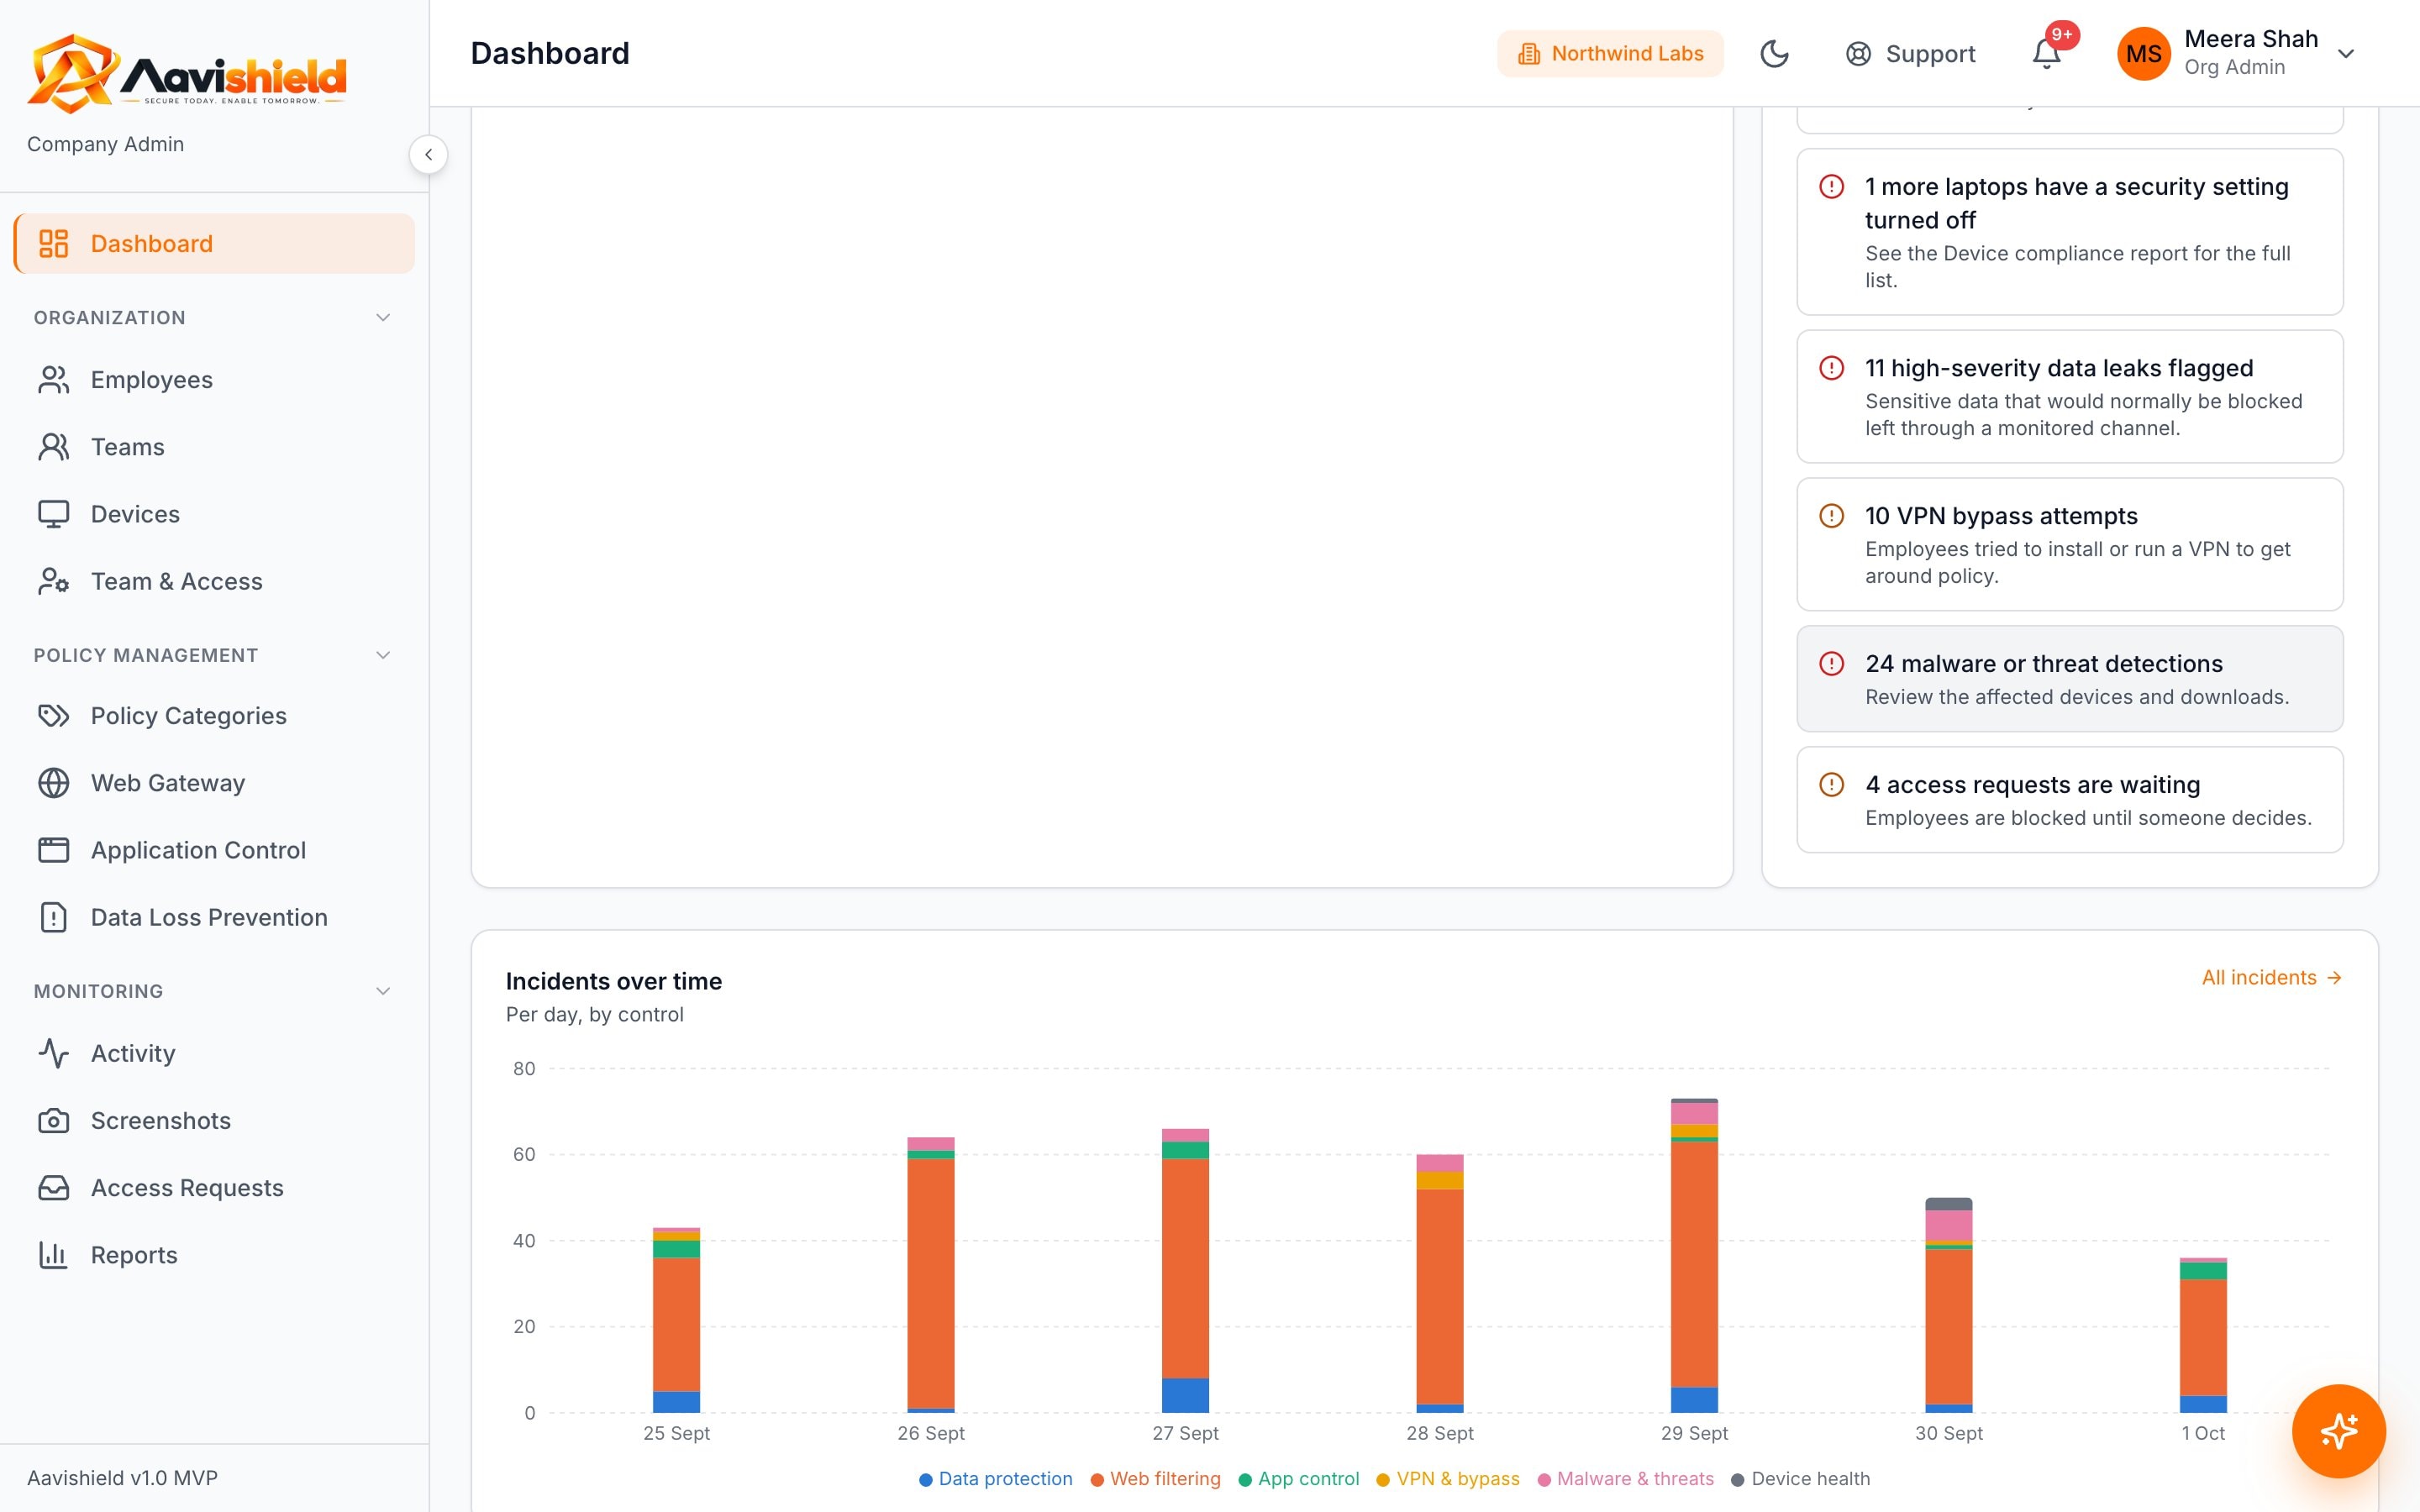
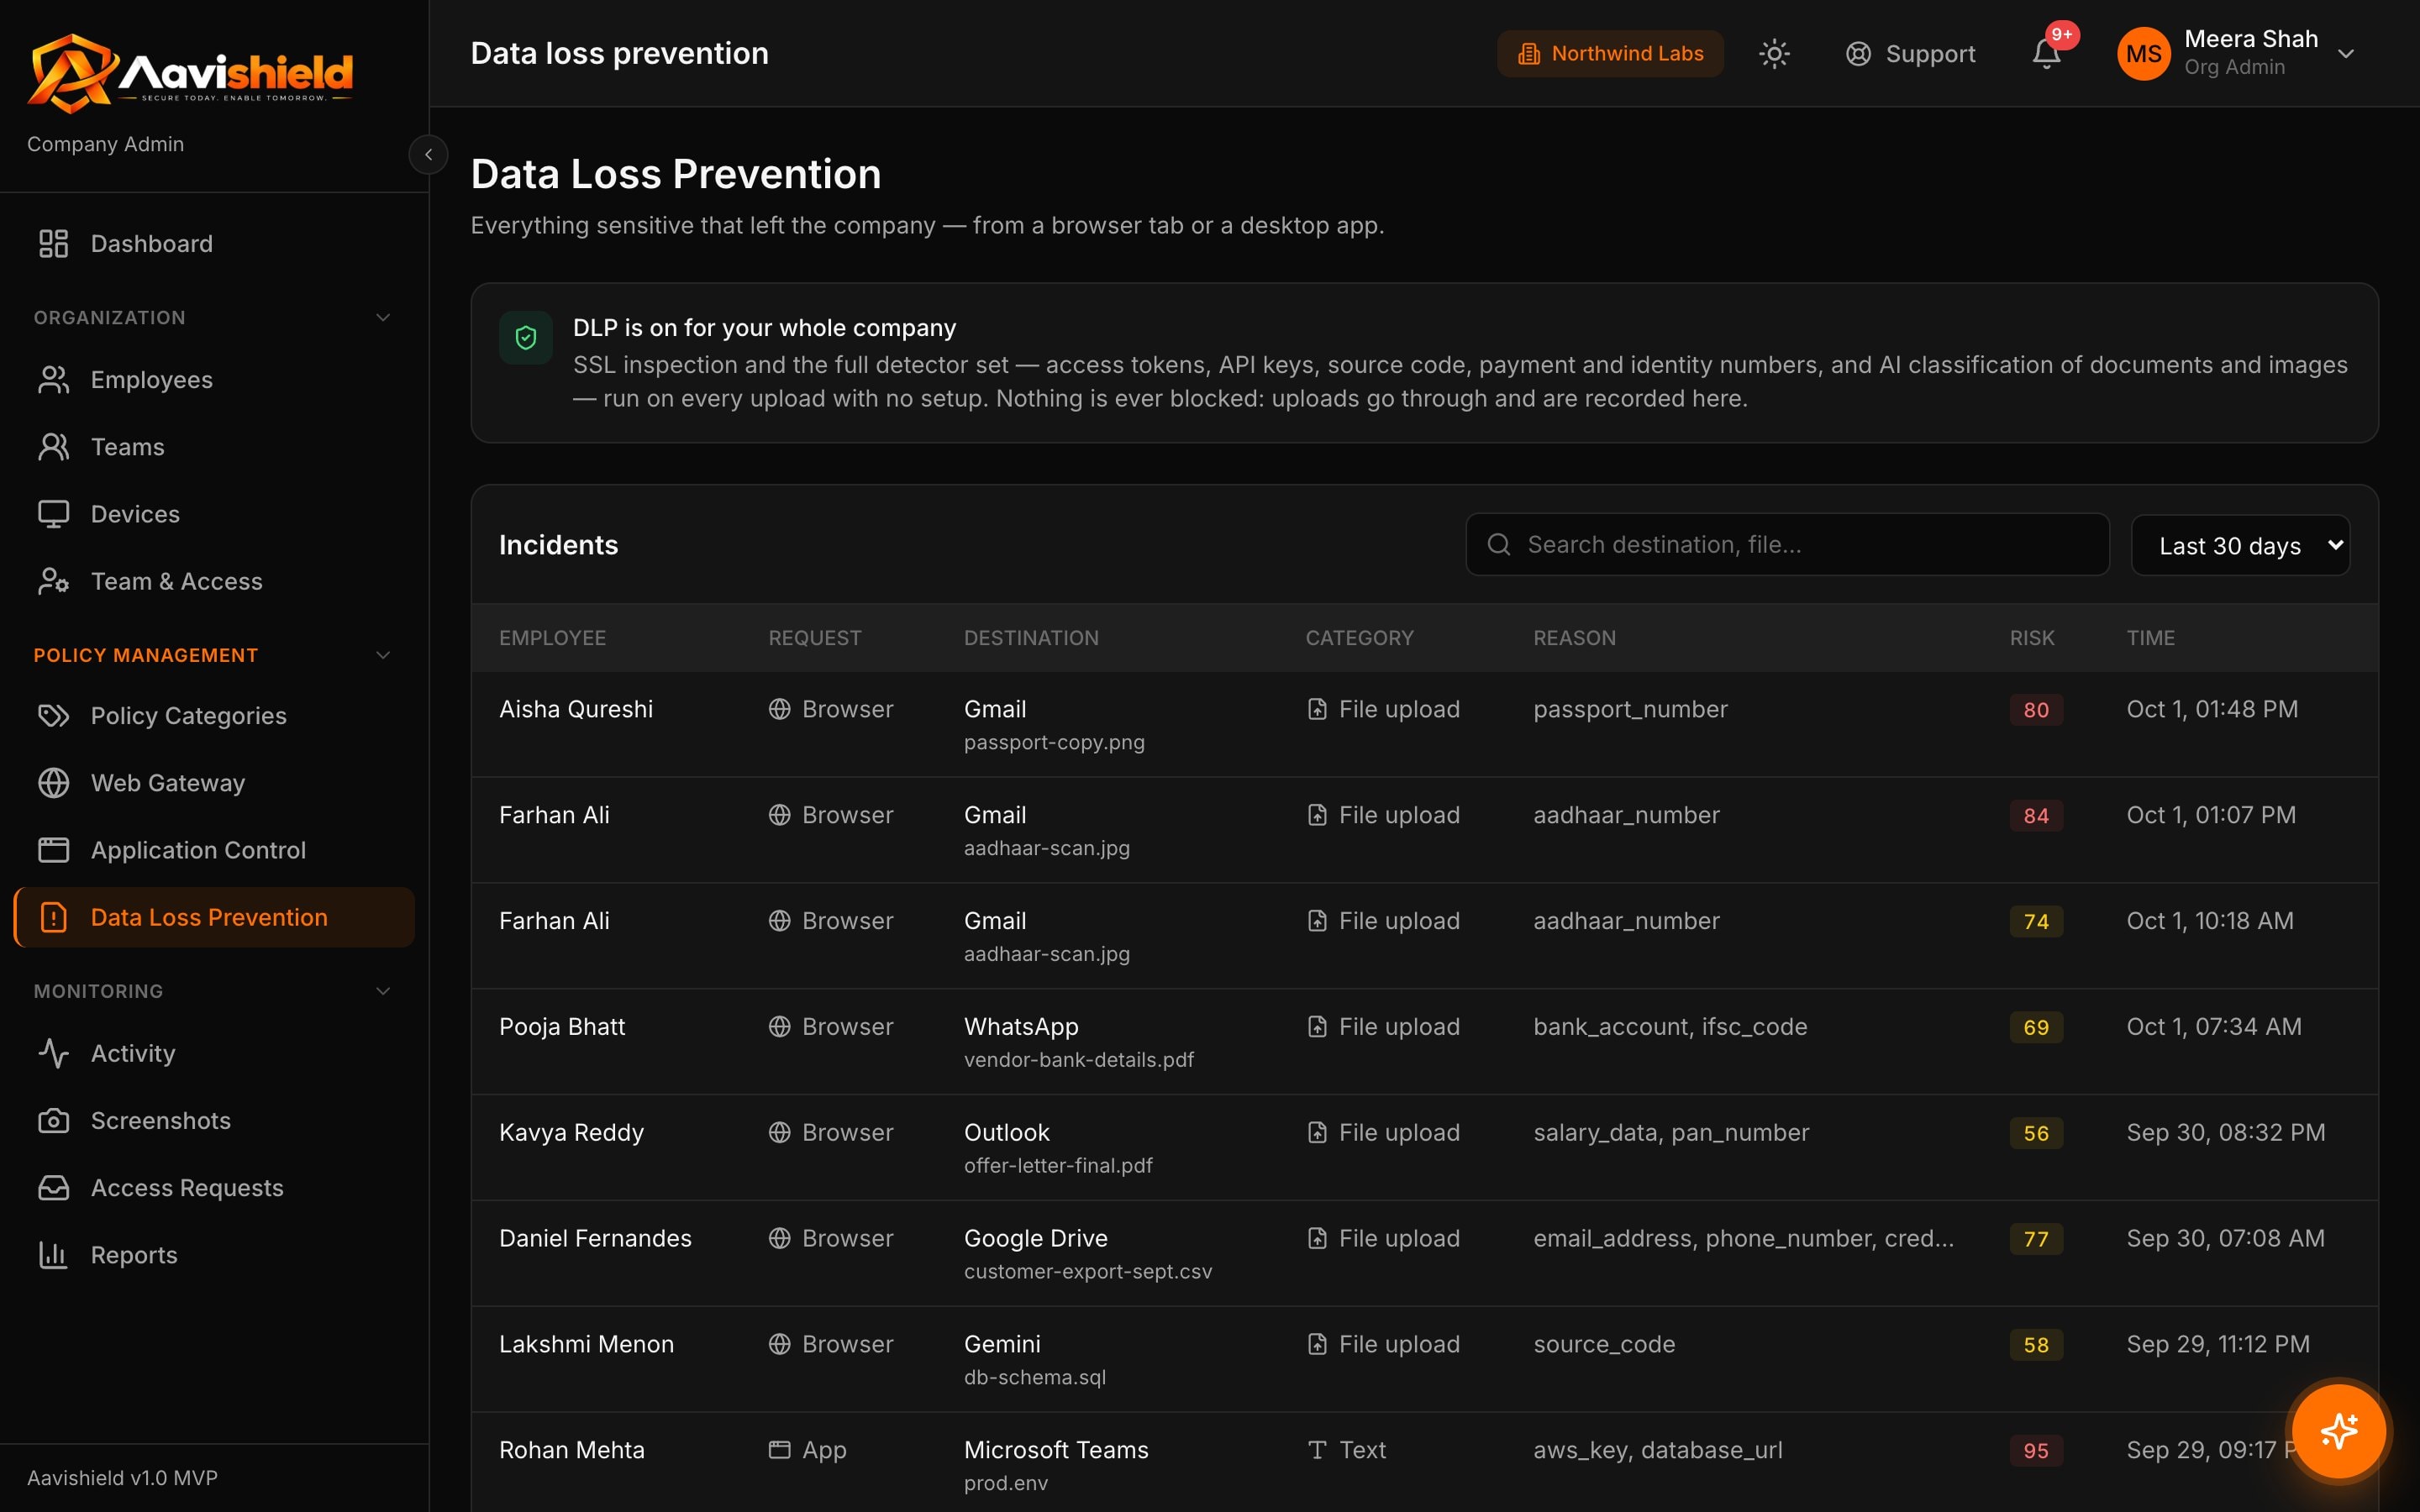
Sensitive data leaving, malicious downloads stopped and devices drifting out of compliance.
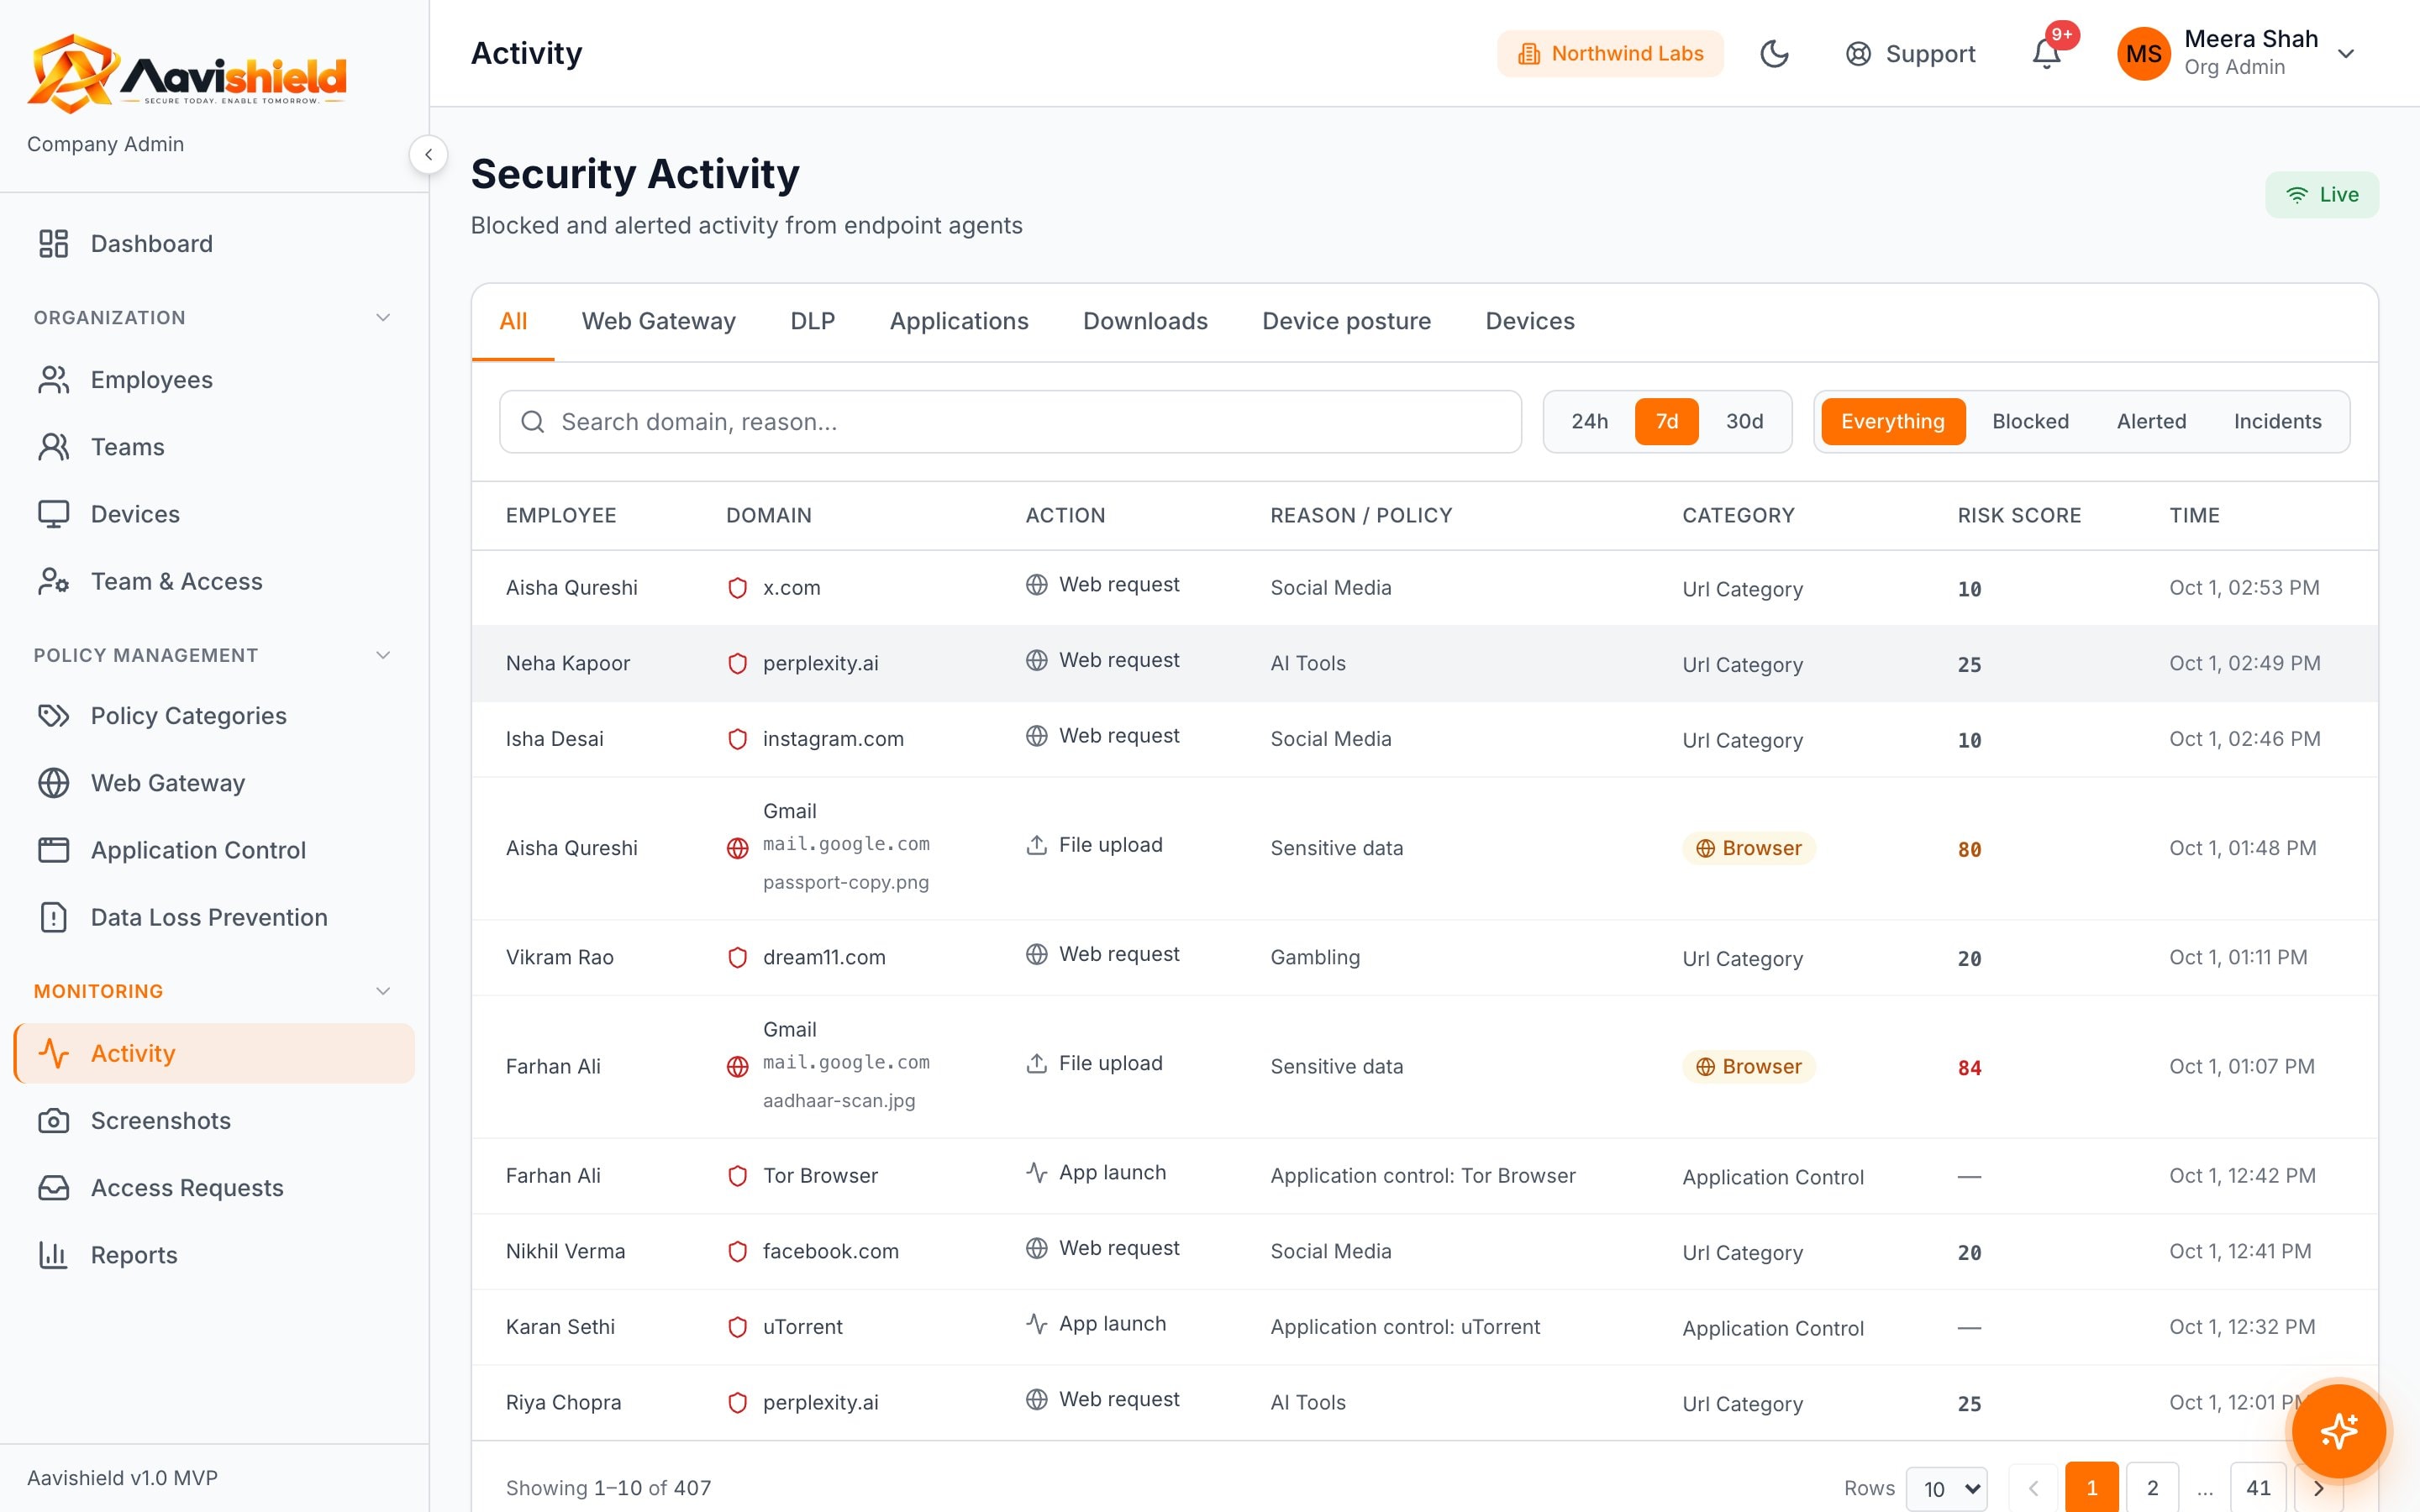
Each incident shows the employee, browser or app, destination, file or text, the detectors that matched and a risk score.
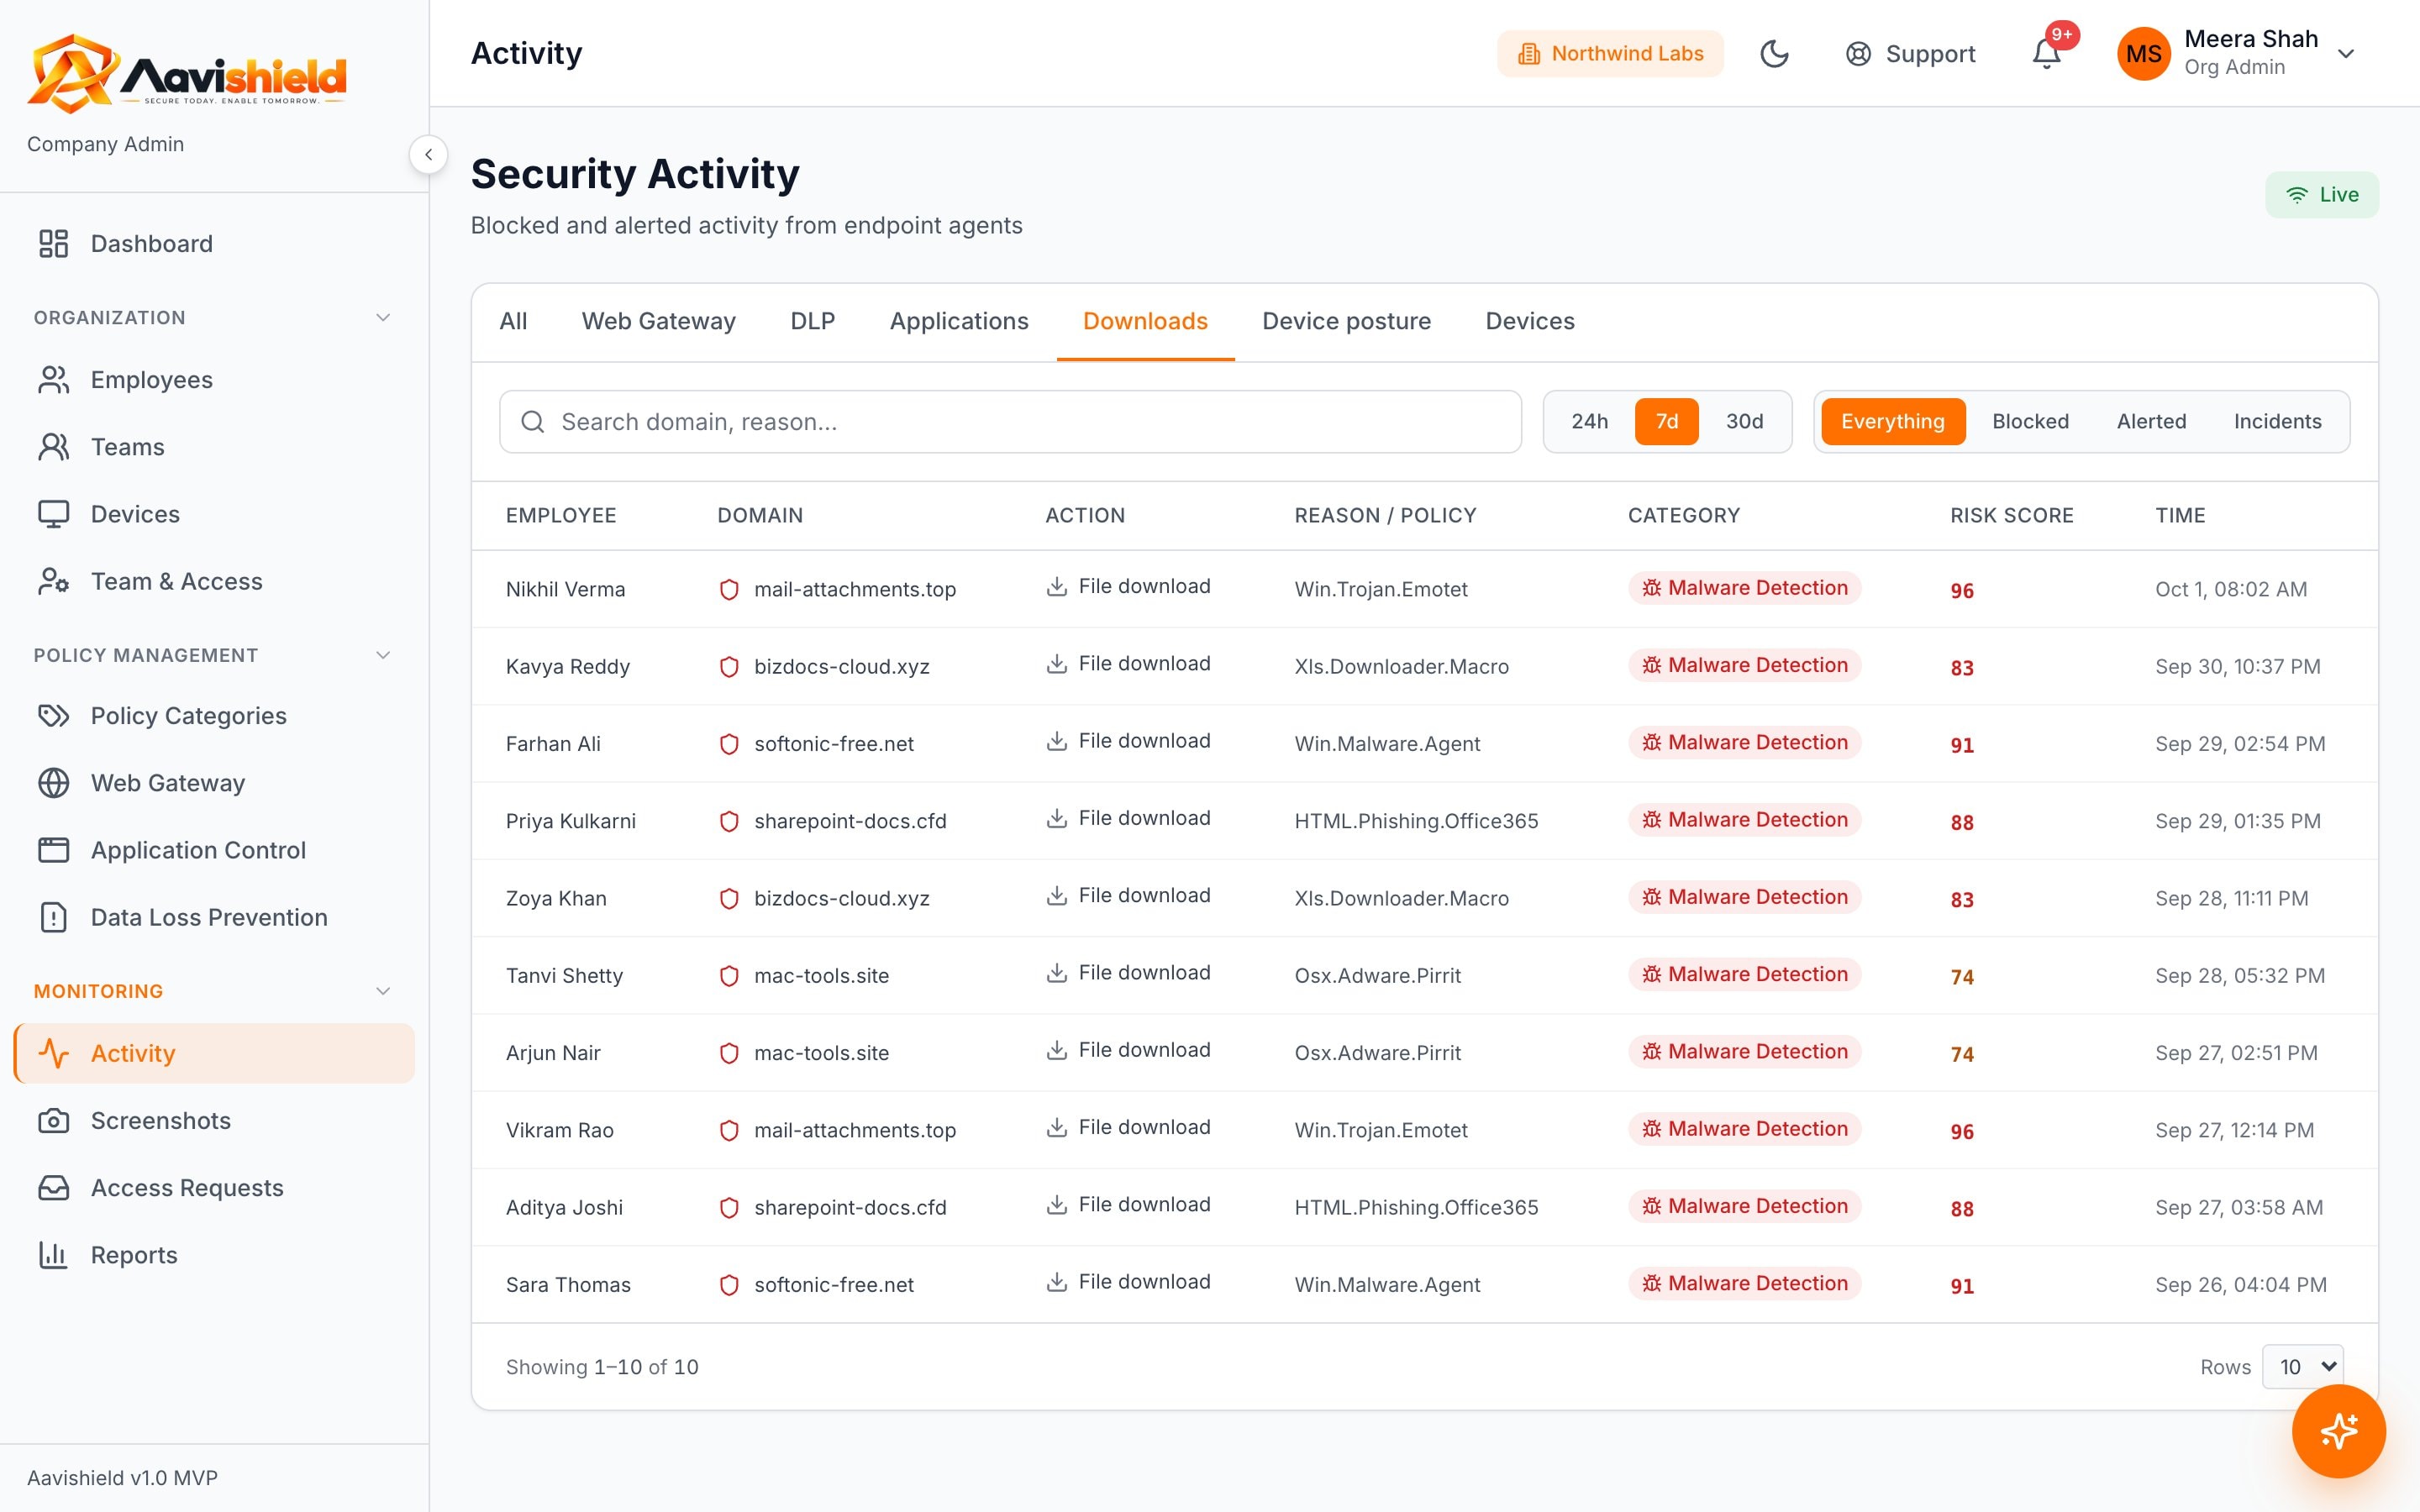
Malicious files stopped in flight, with the source domain, signature and risk score.
Devices with the firewall off, updates pending or encryption disabled, with plain-language fixes.
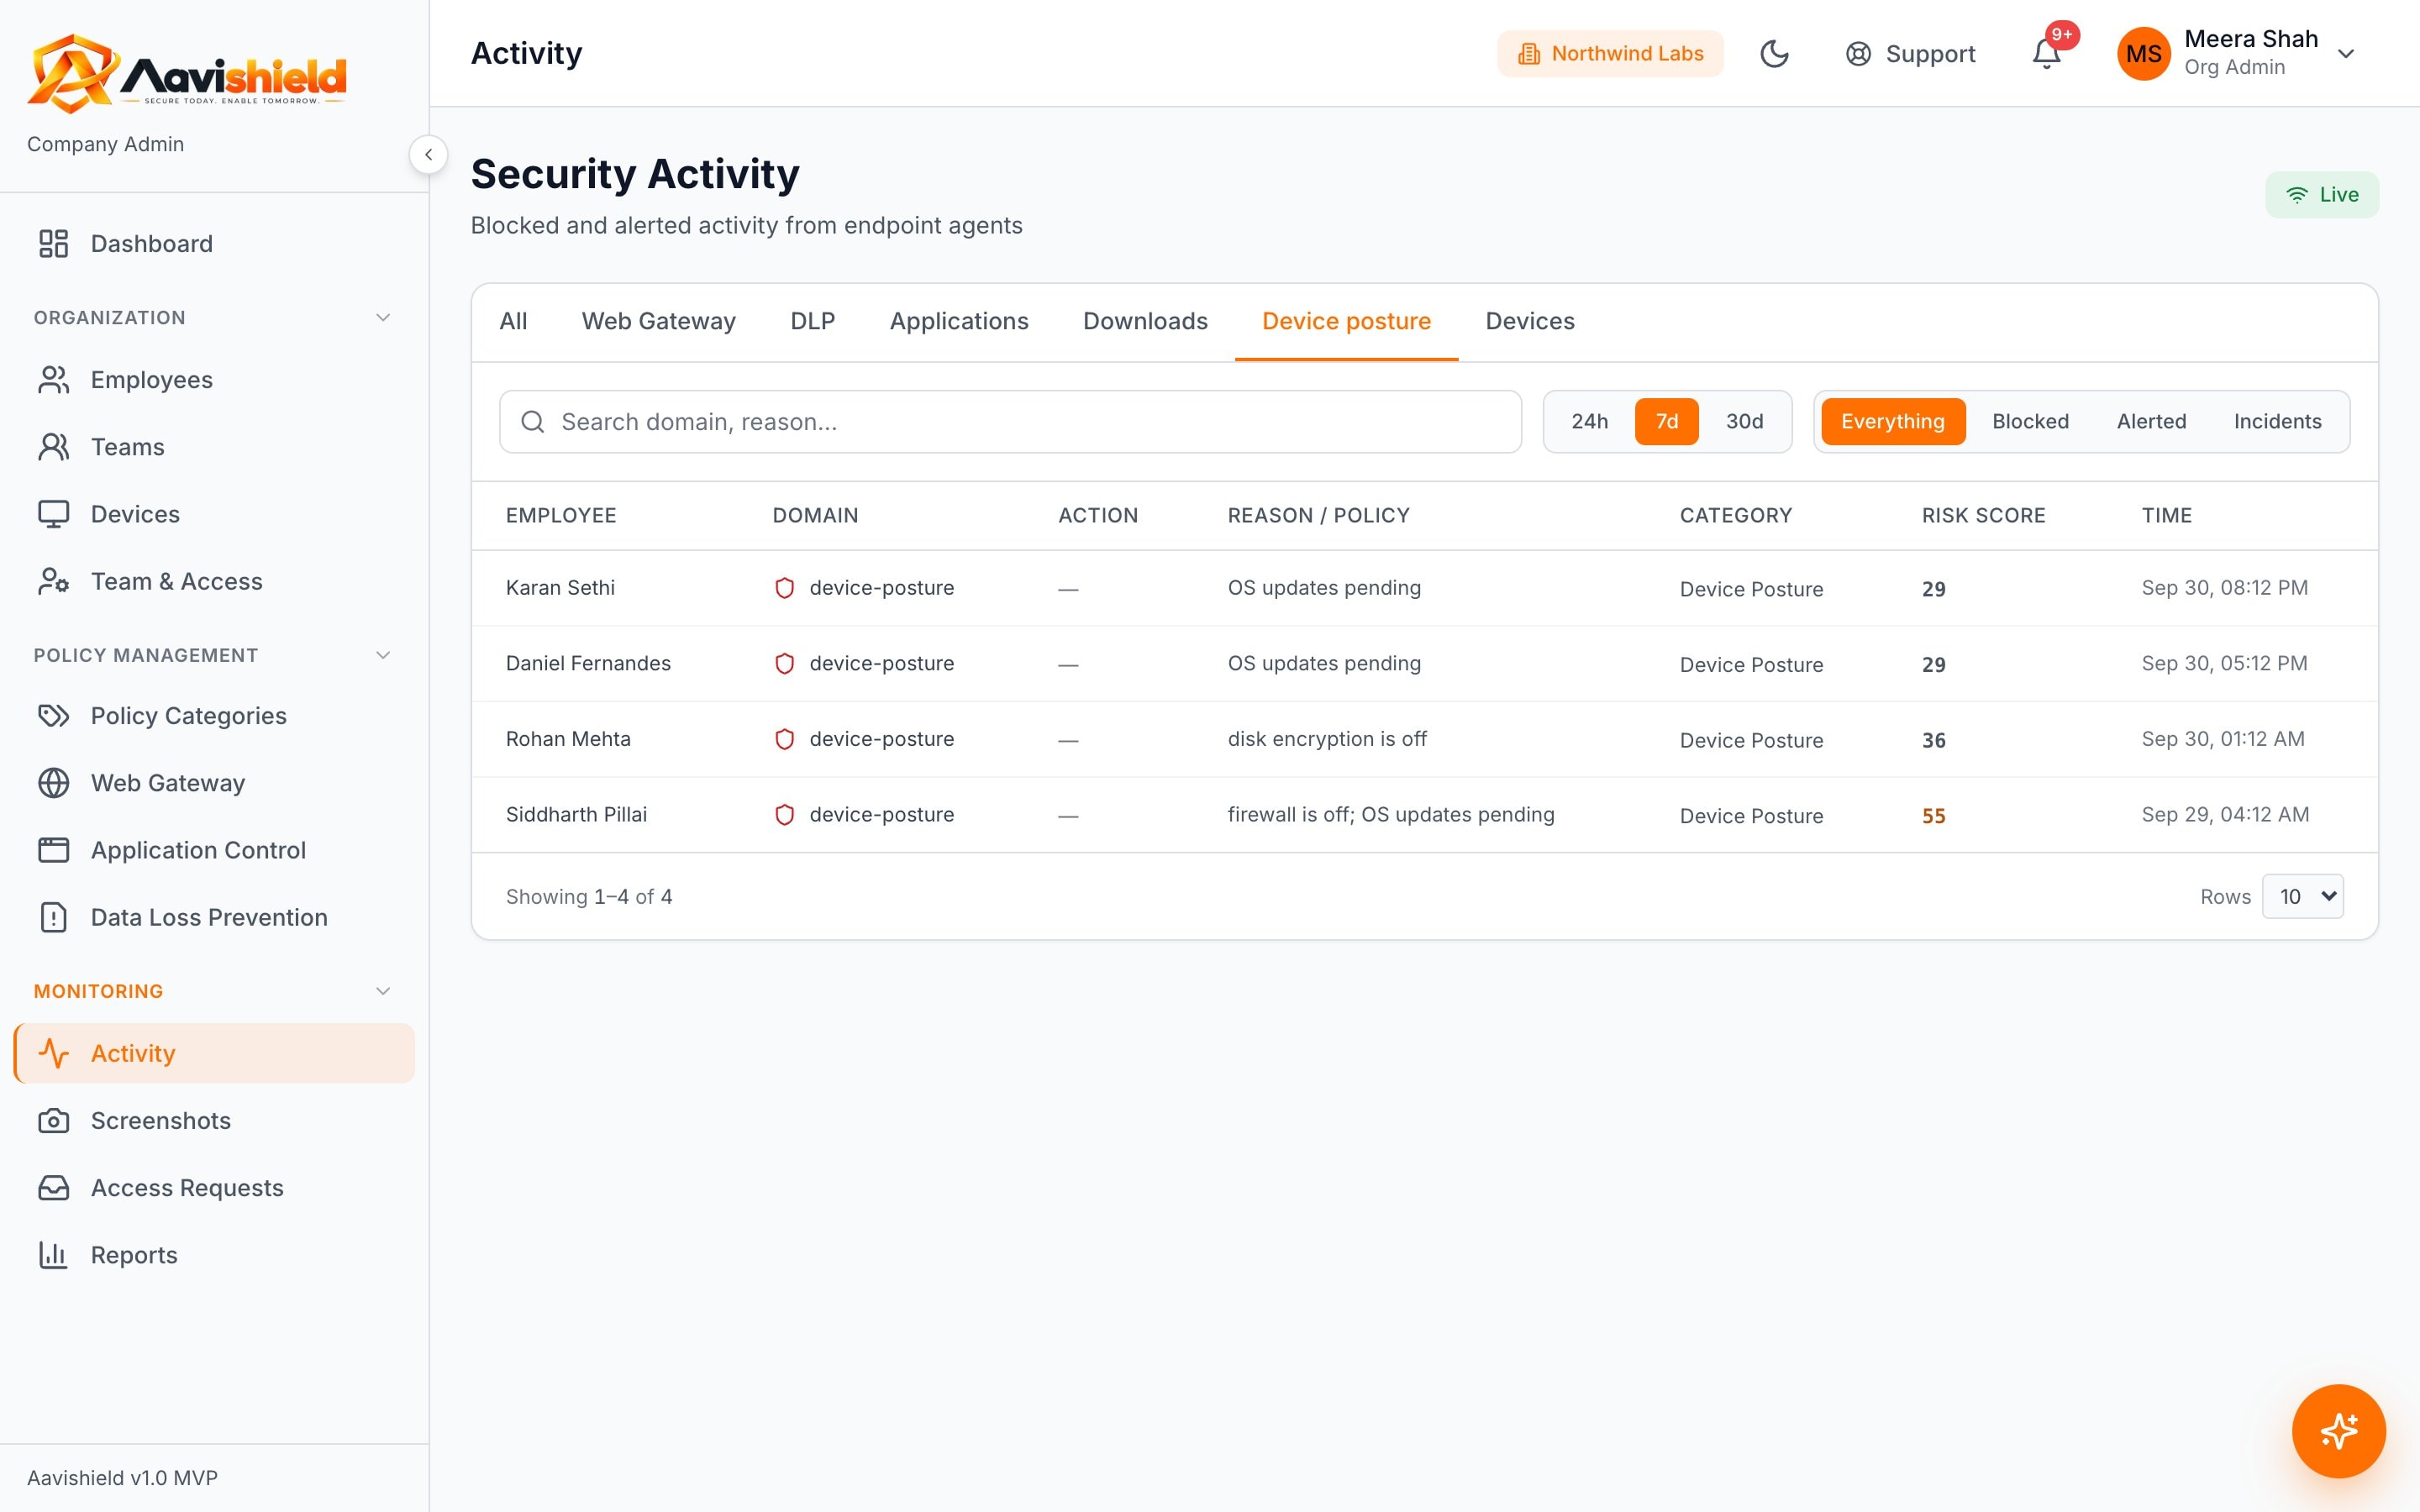
Everything the agents report, together, with the context to act.
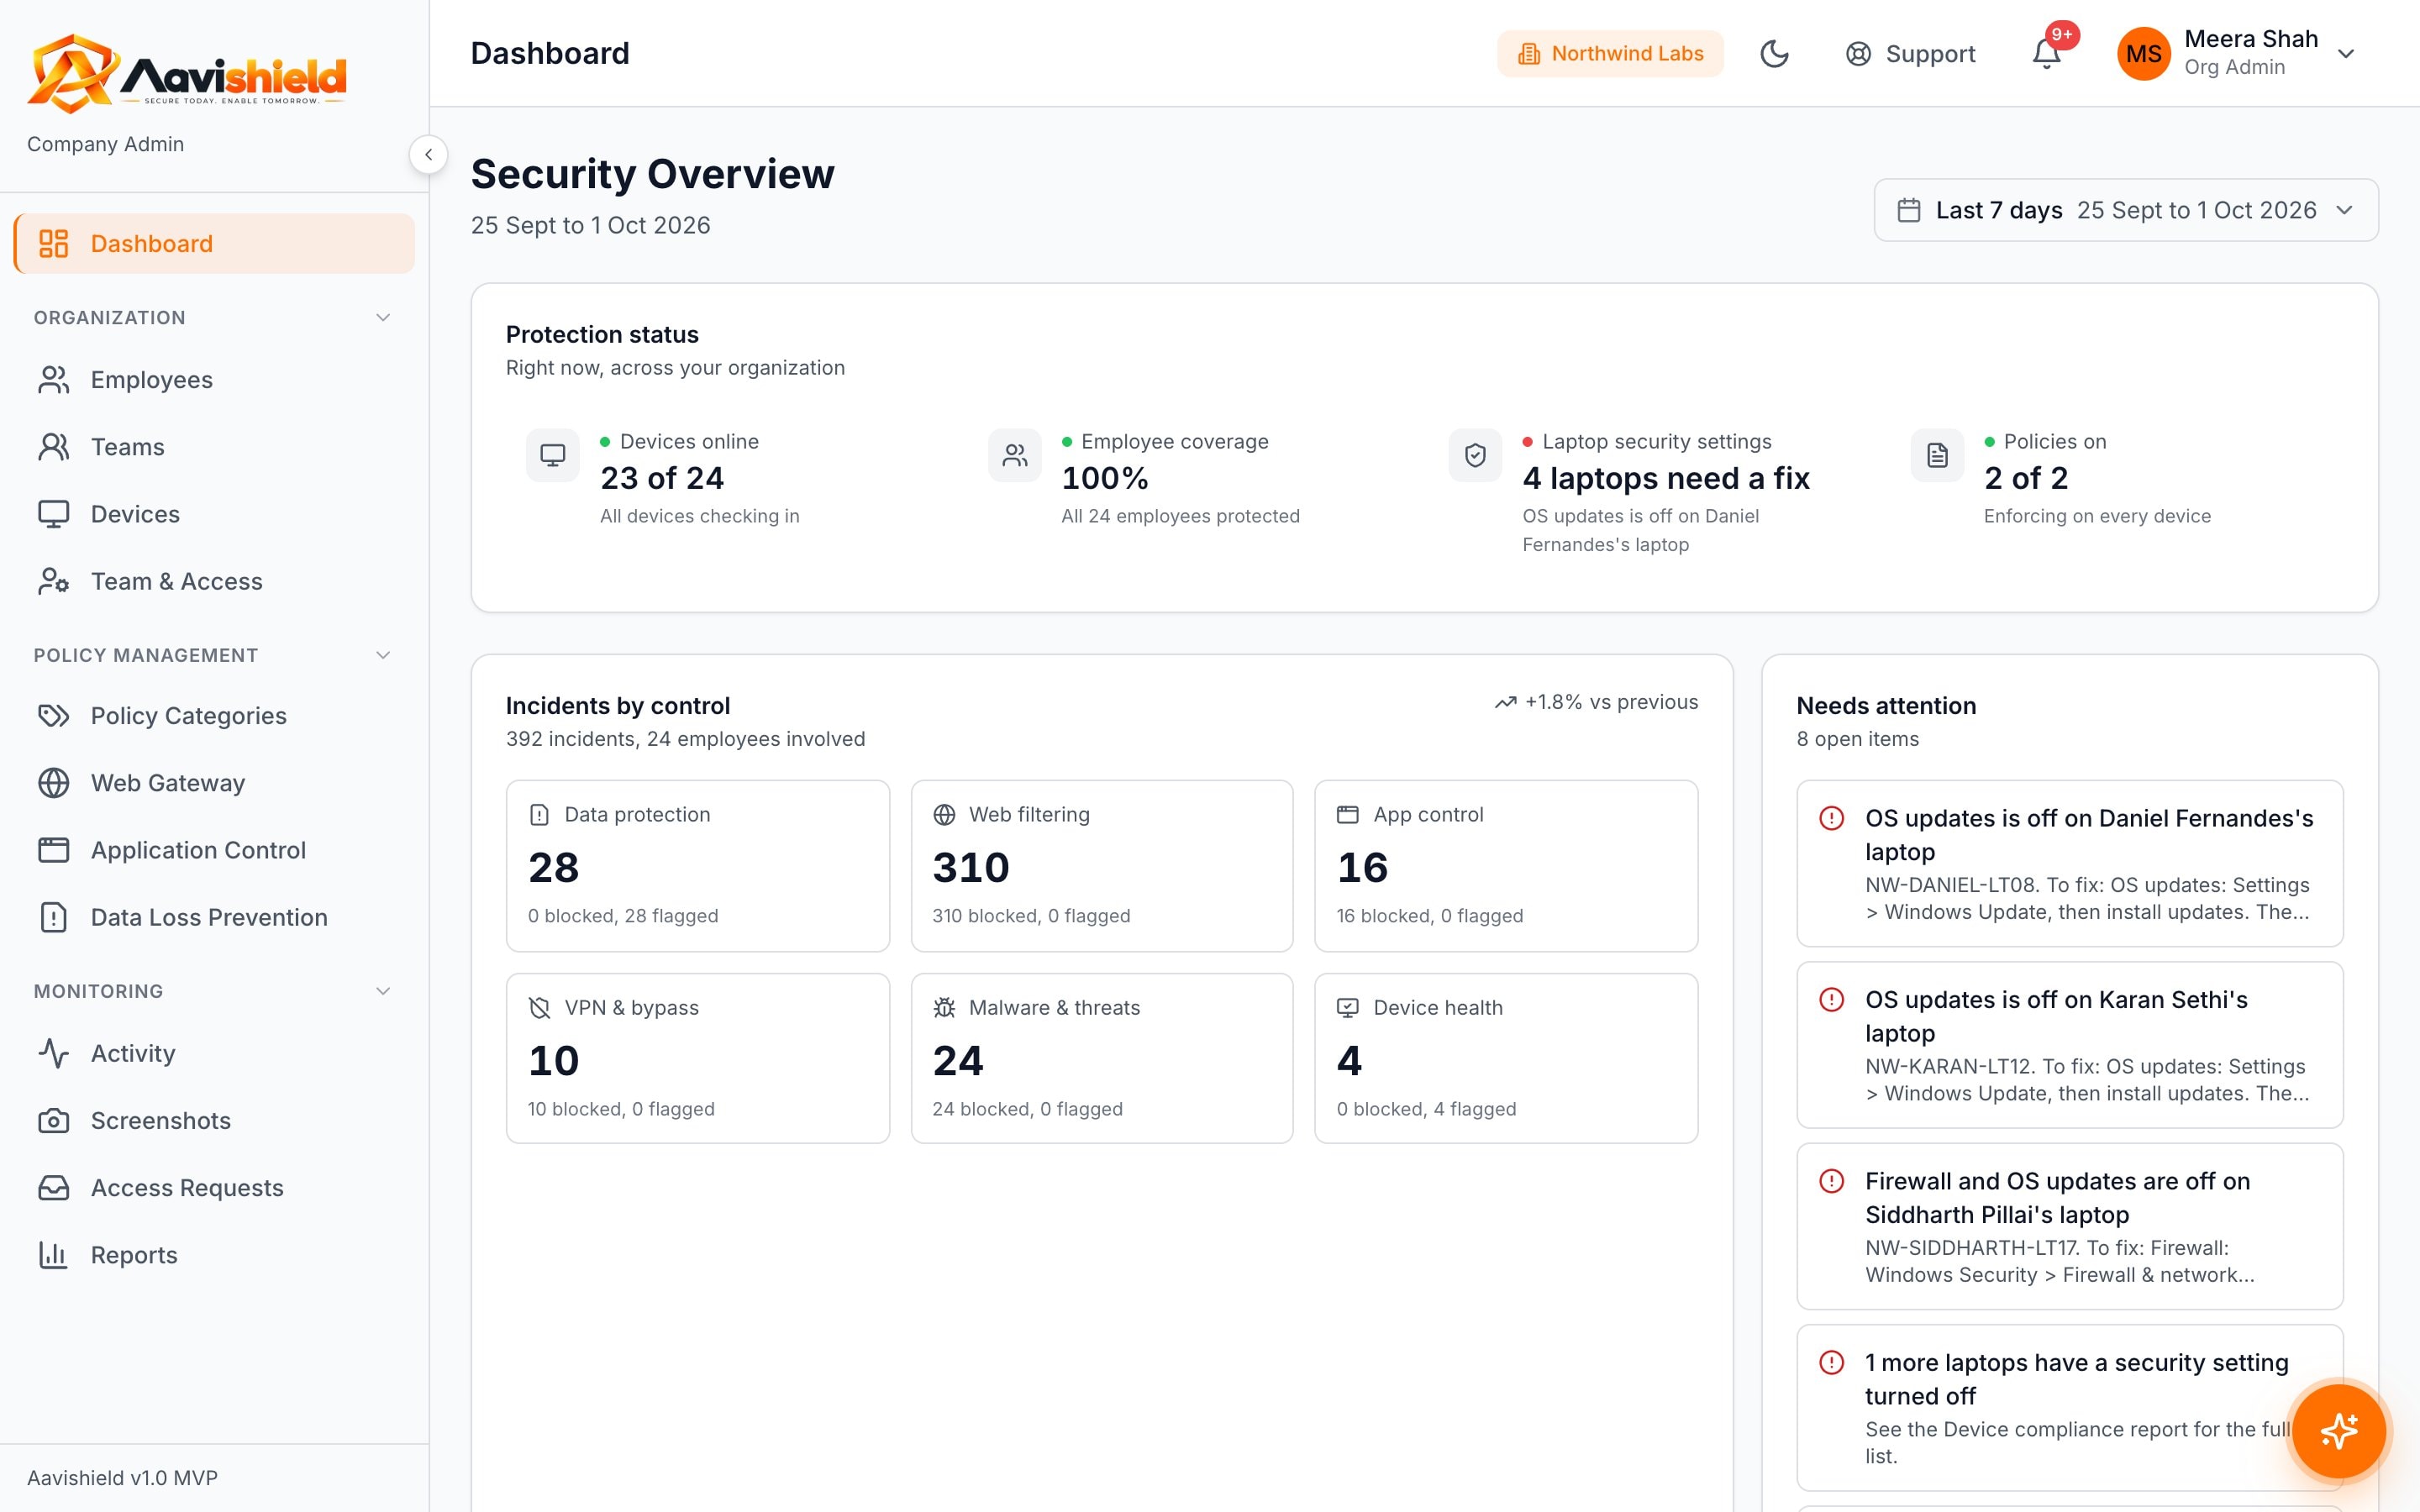
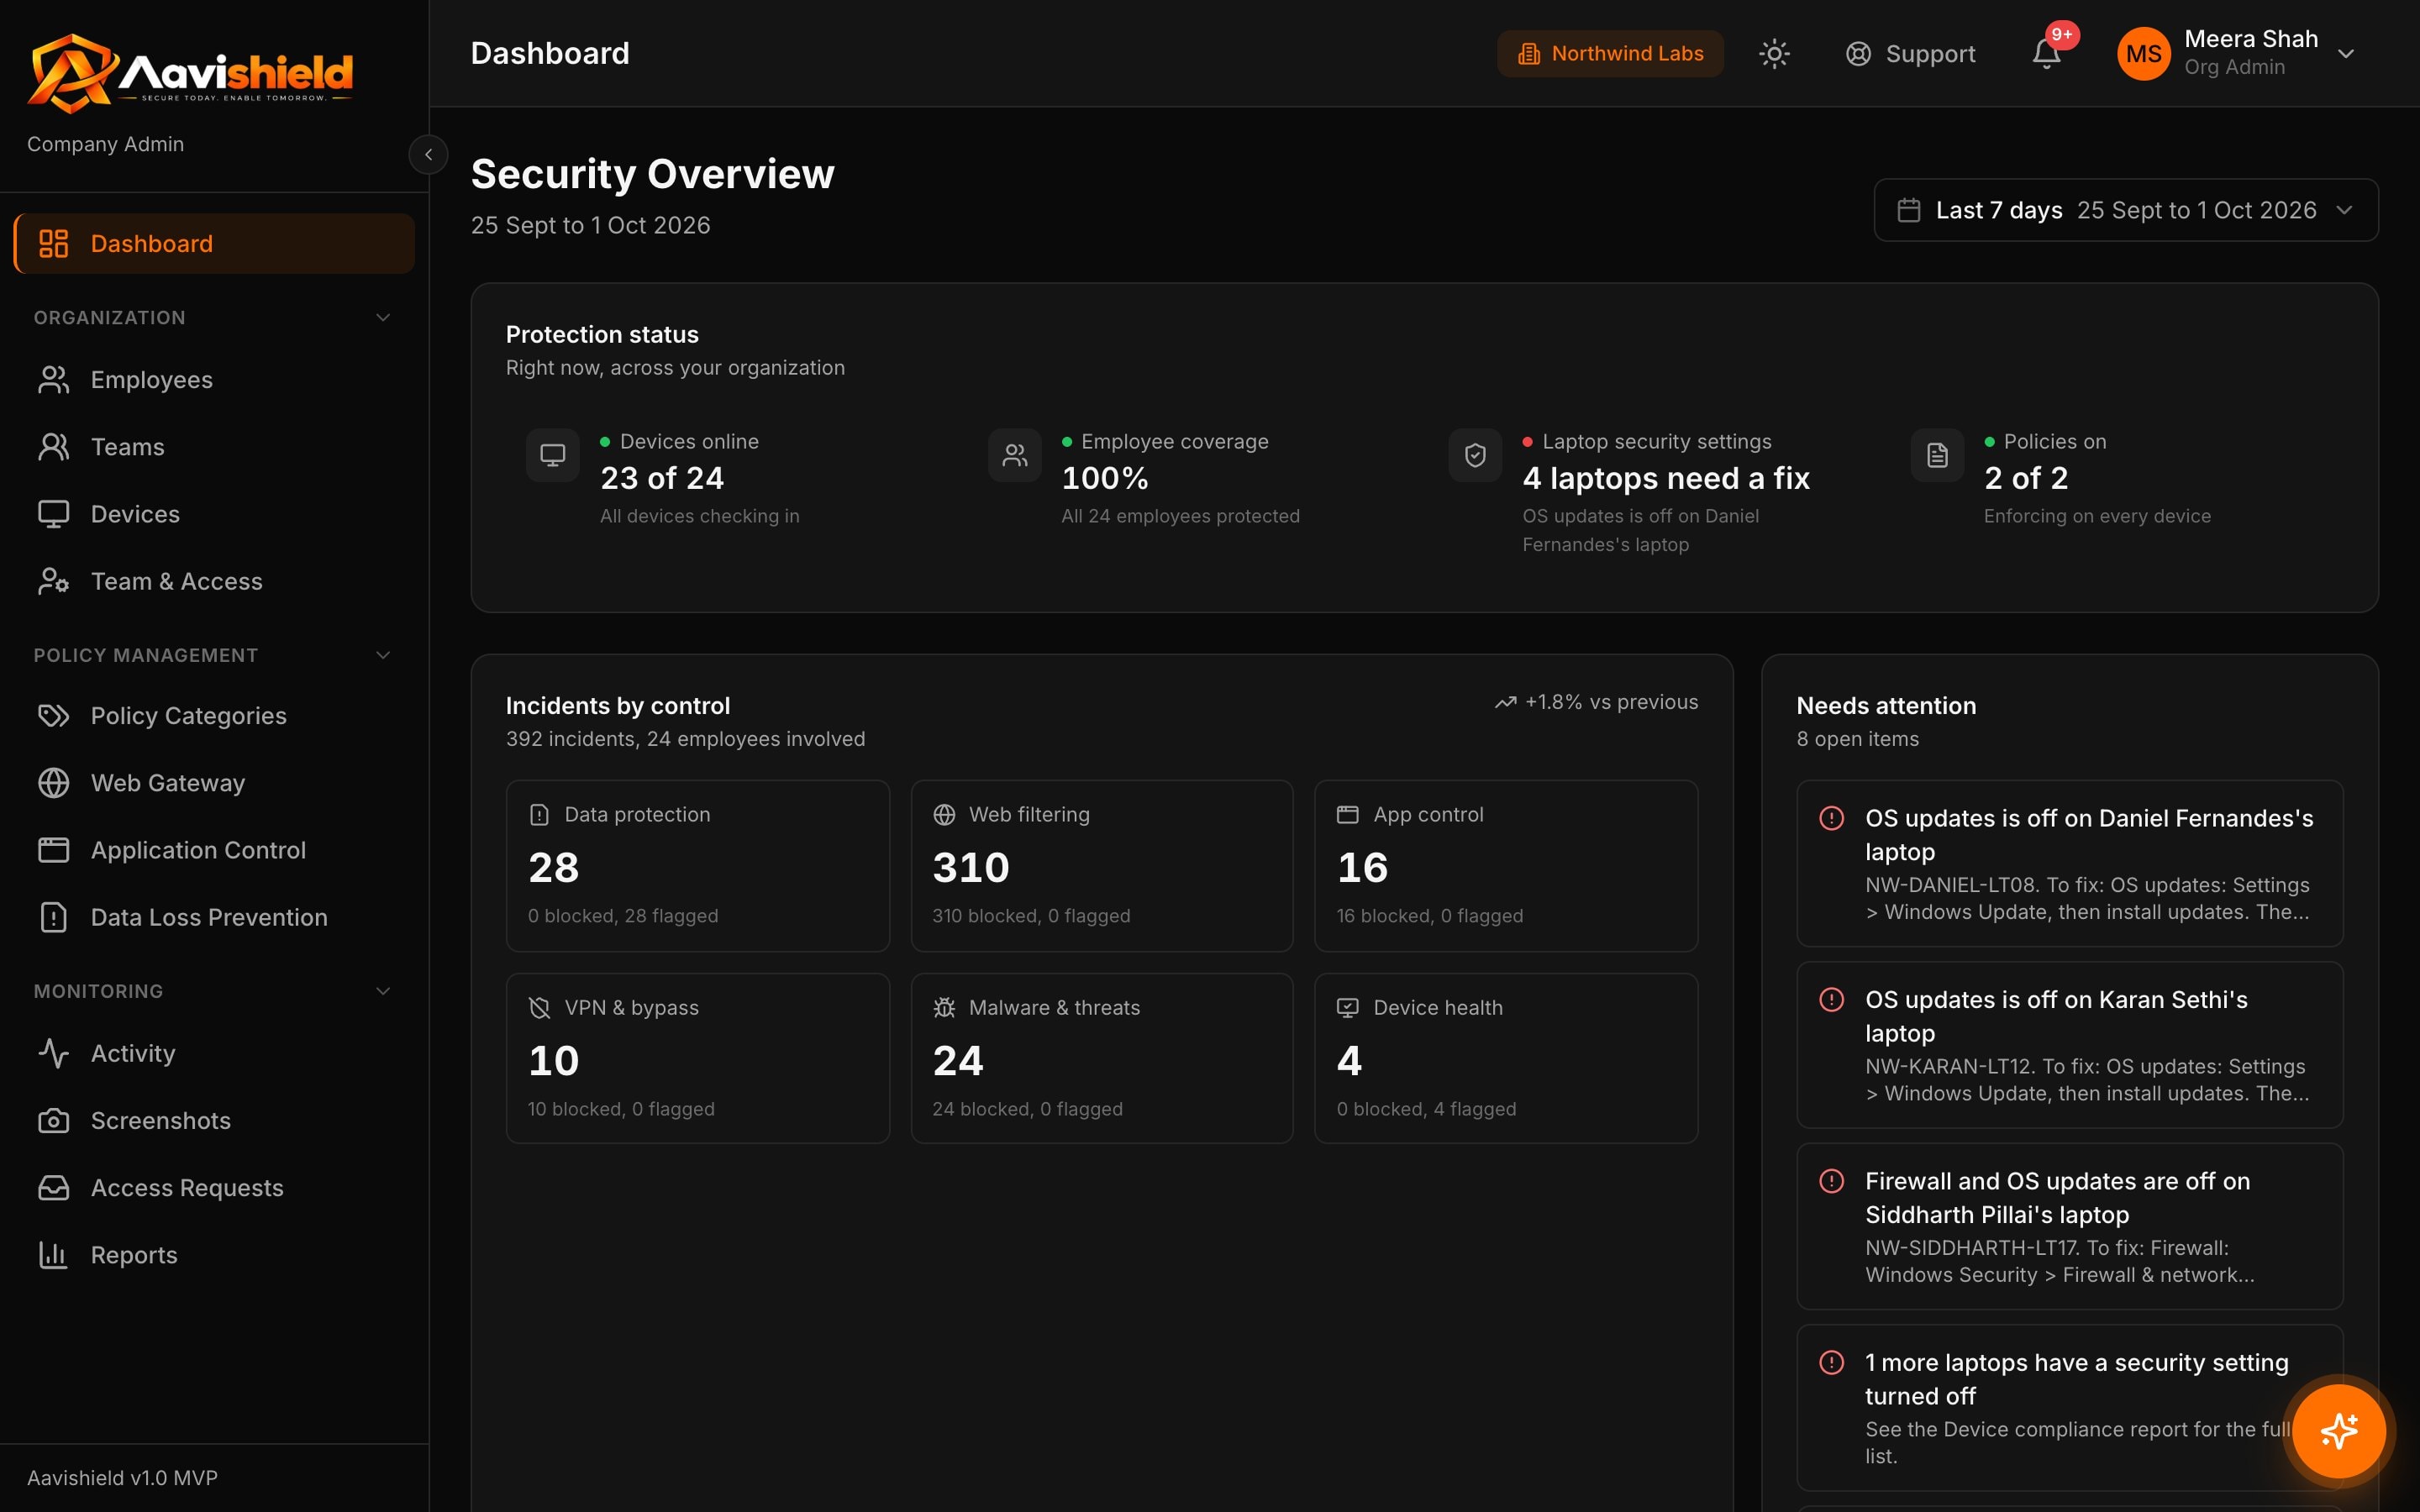
Protection status, incidents by control and a needs-attention list, for any date range.
A daily chart of incidents per control and the open items that need someone's attention.
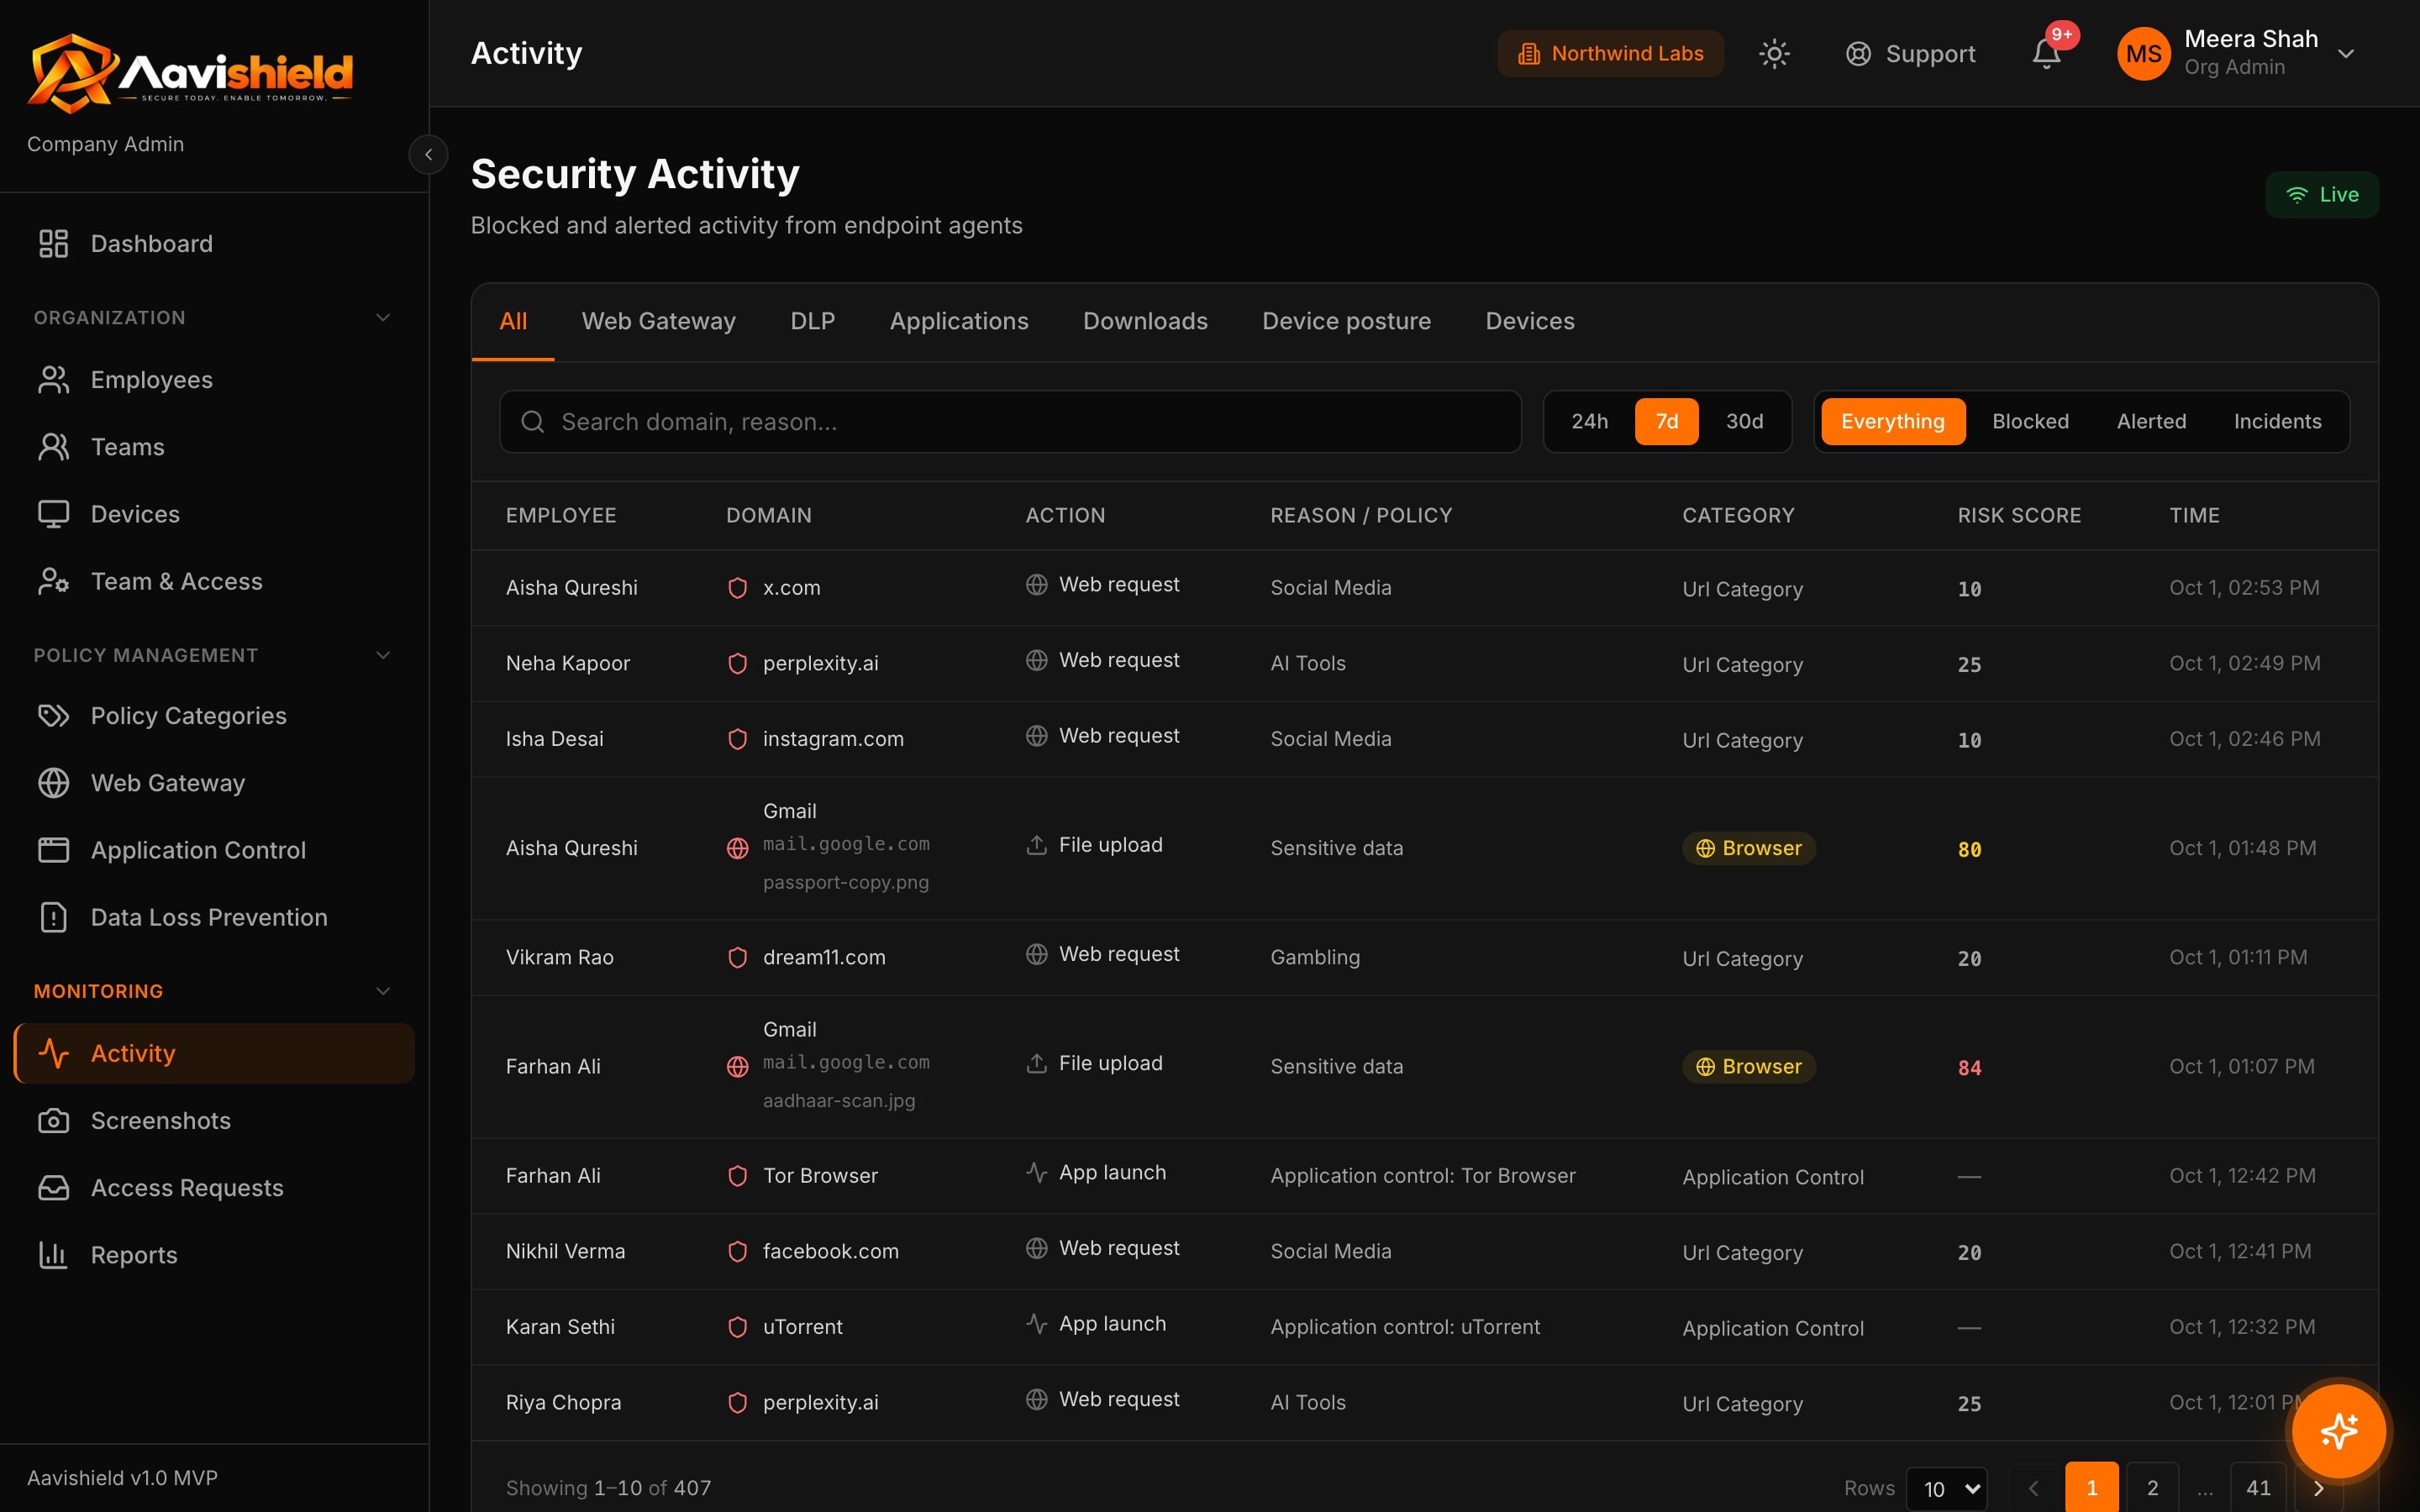
Every blocked and alerted event from every control, filterable by source, time and outcome.
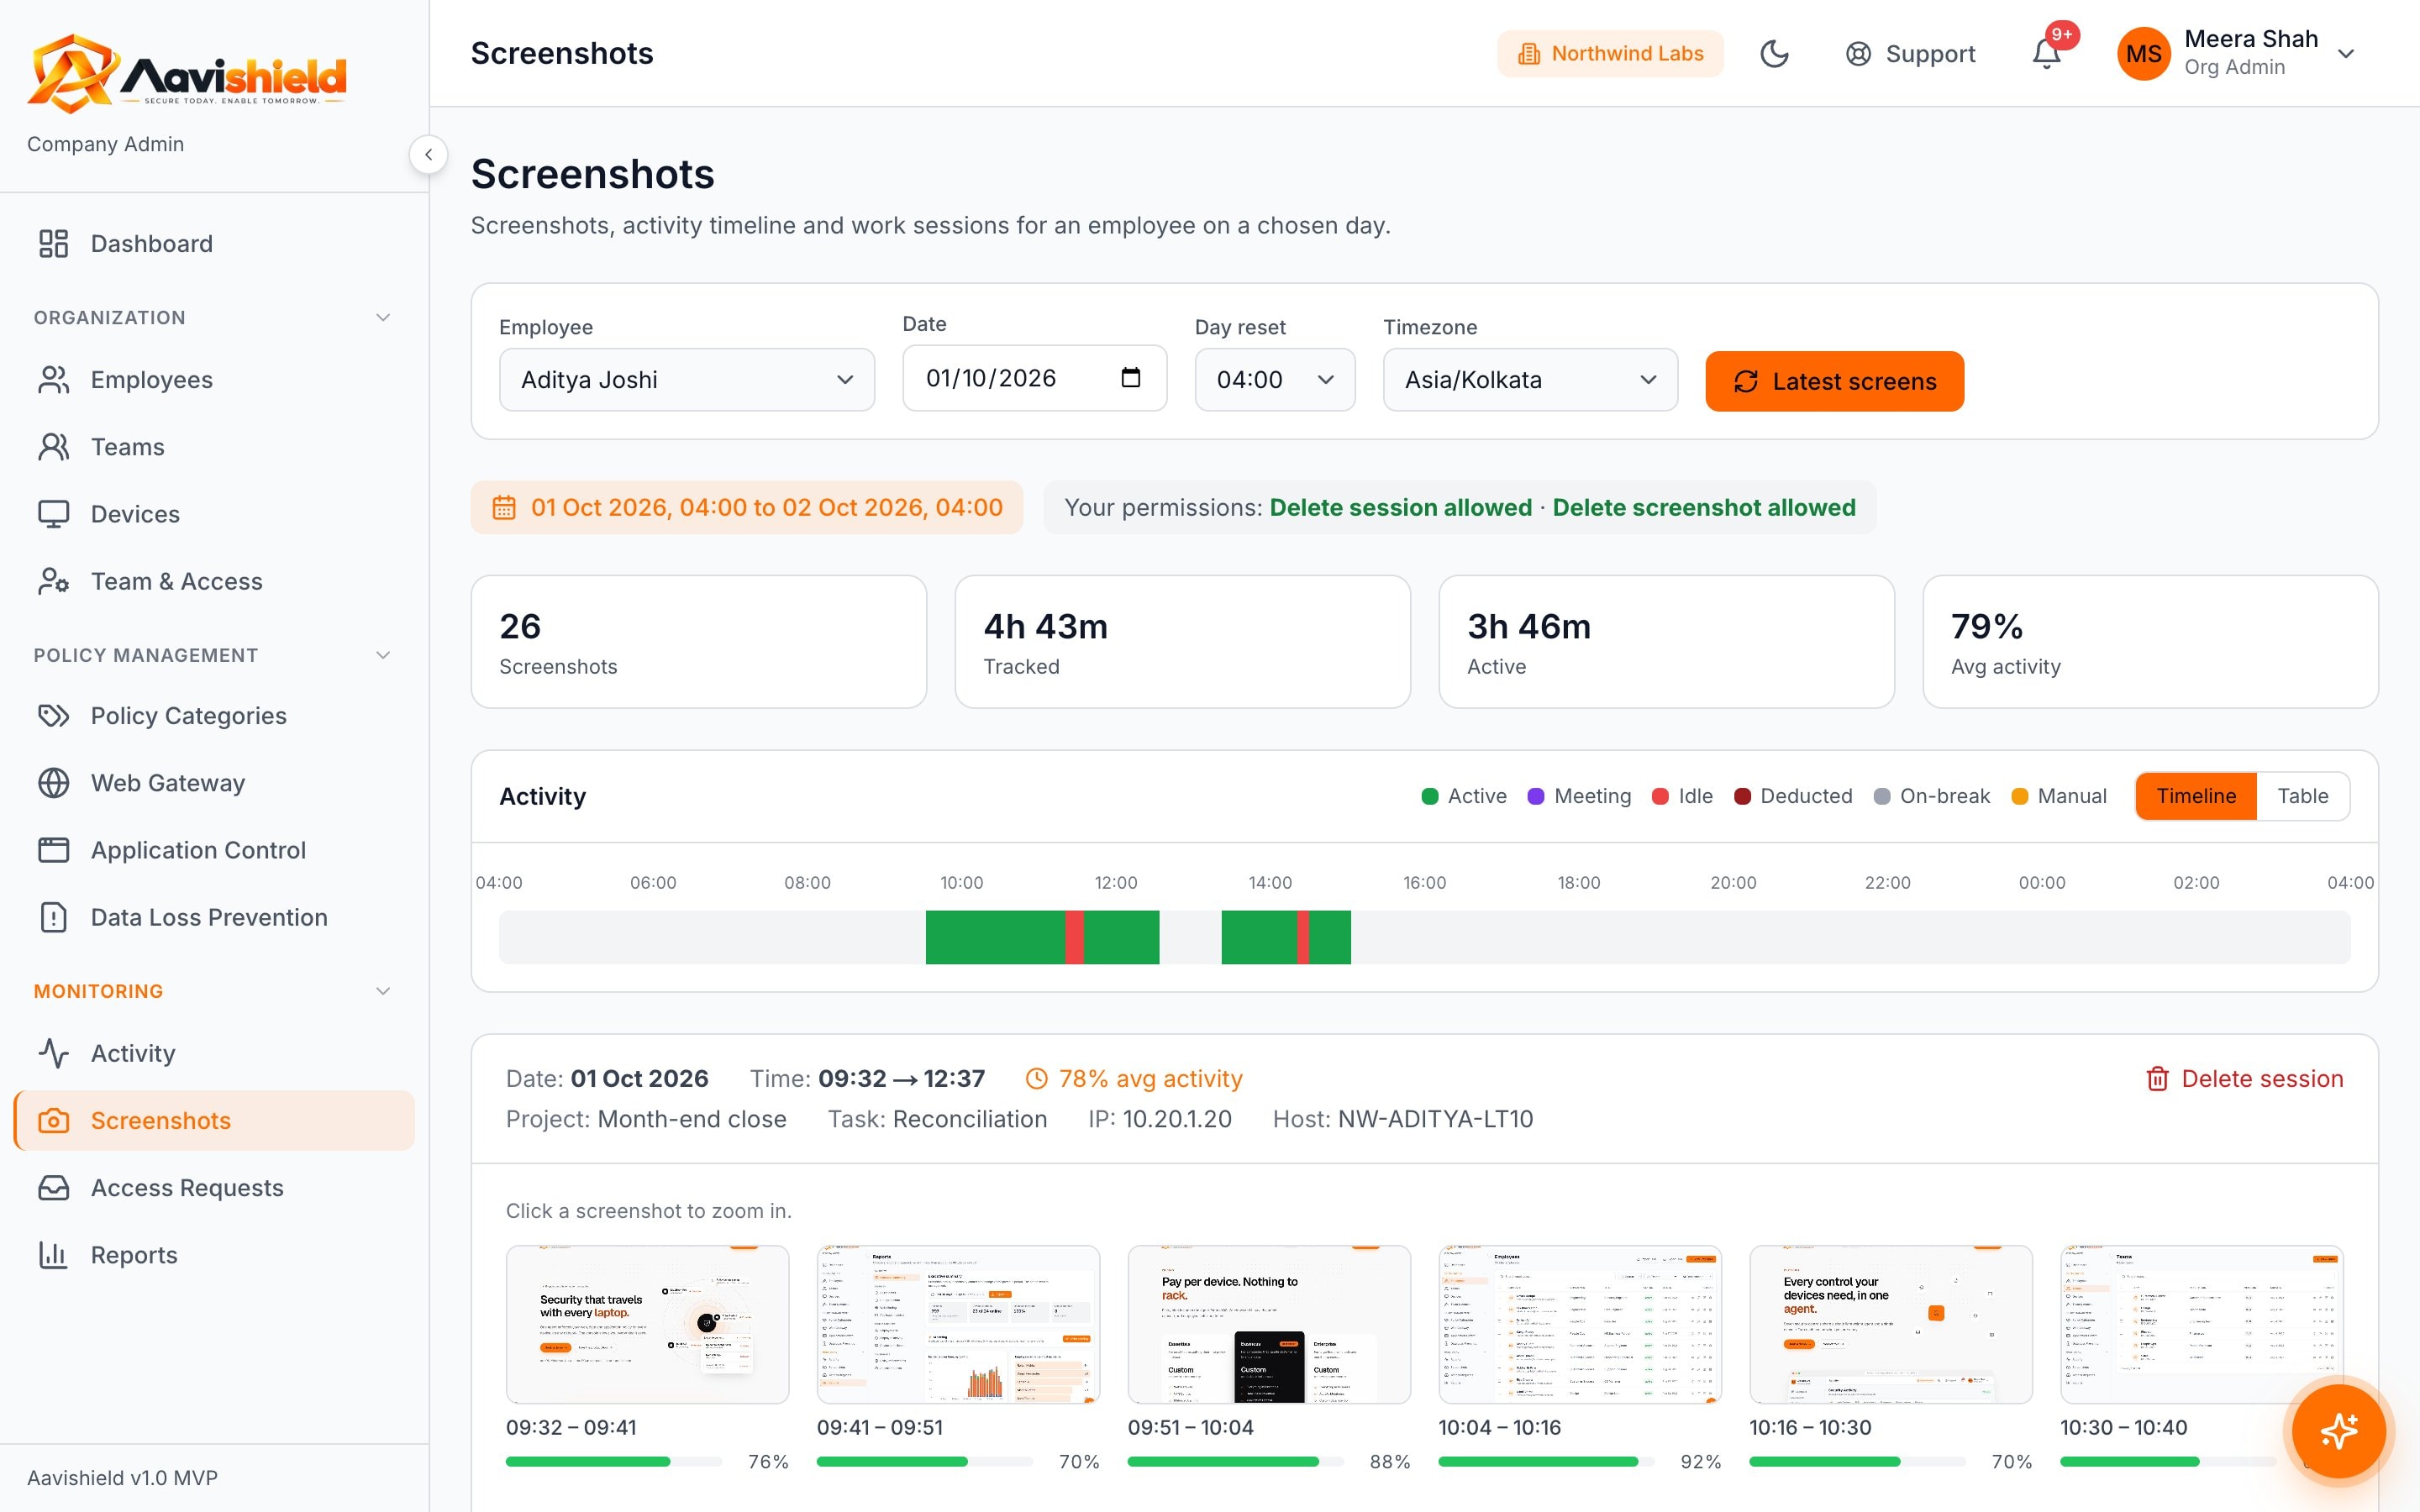
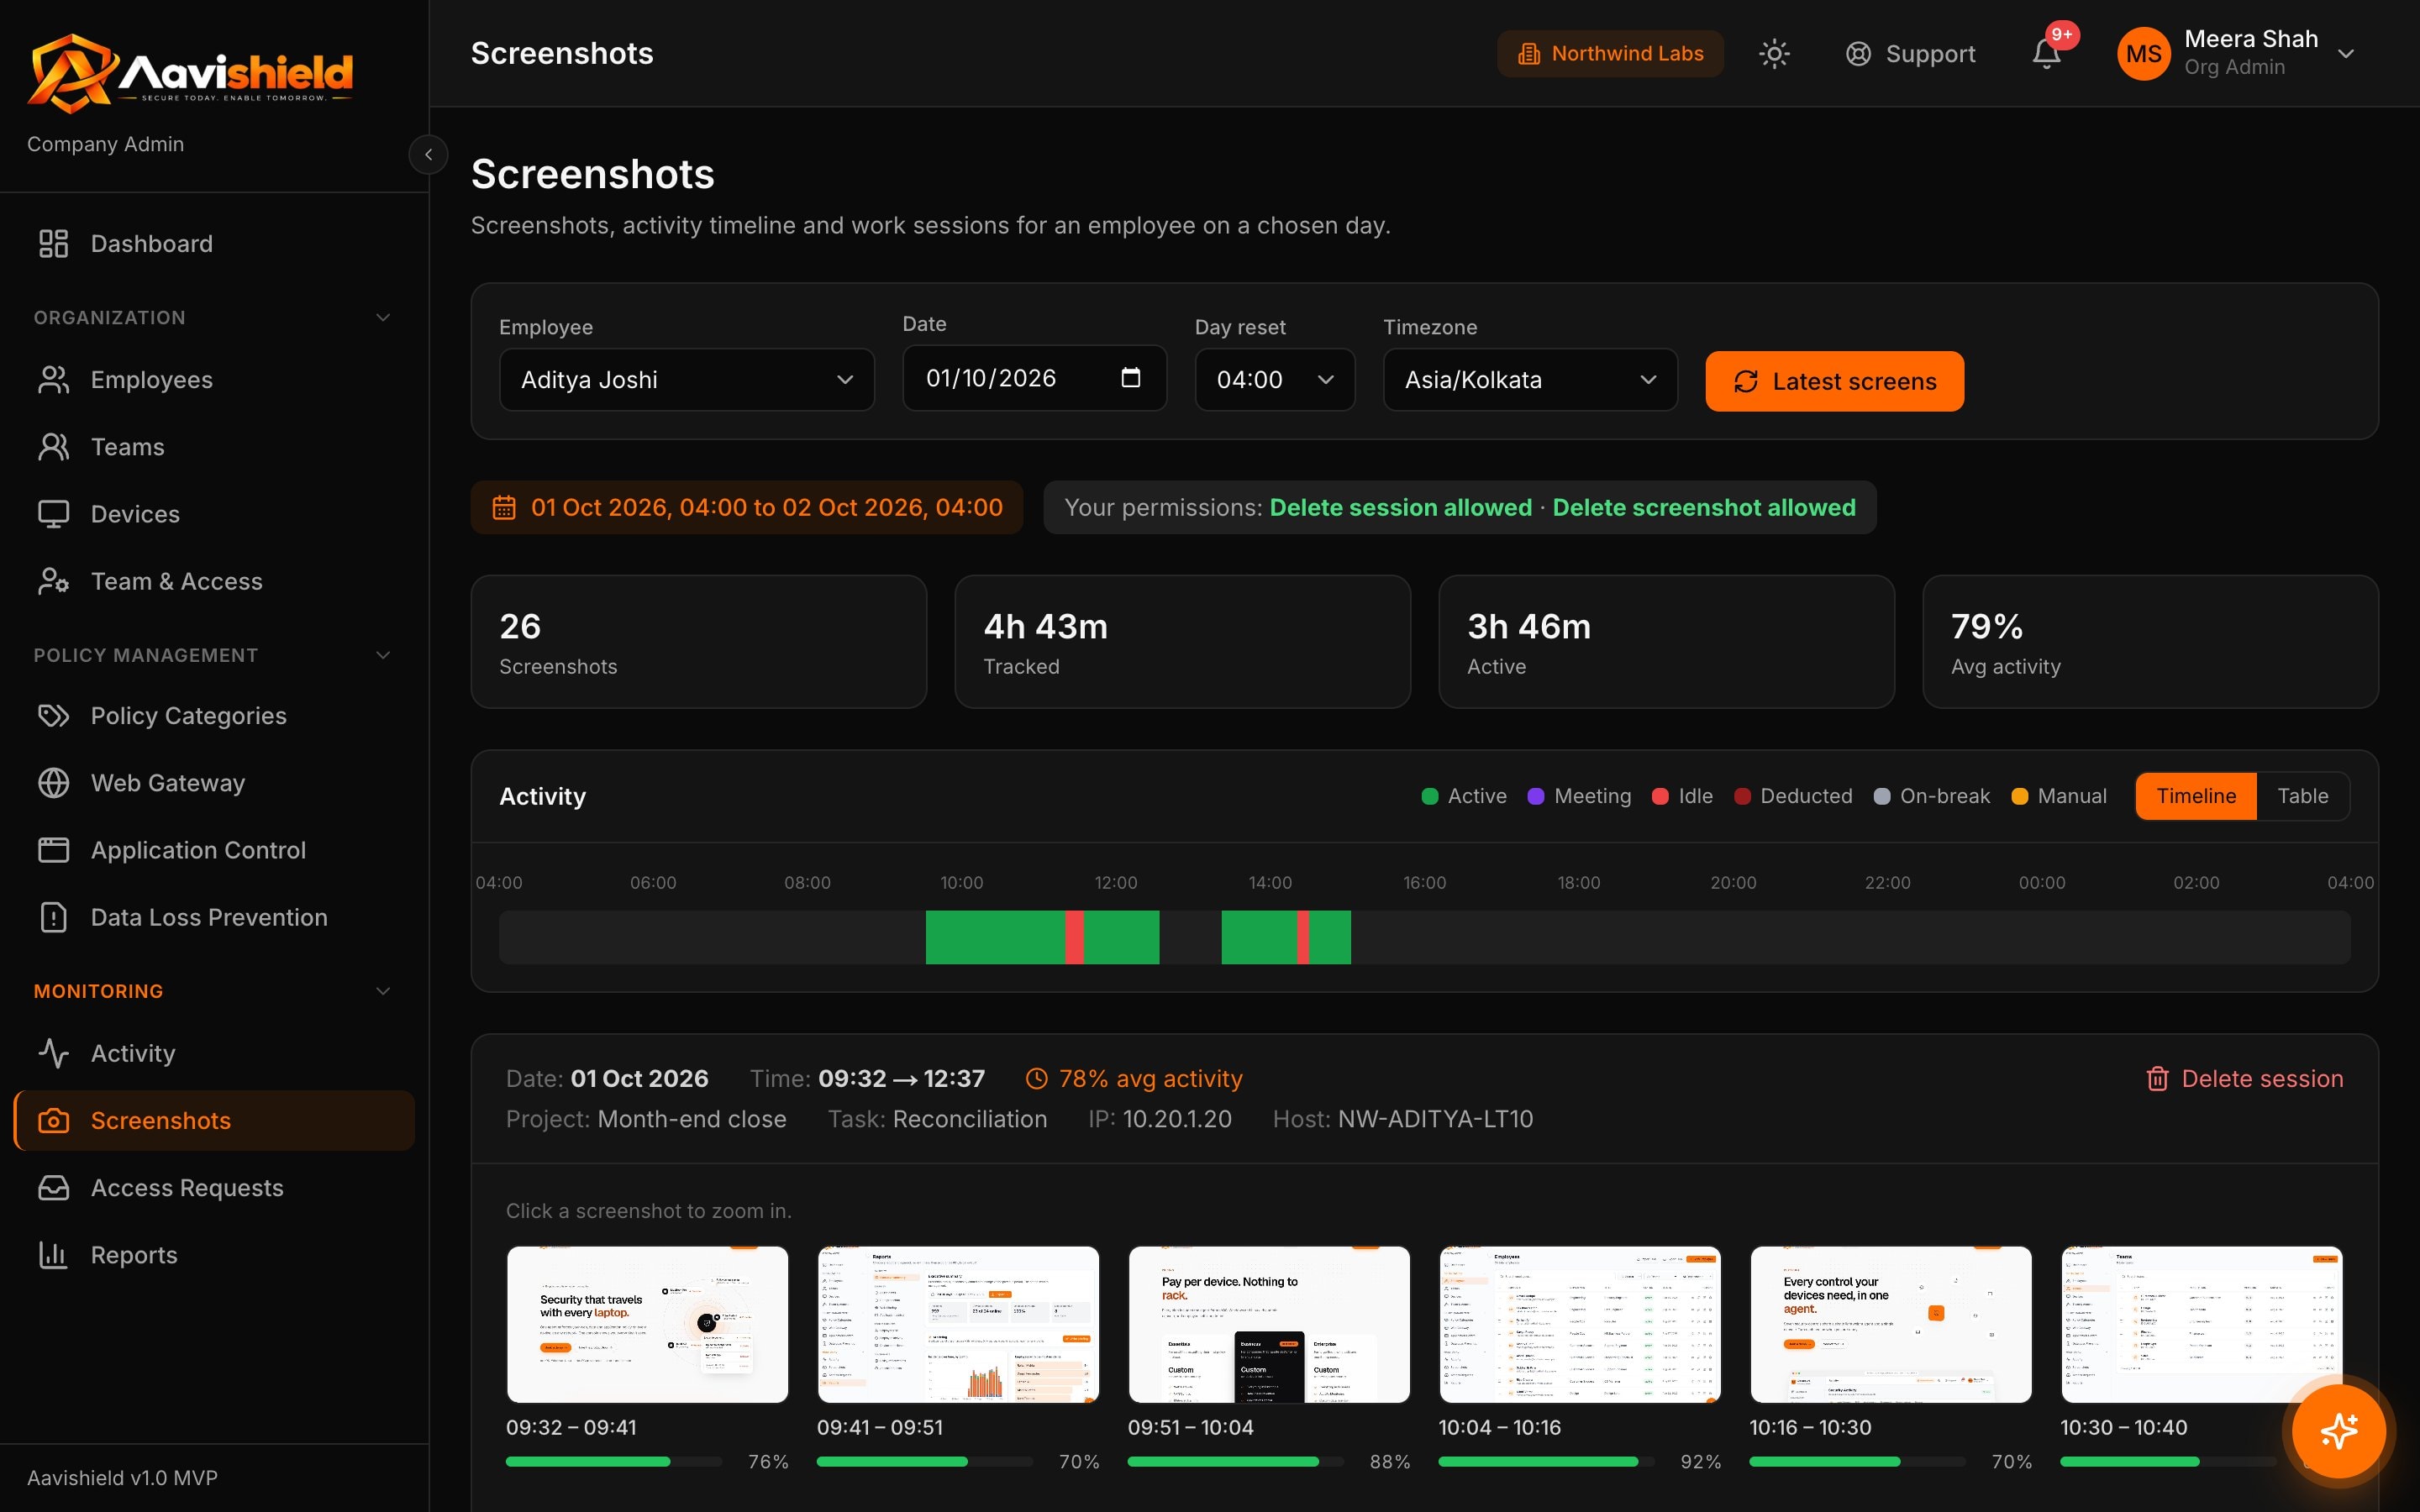
For monitored devices: tracked and active time, a colour-coded timeline, work sessions and periodic screenshots.
The directory behind every policy and every finding.
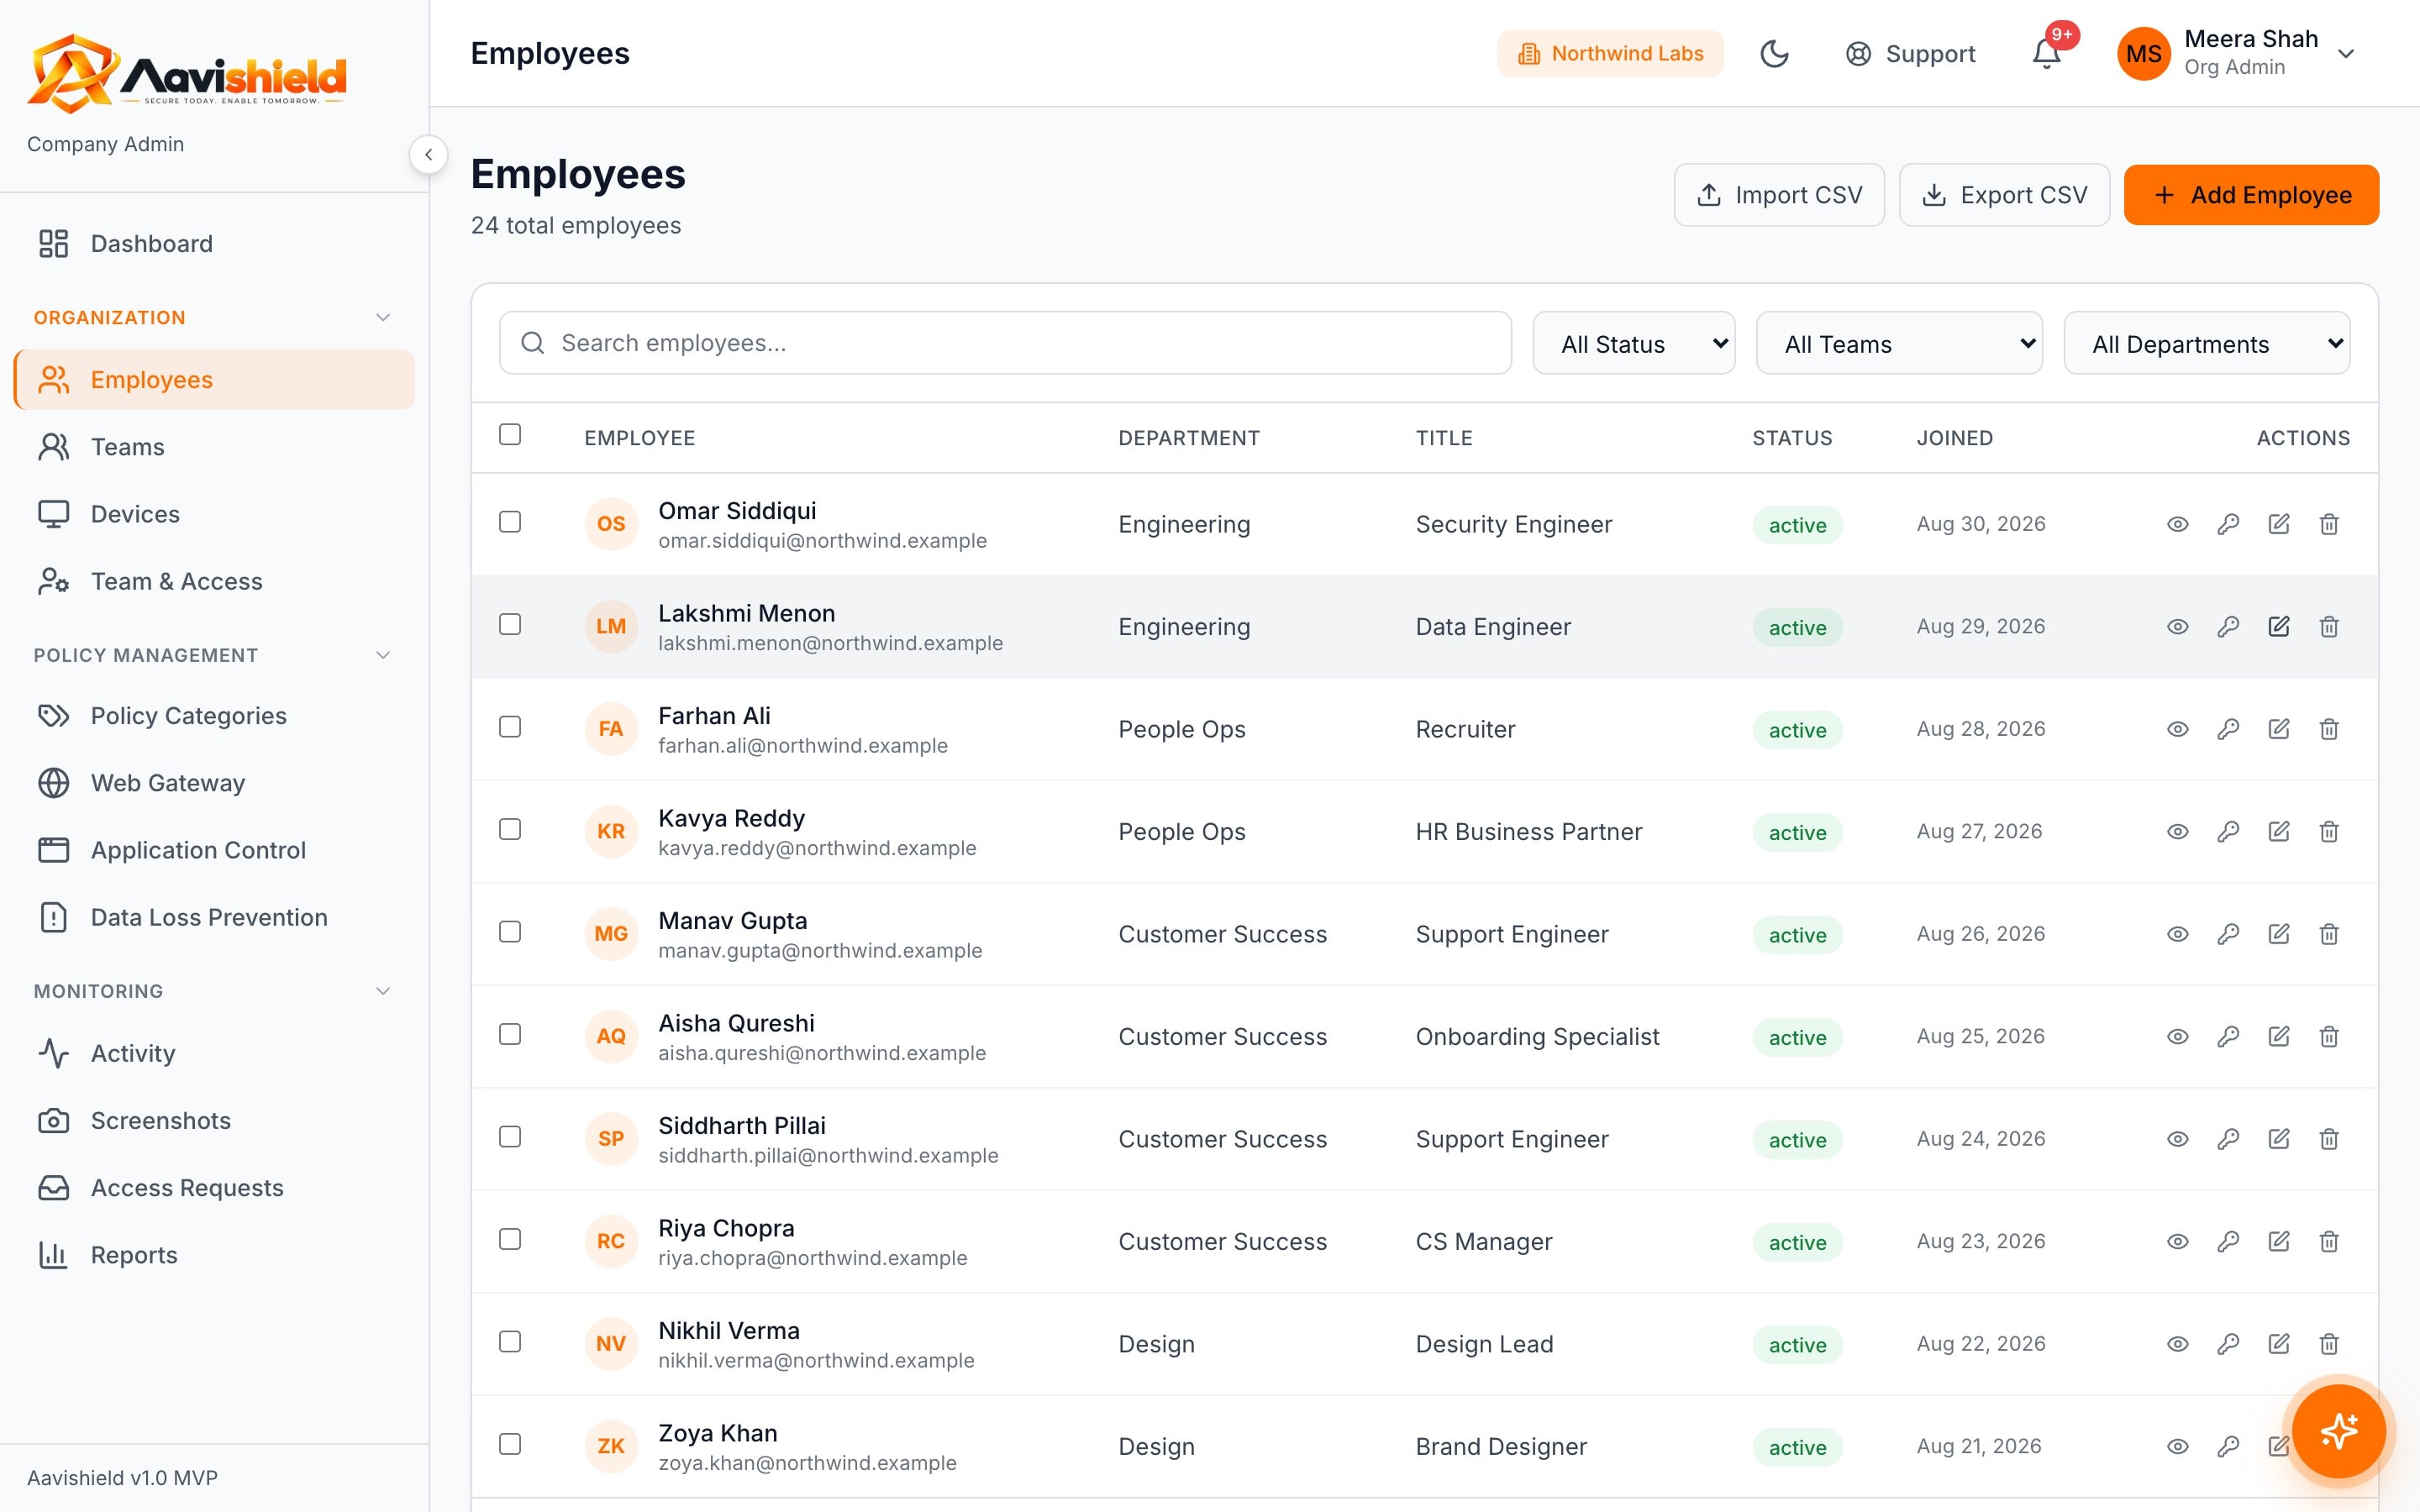
Every employee with department, title, status and devices. Import or export by CSV.
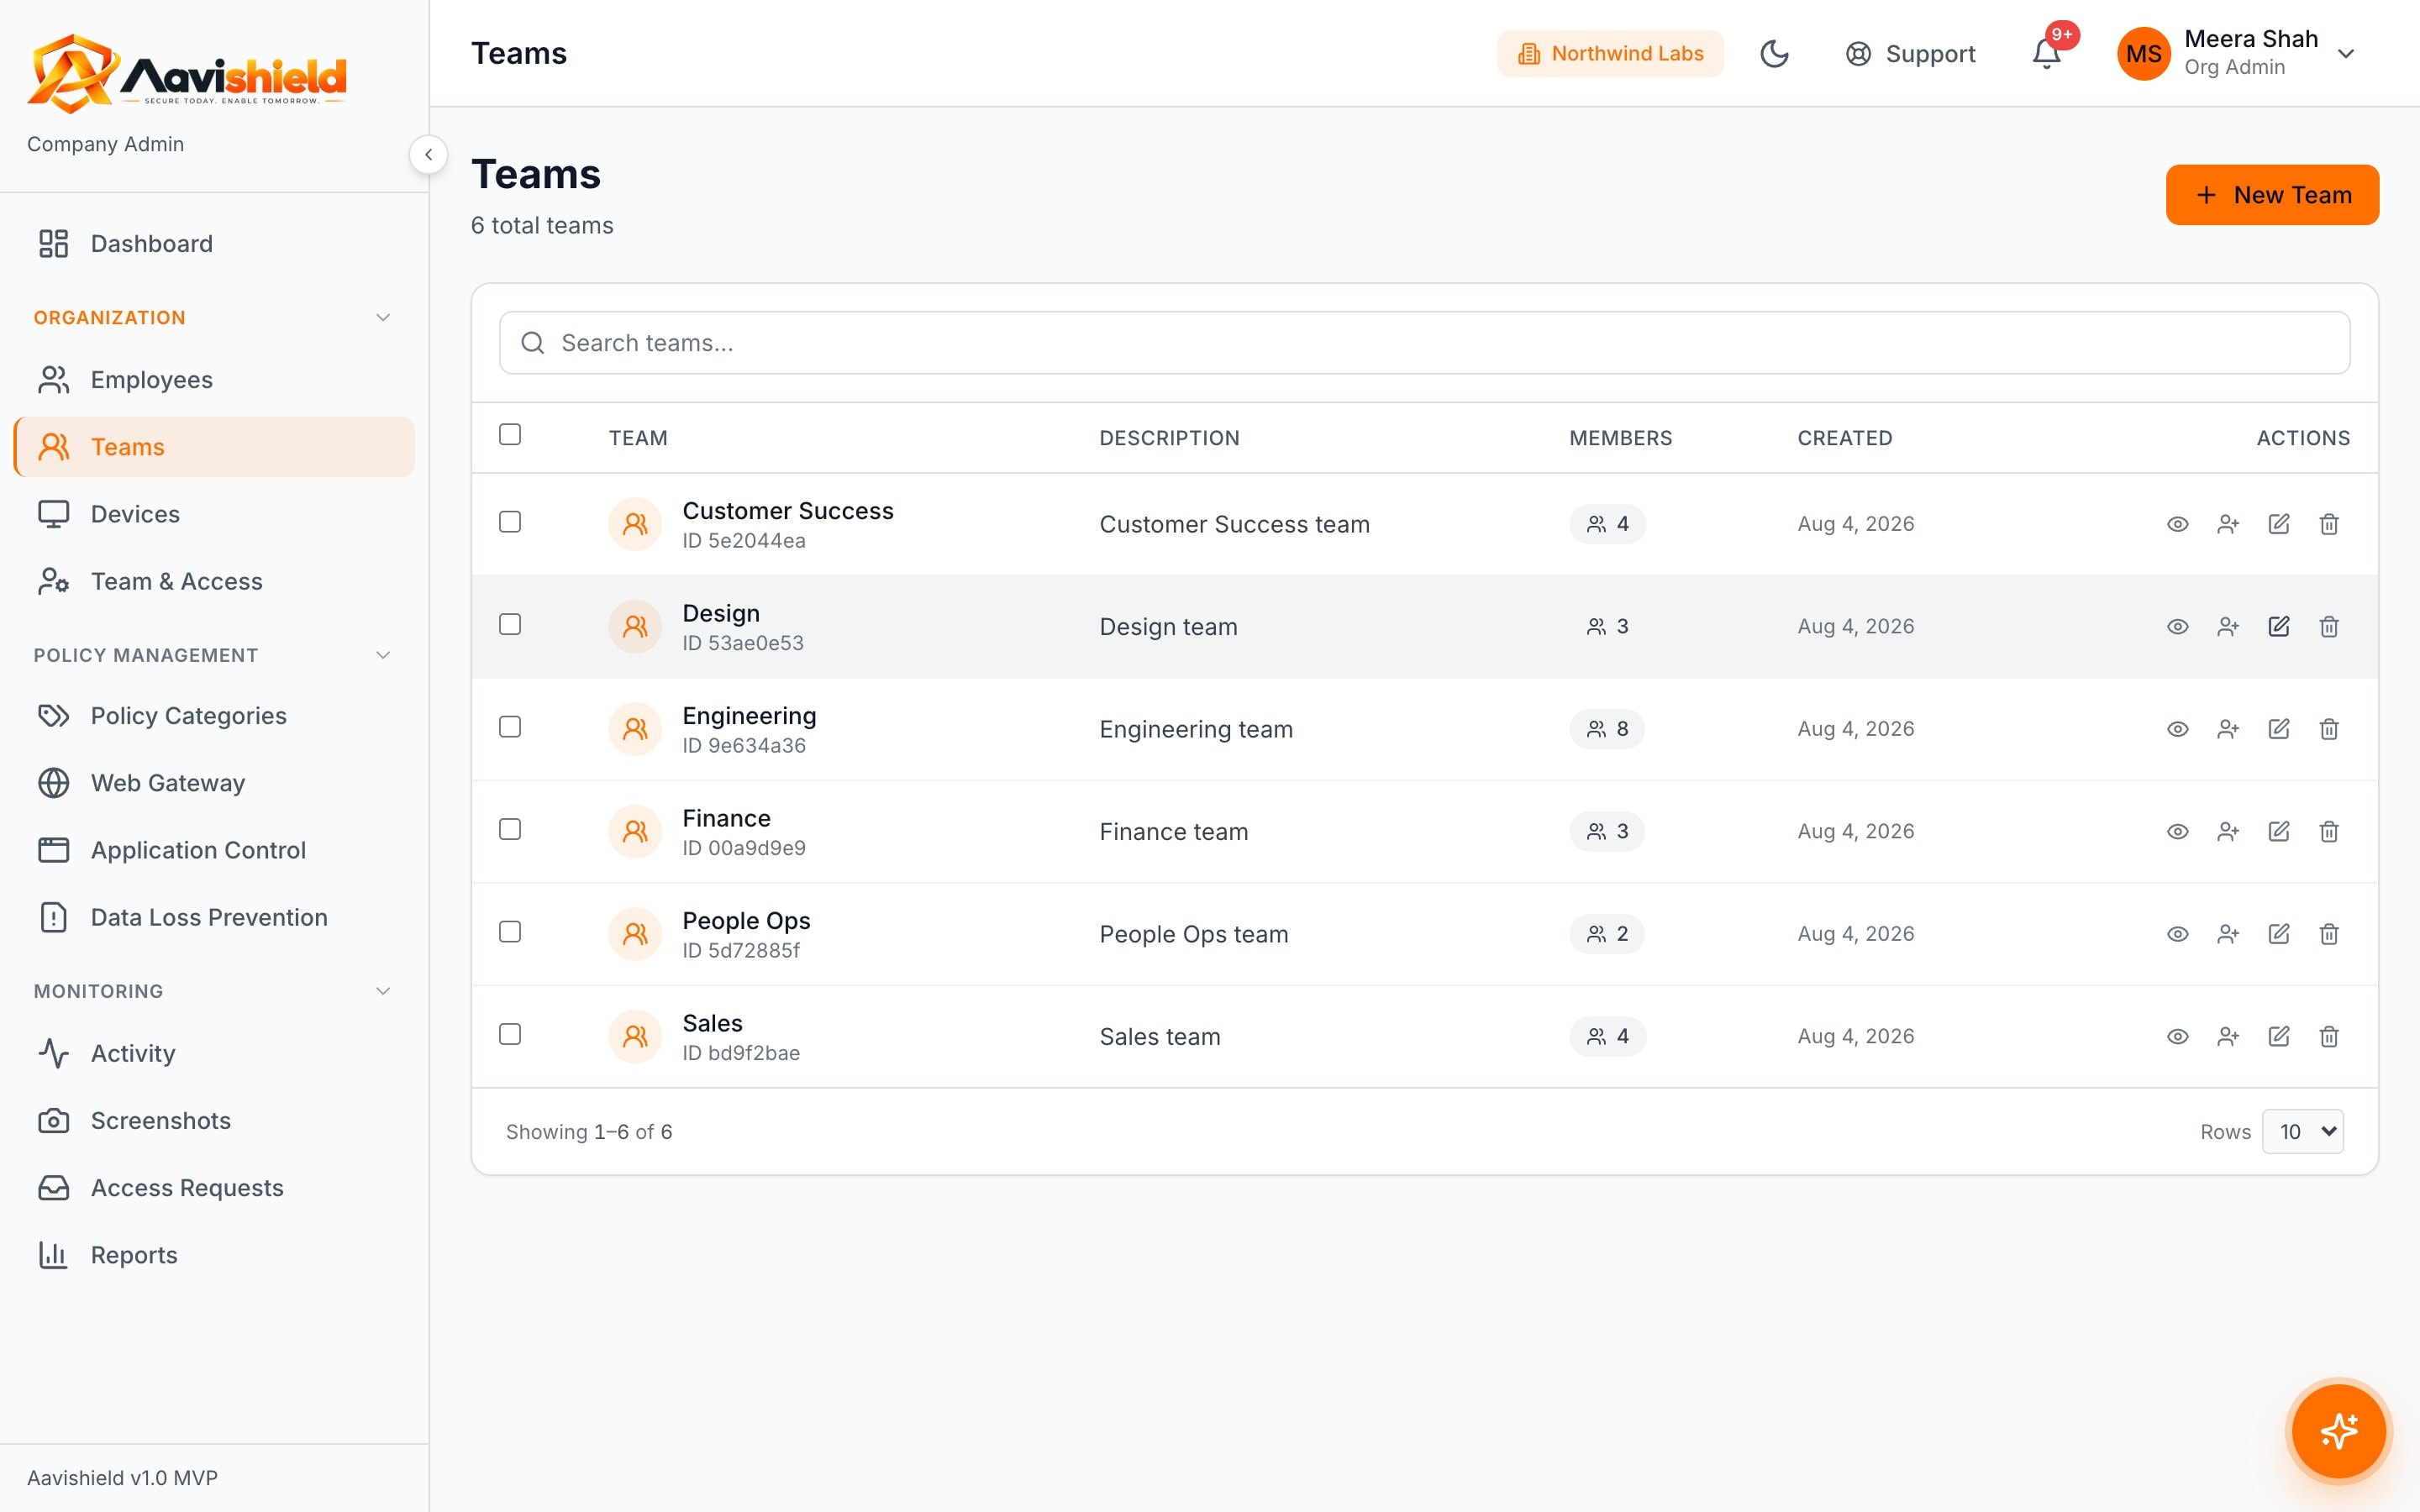
Teams group people for policy targeting and reporting.
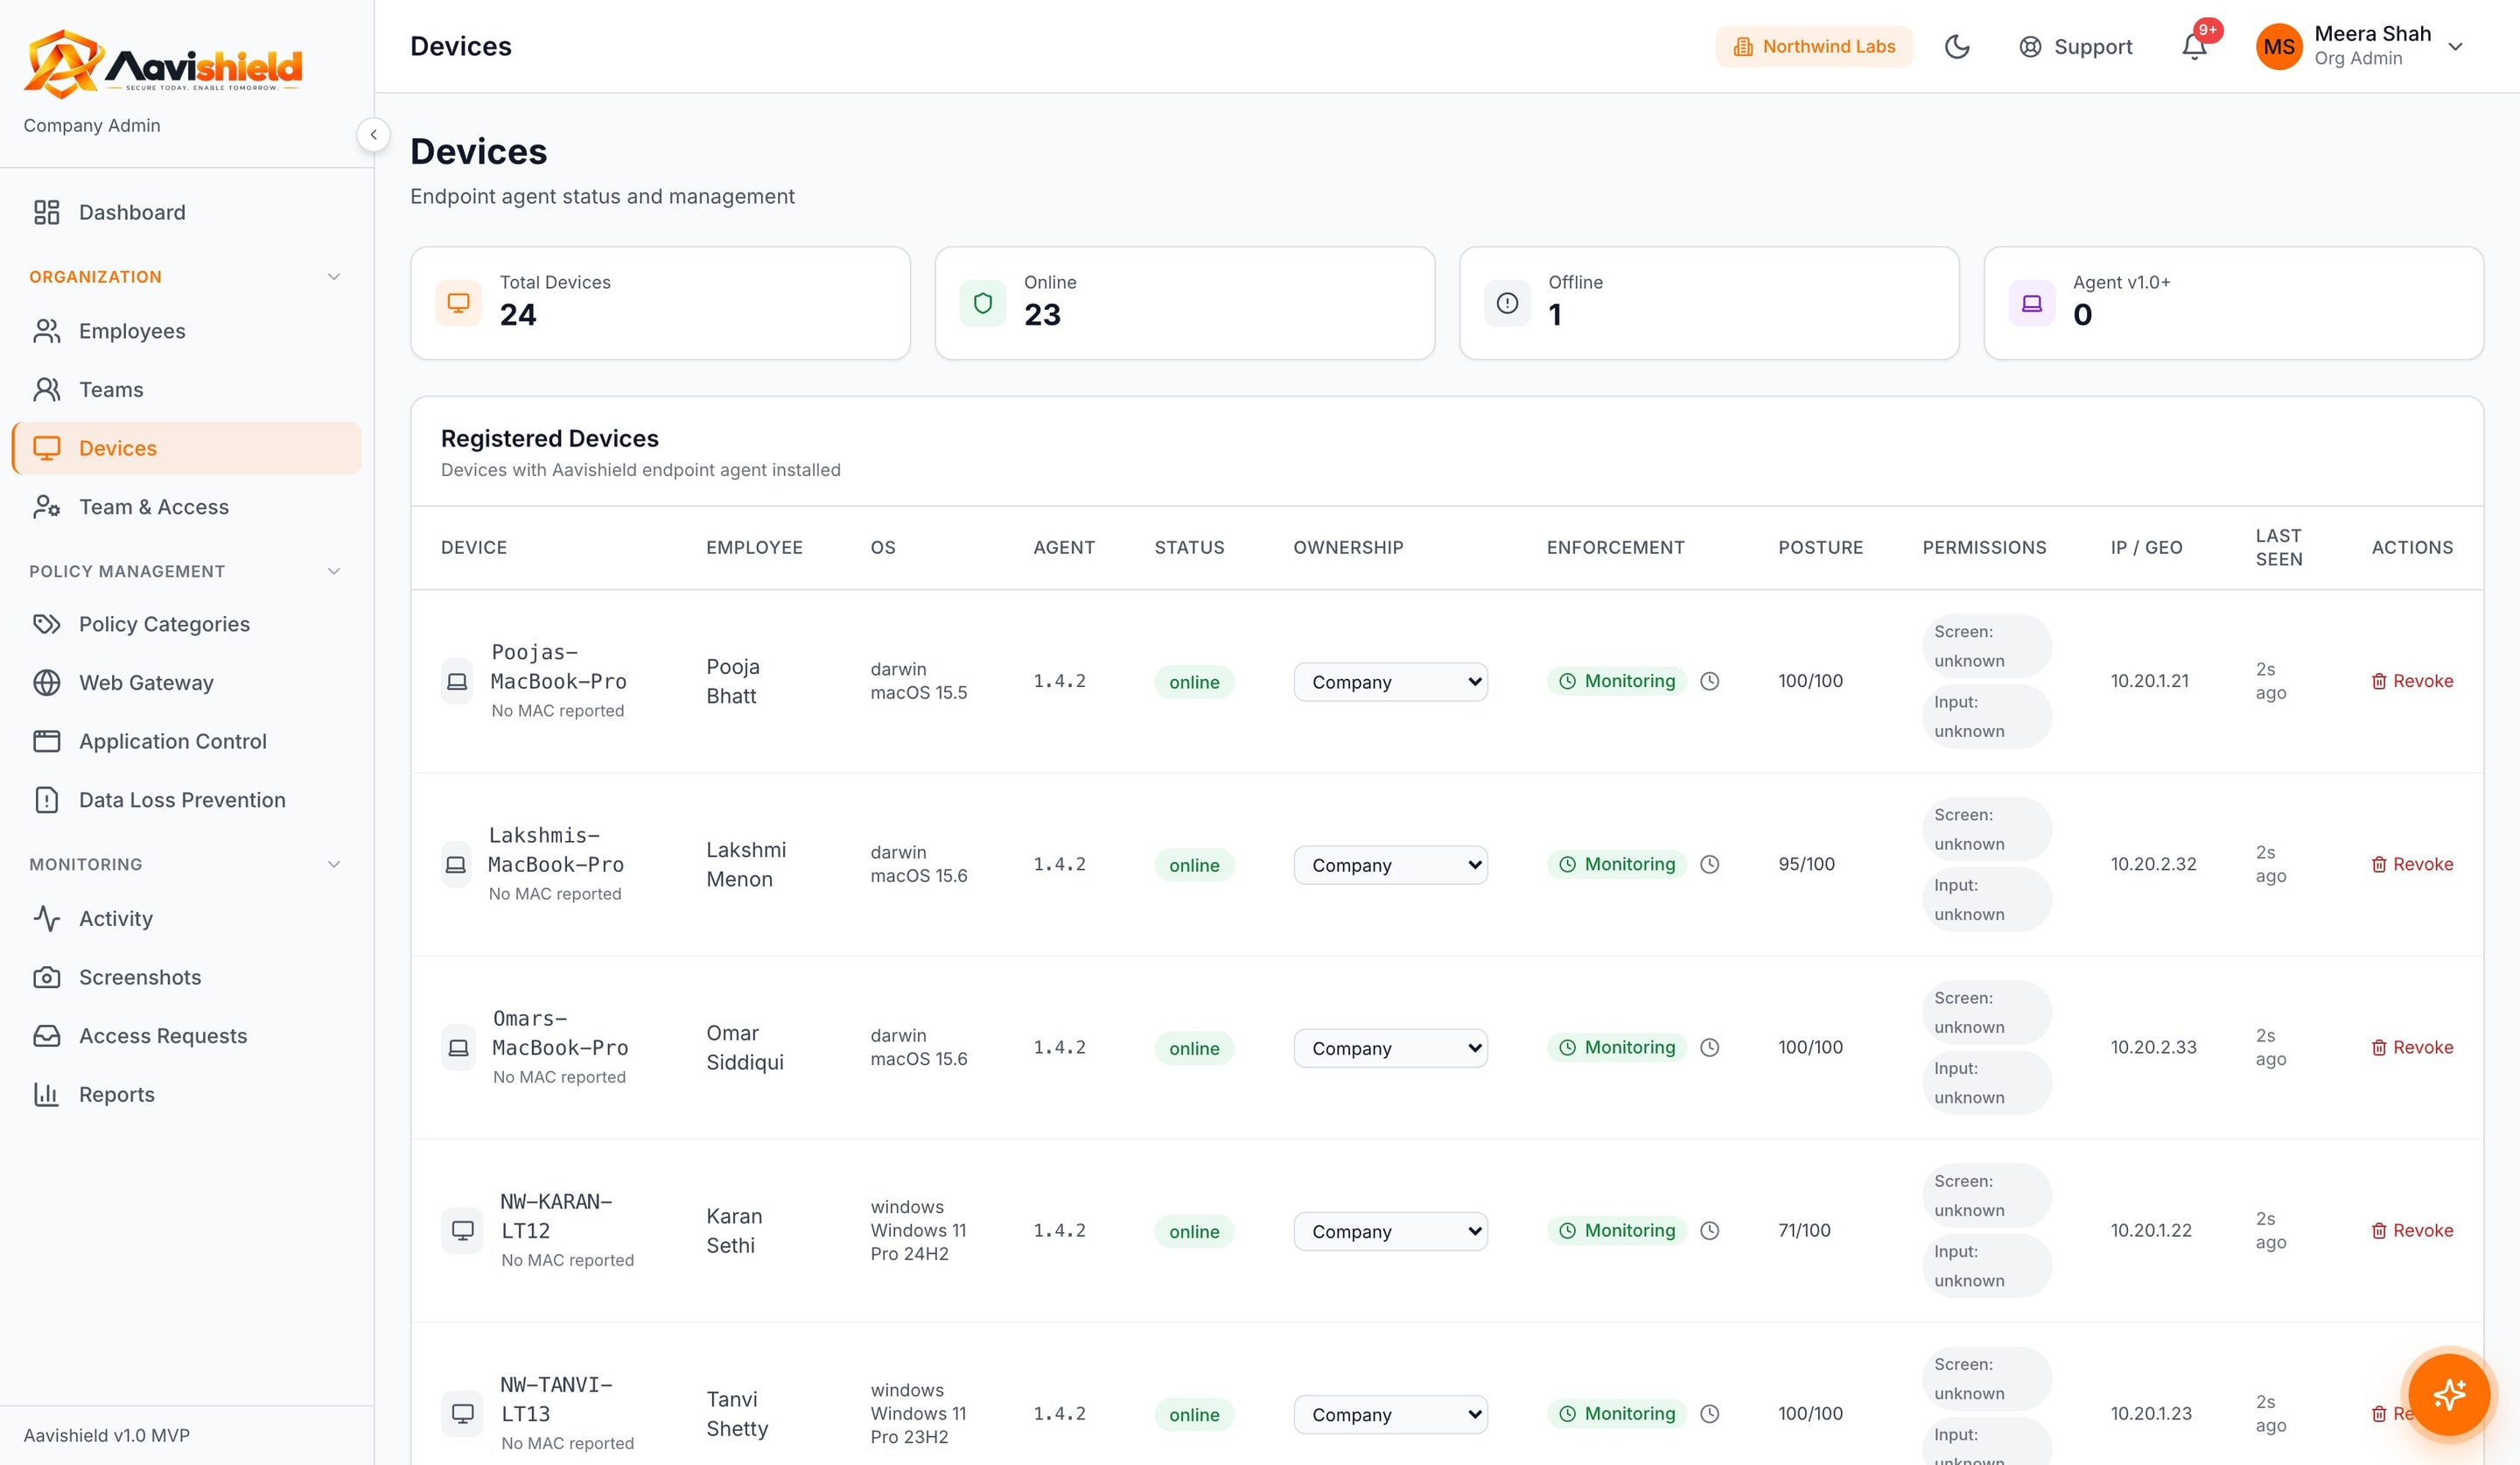
Every enrolled device with OS, agent version, status, ownership, enforcement and posture score.
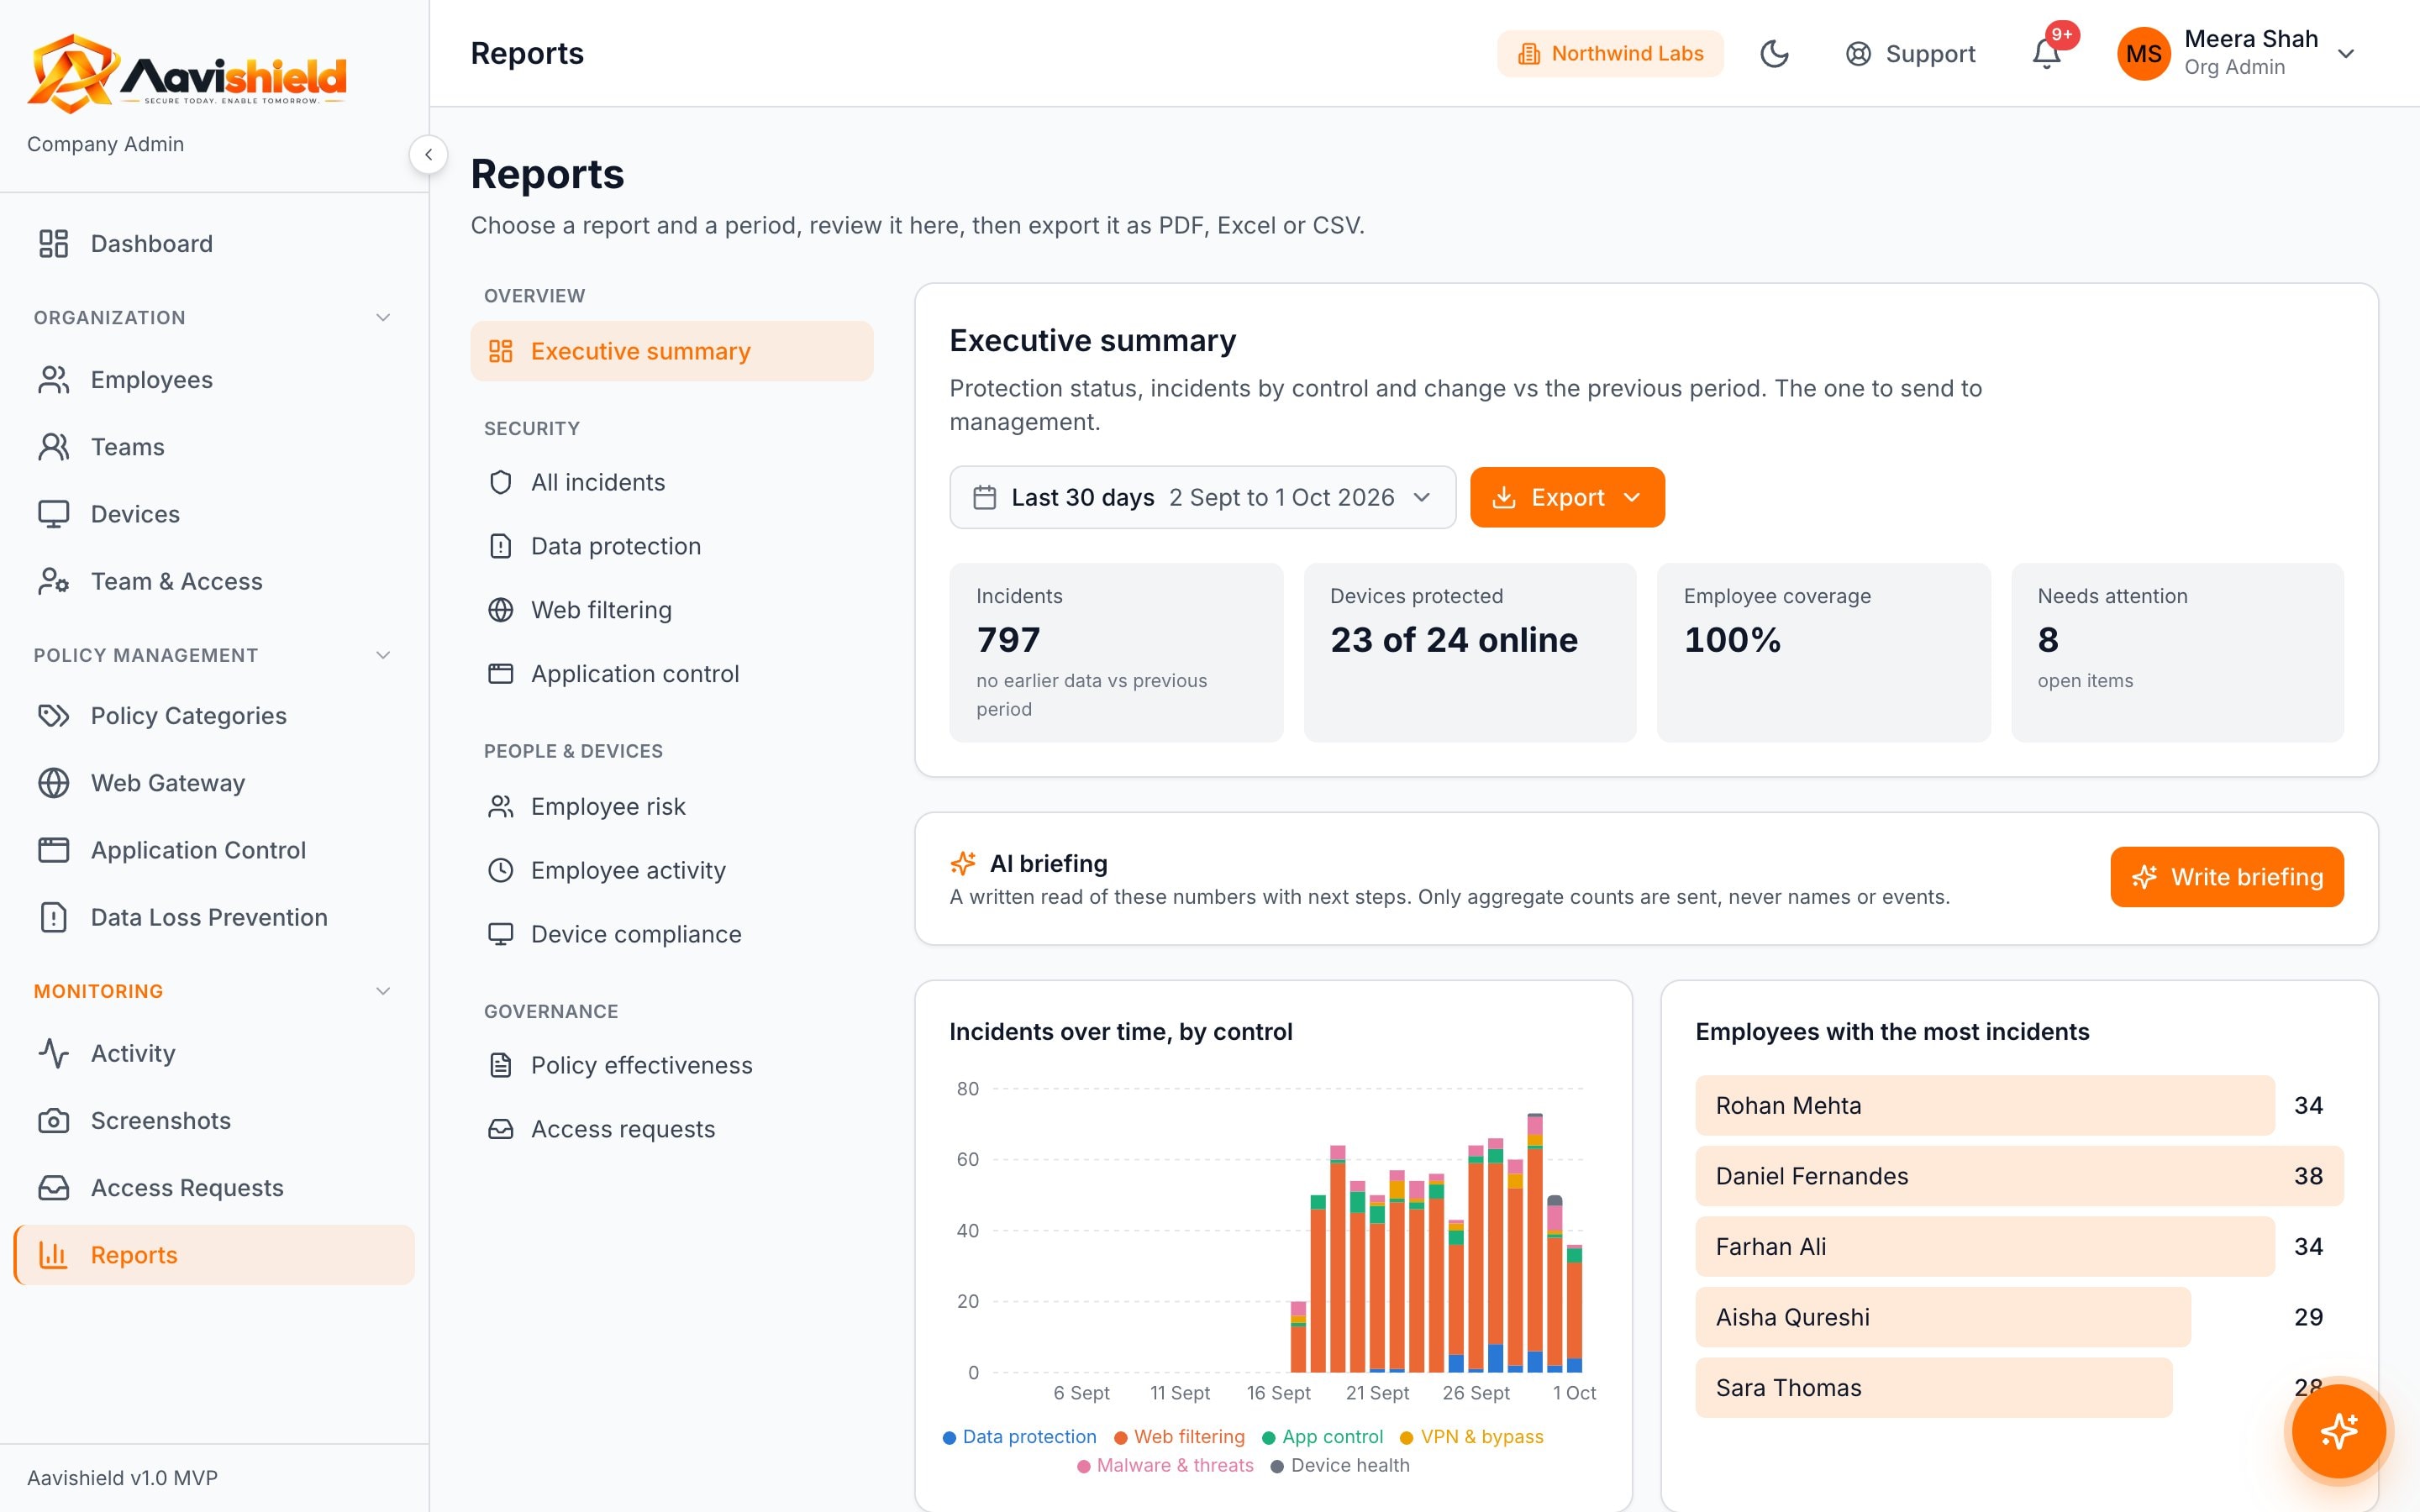
Reports for leadership, clients and auditors, exported in the format they want.
Incidents, devices protected, coverage and open items, with an AI briefing and a chart of incidents by control.
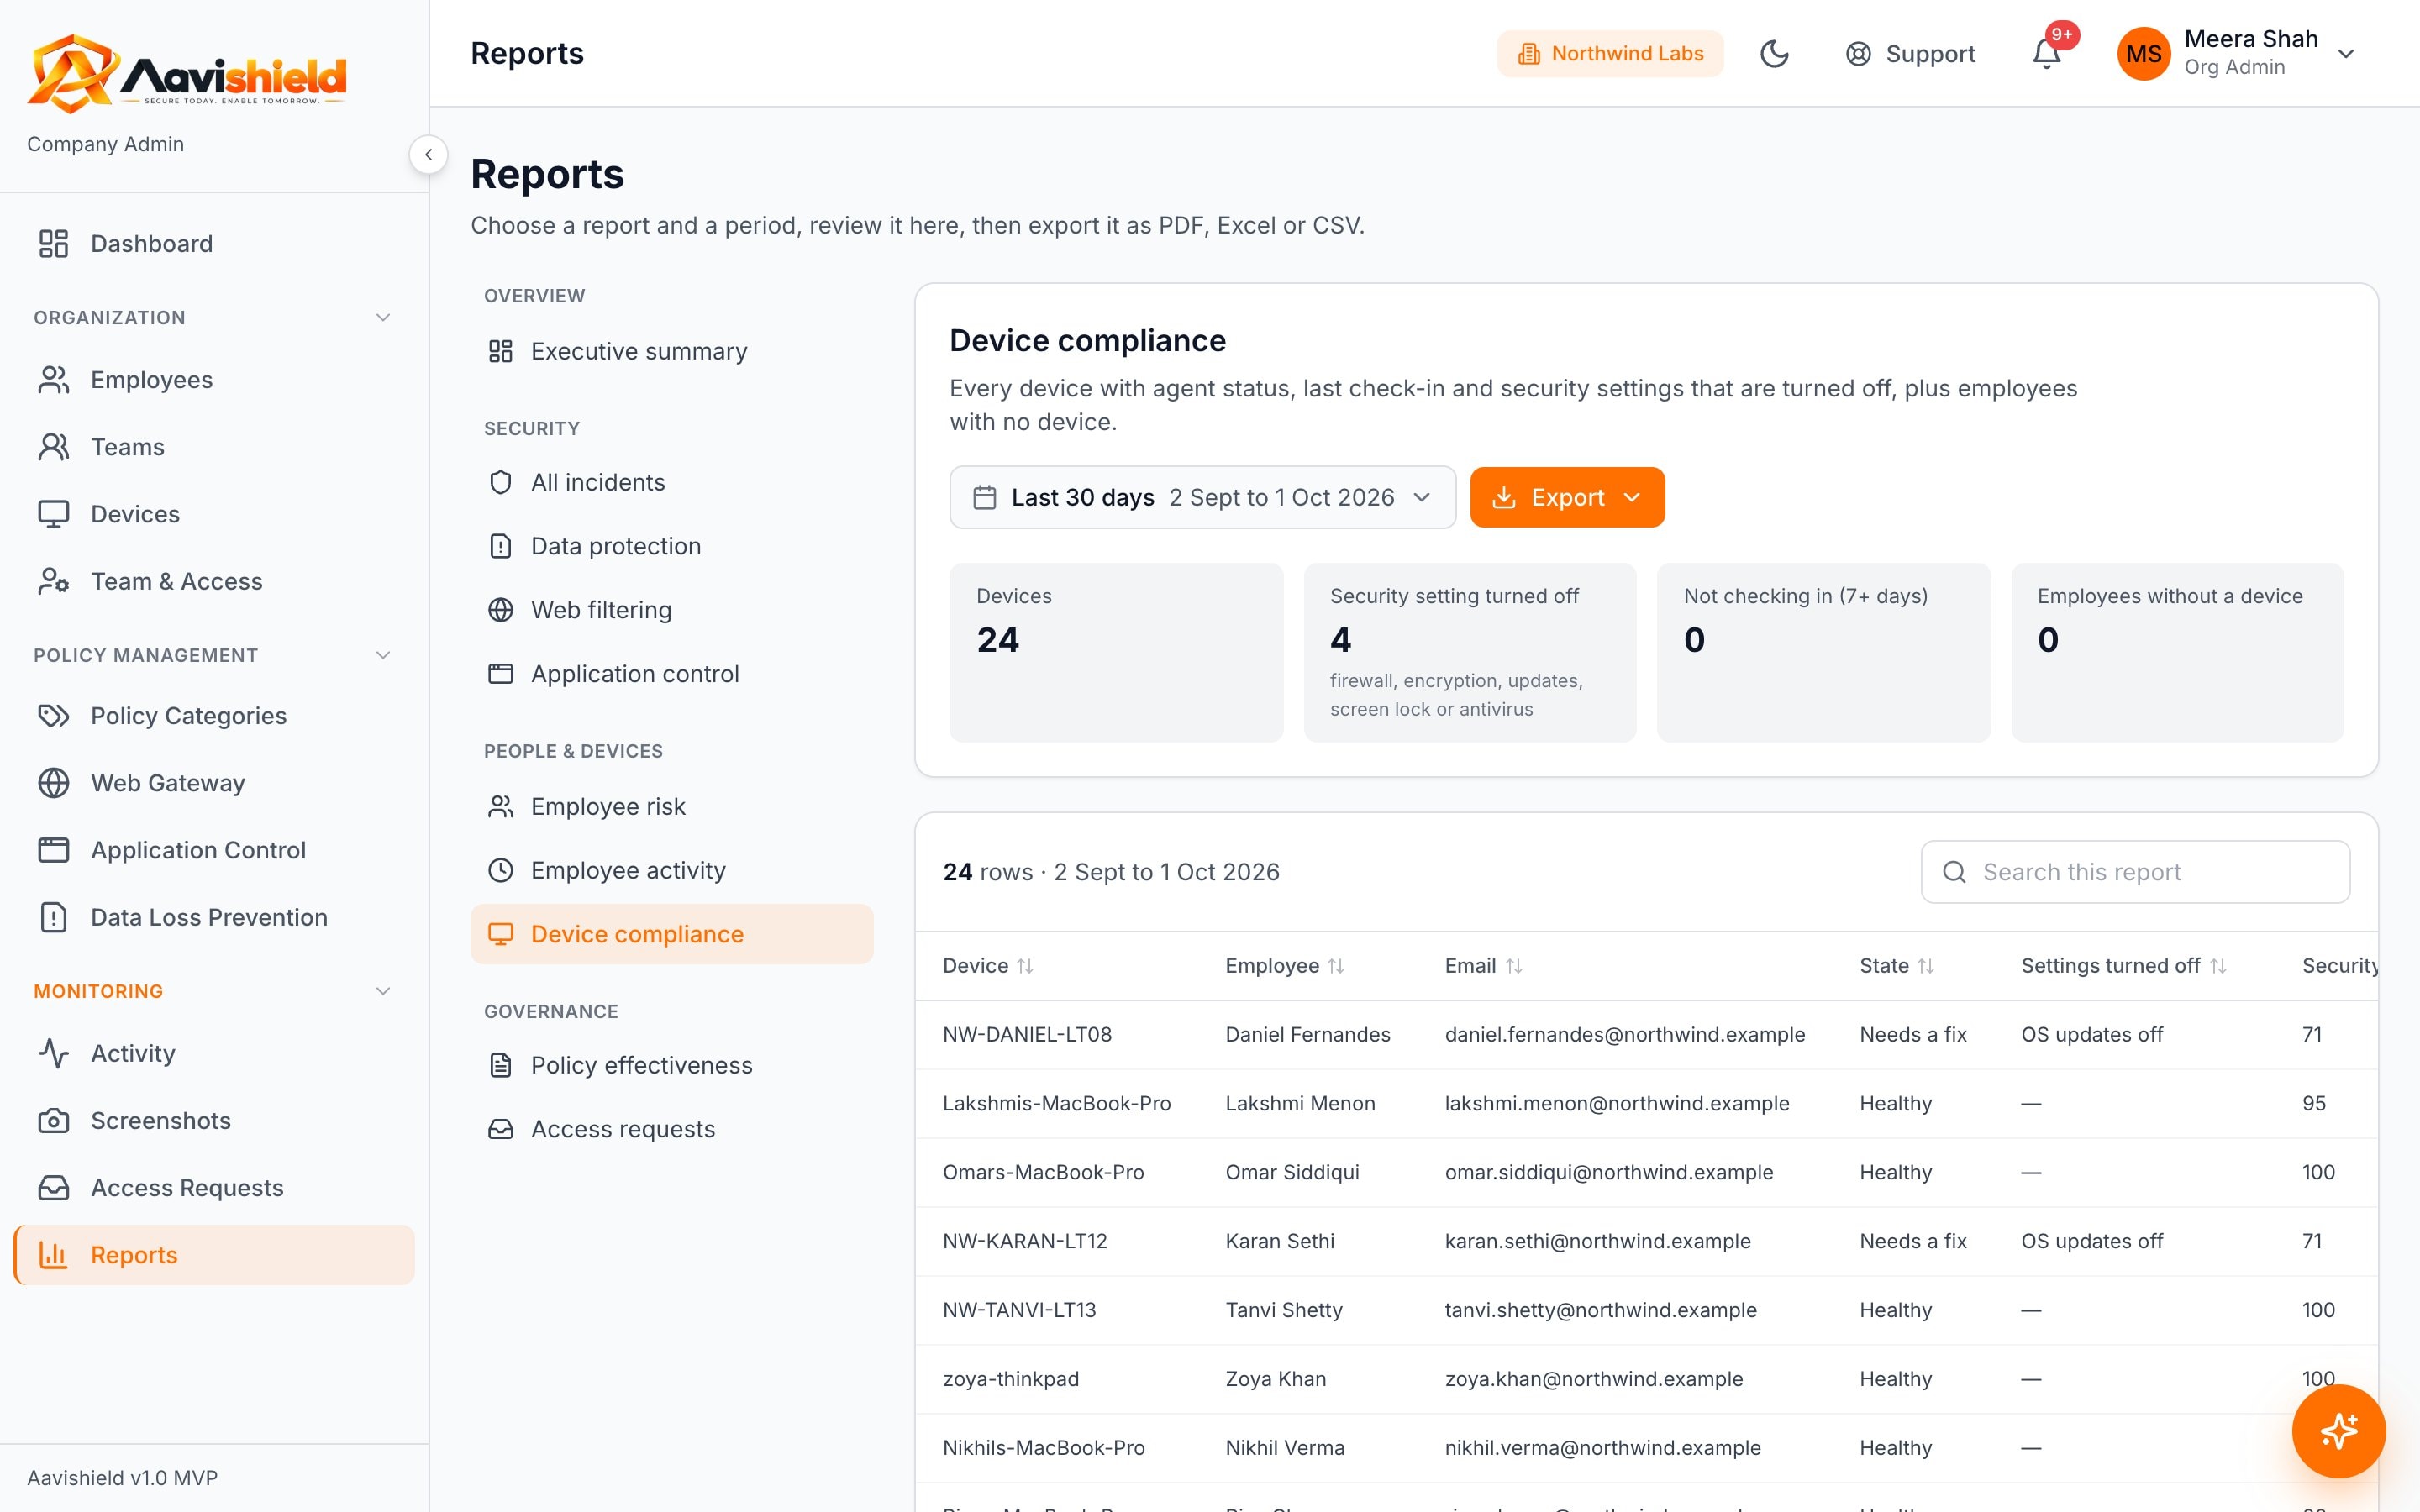
Each device, its owner, state, check-ins and settings that are off, ready for auditors.
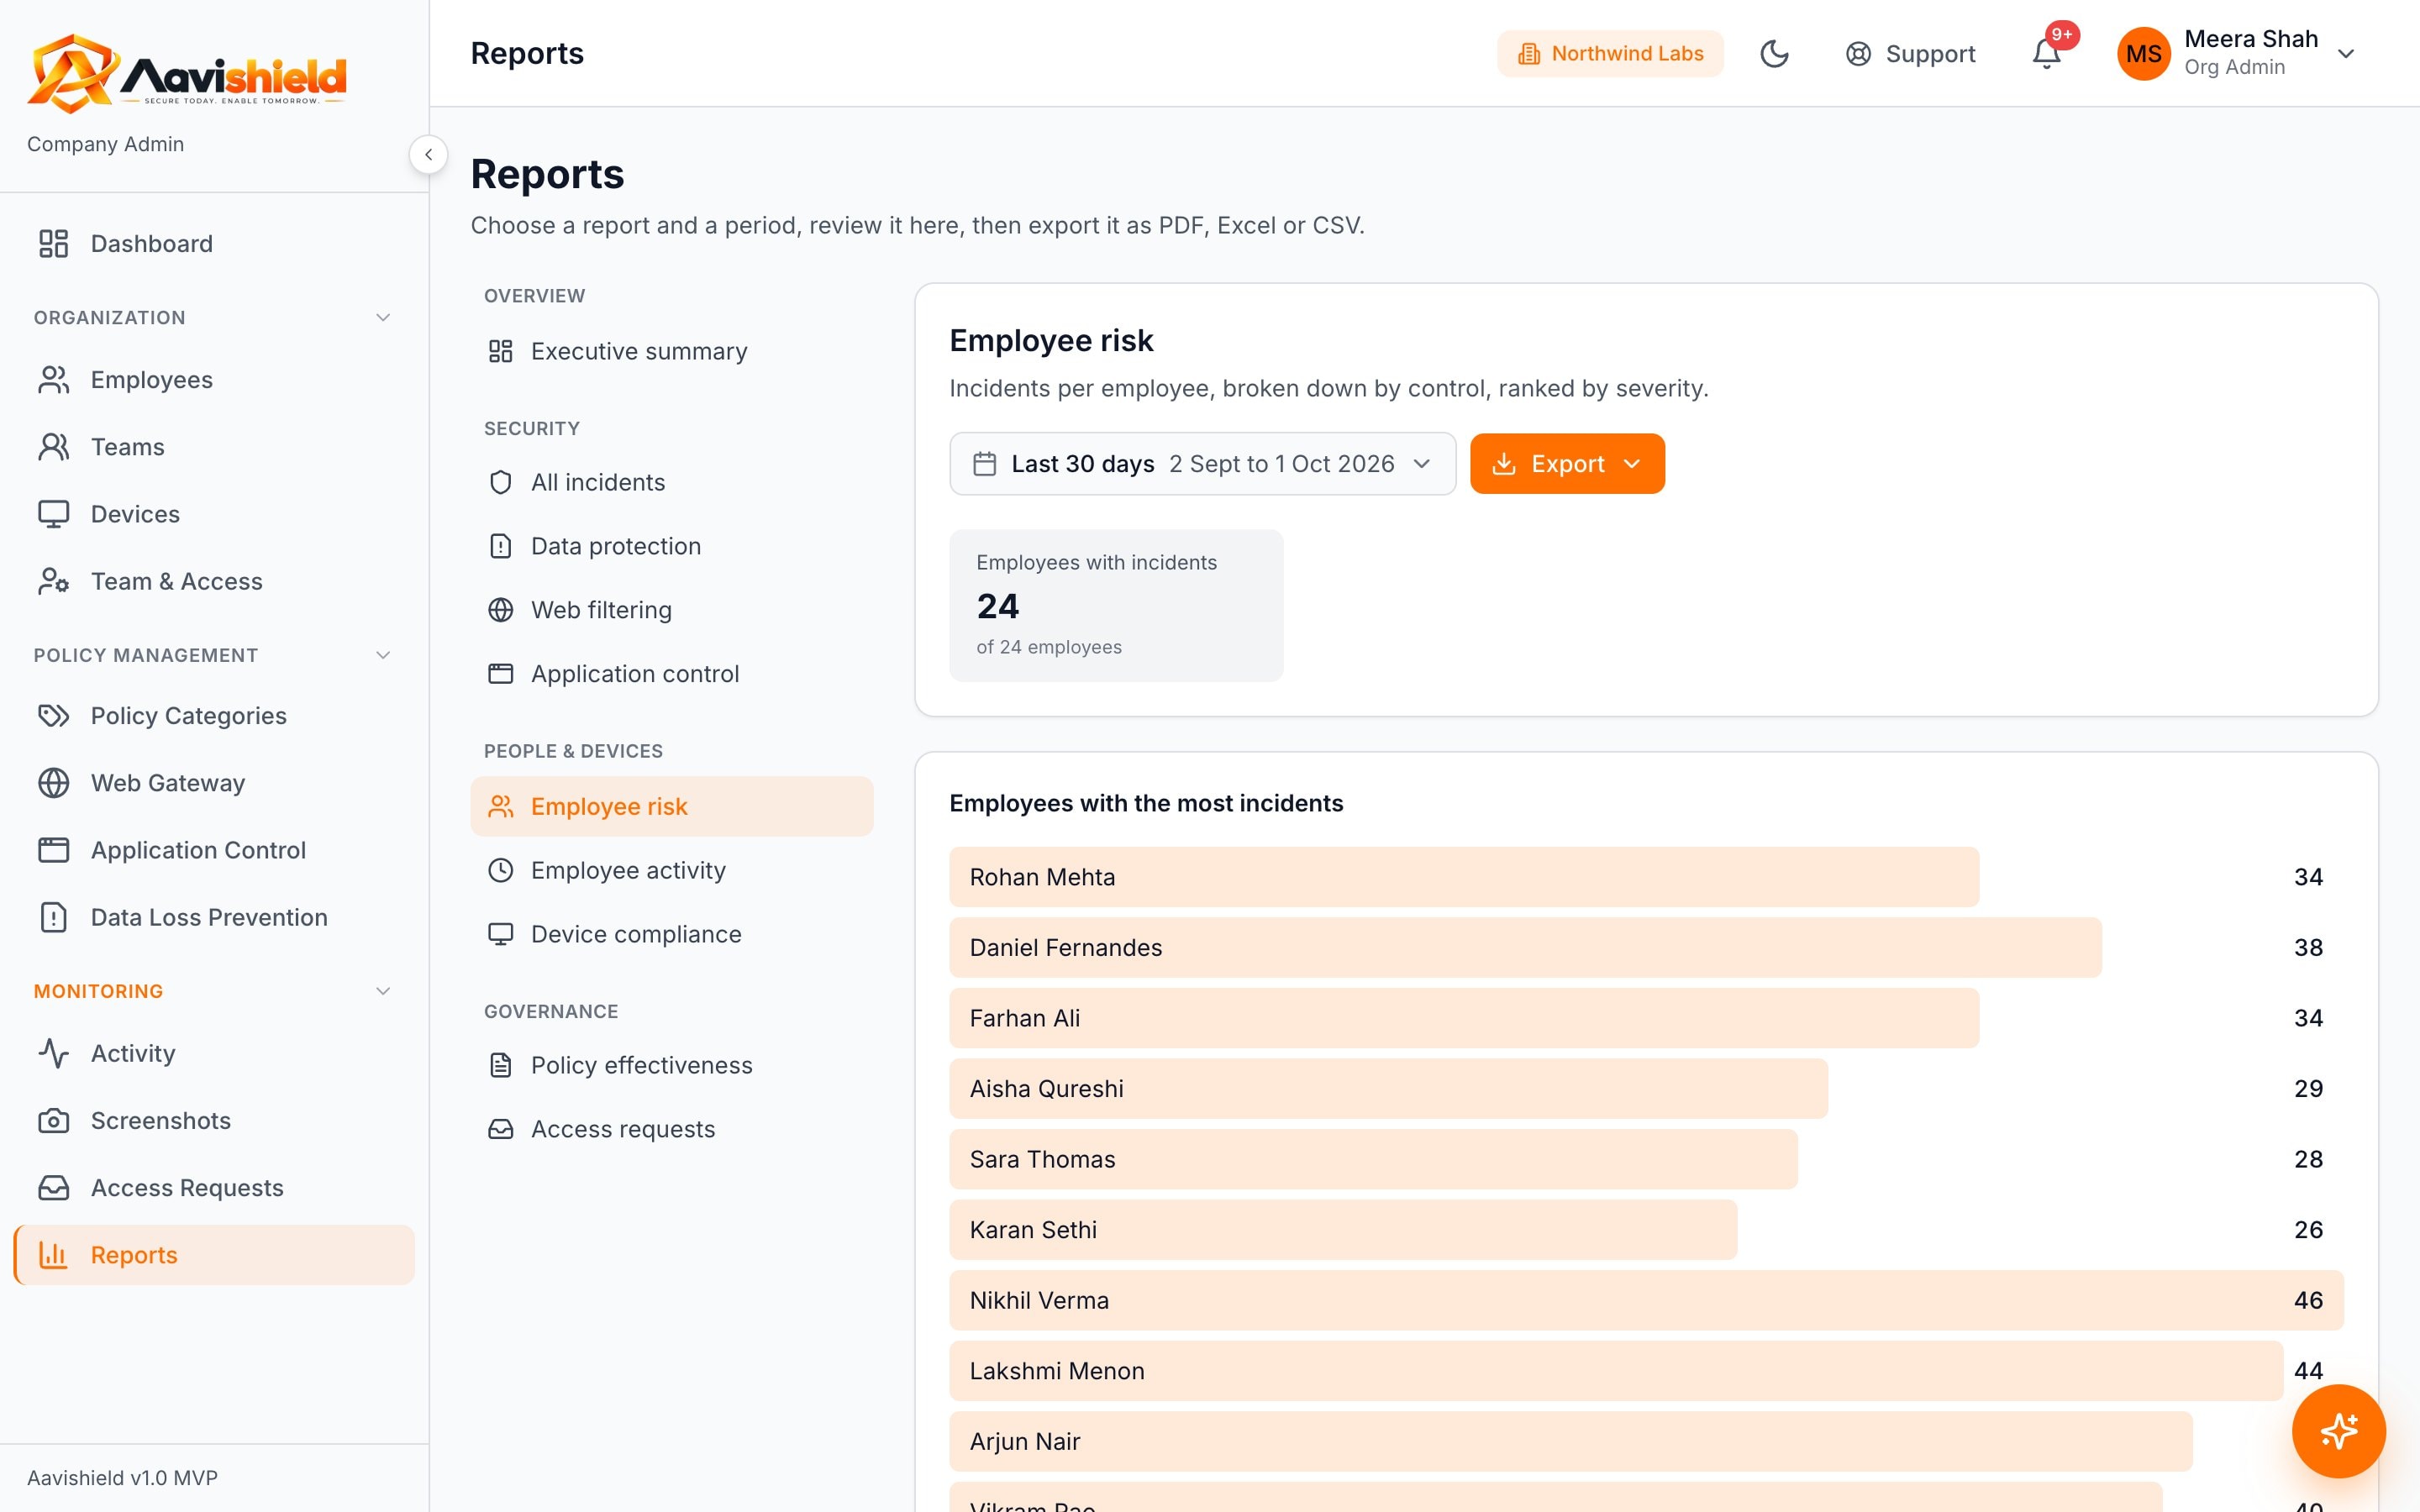
Employees ranked by incidents across every control.
The tools that make Aavishield easy for one person to operate.
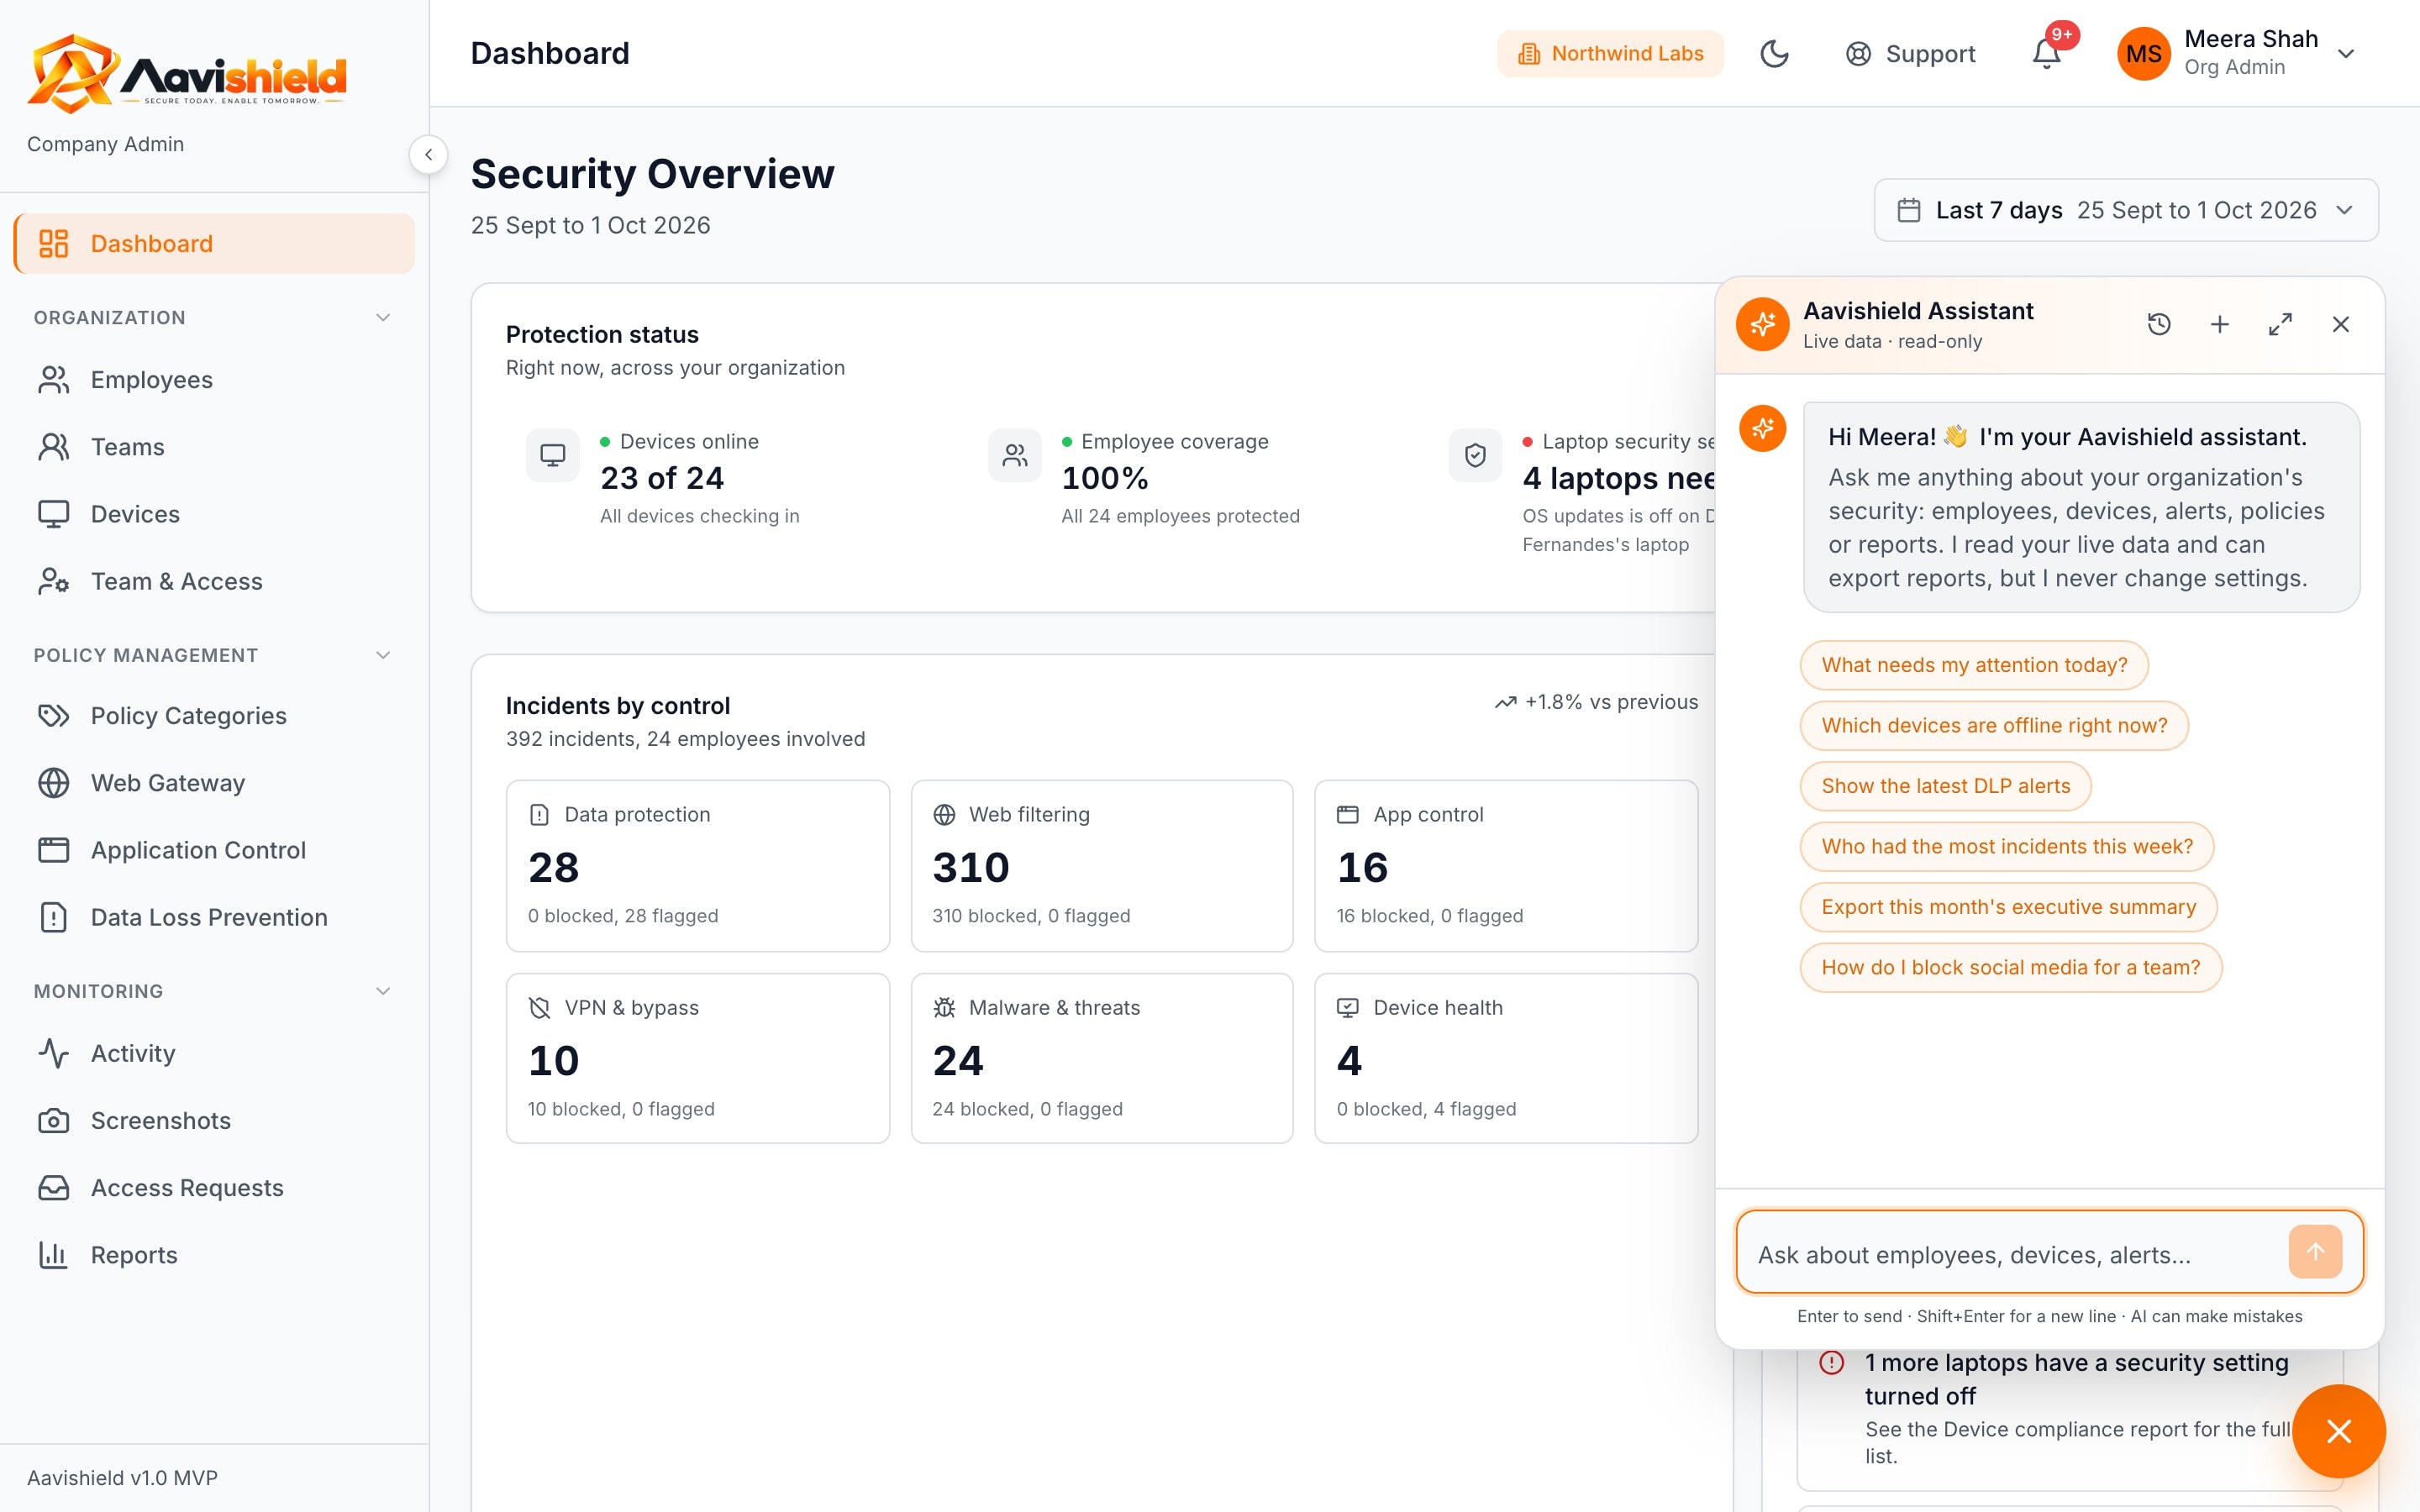
Ask what needs attention, which devices are offline or who had the most incidents. Answers come from live data.
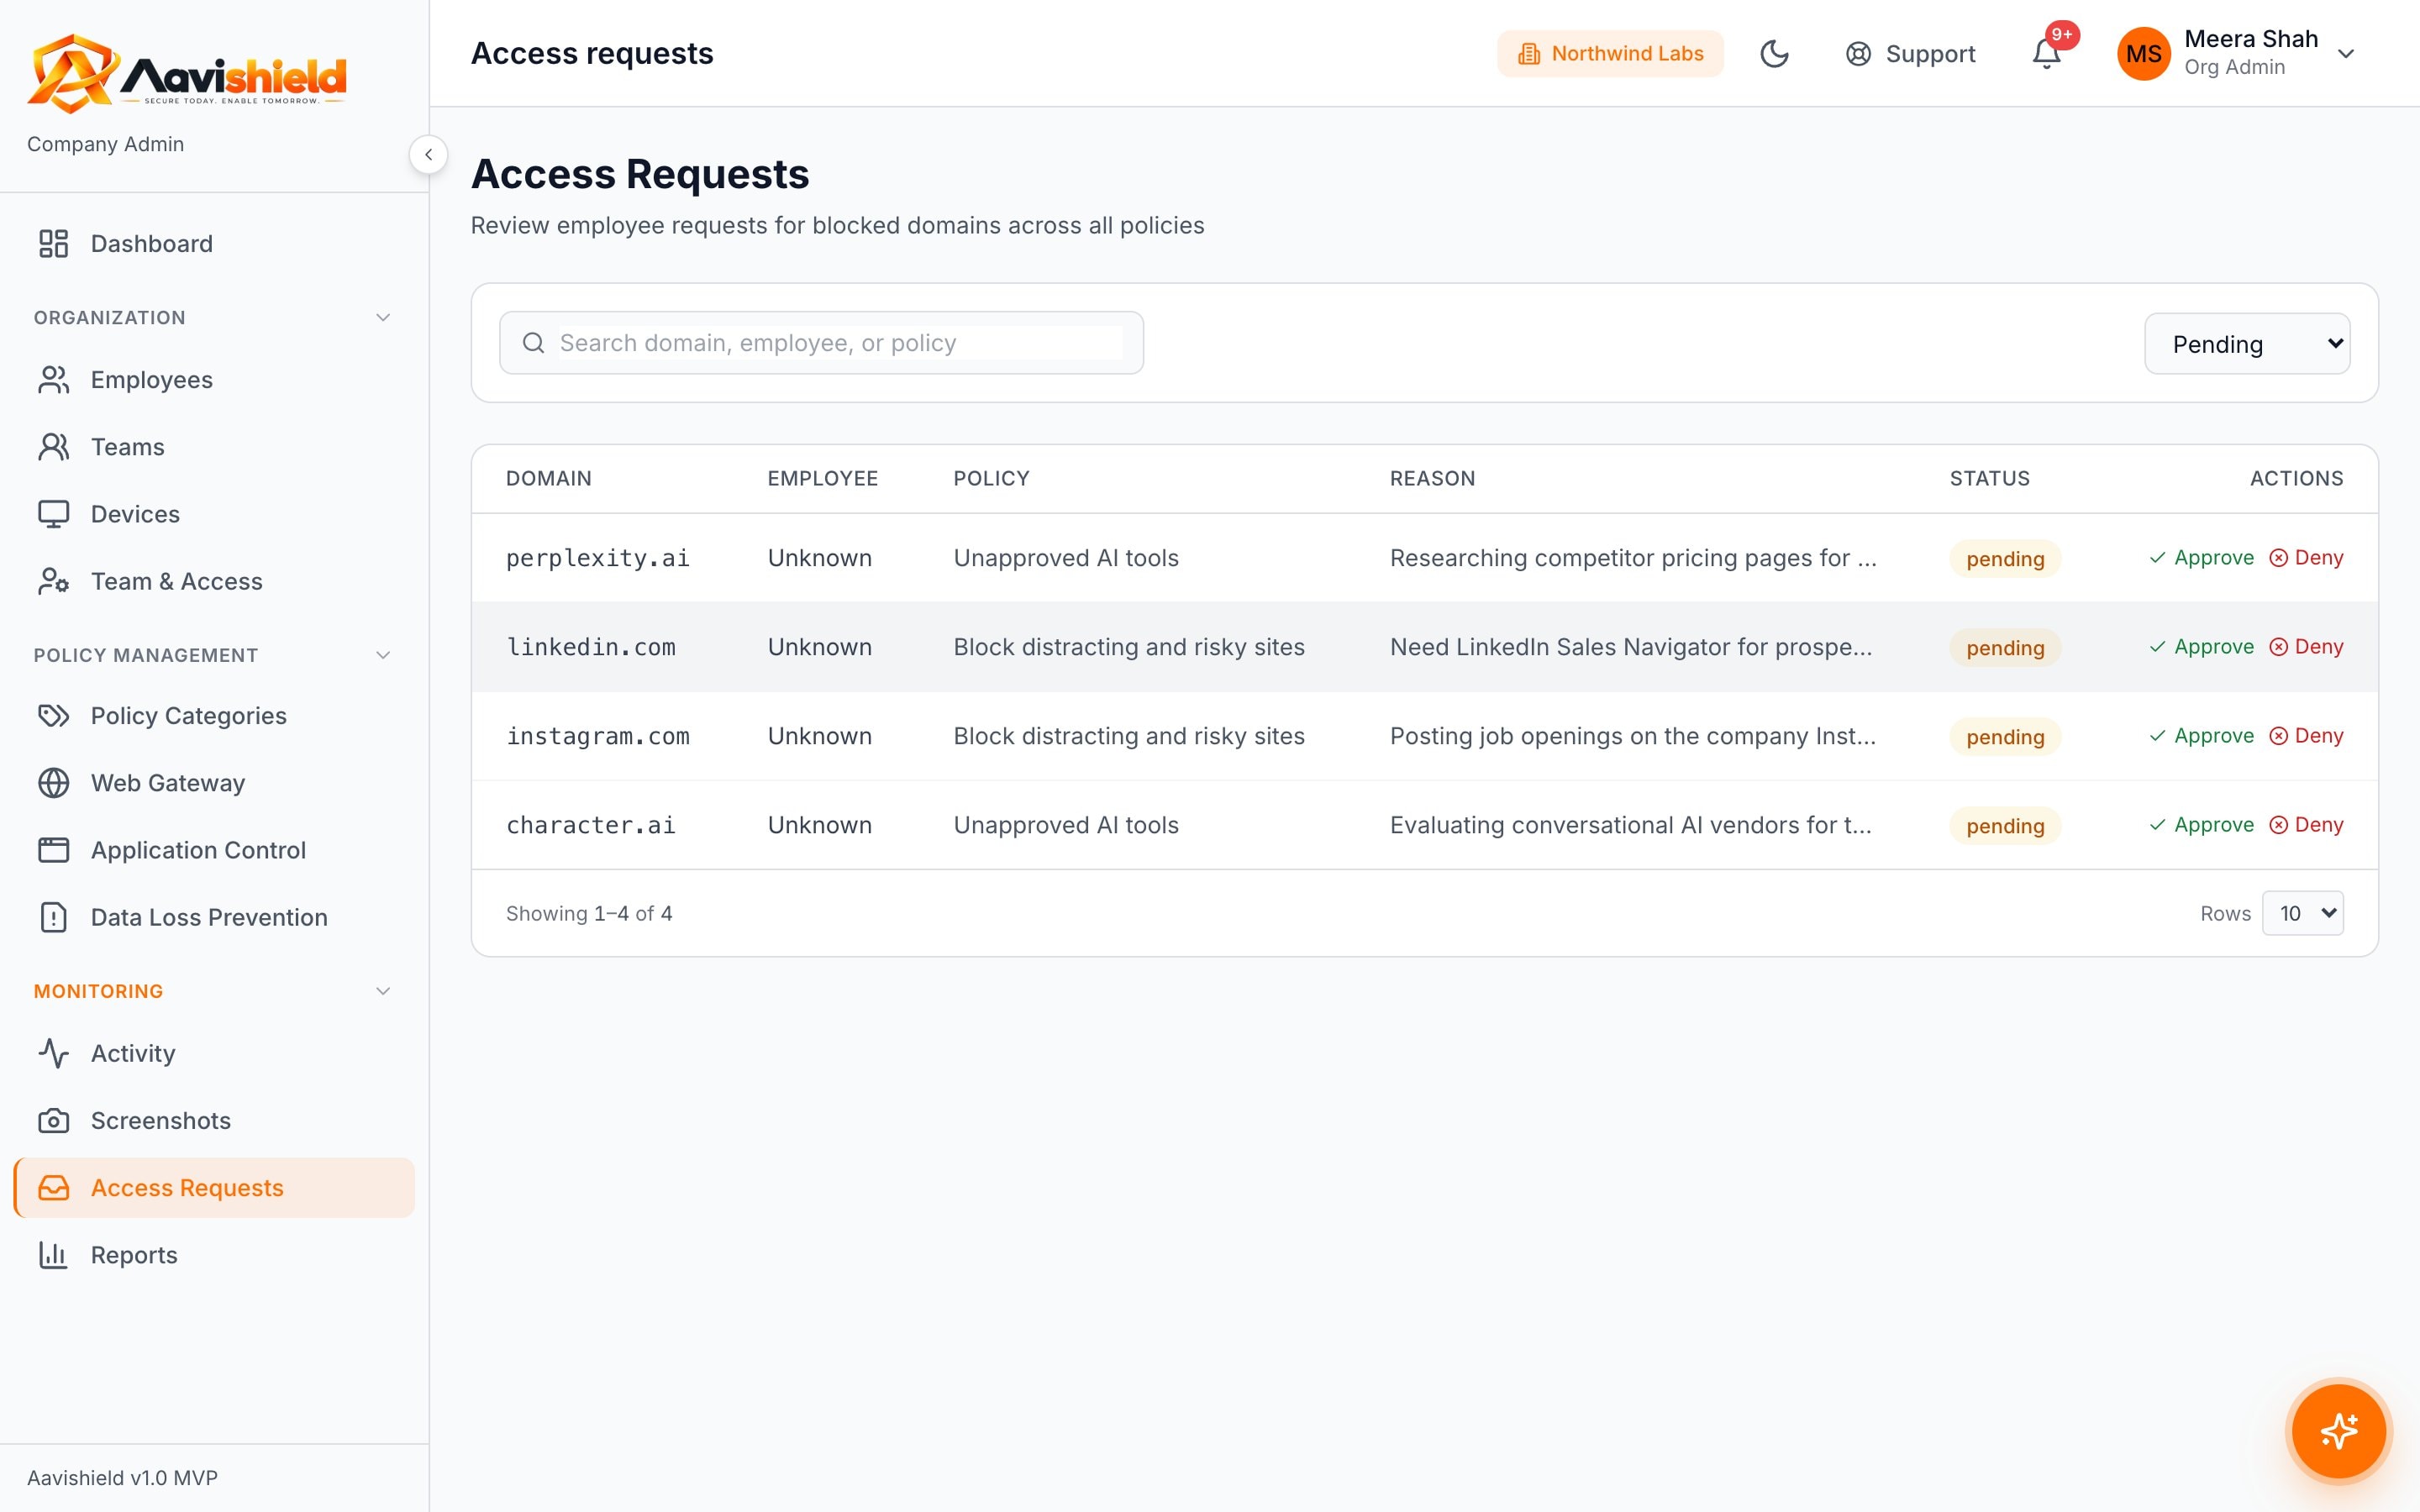
Employees ask to unblock a domain with a reason. Review and decide.
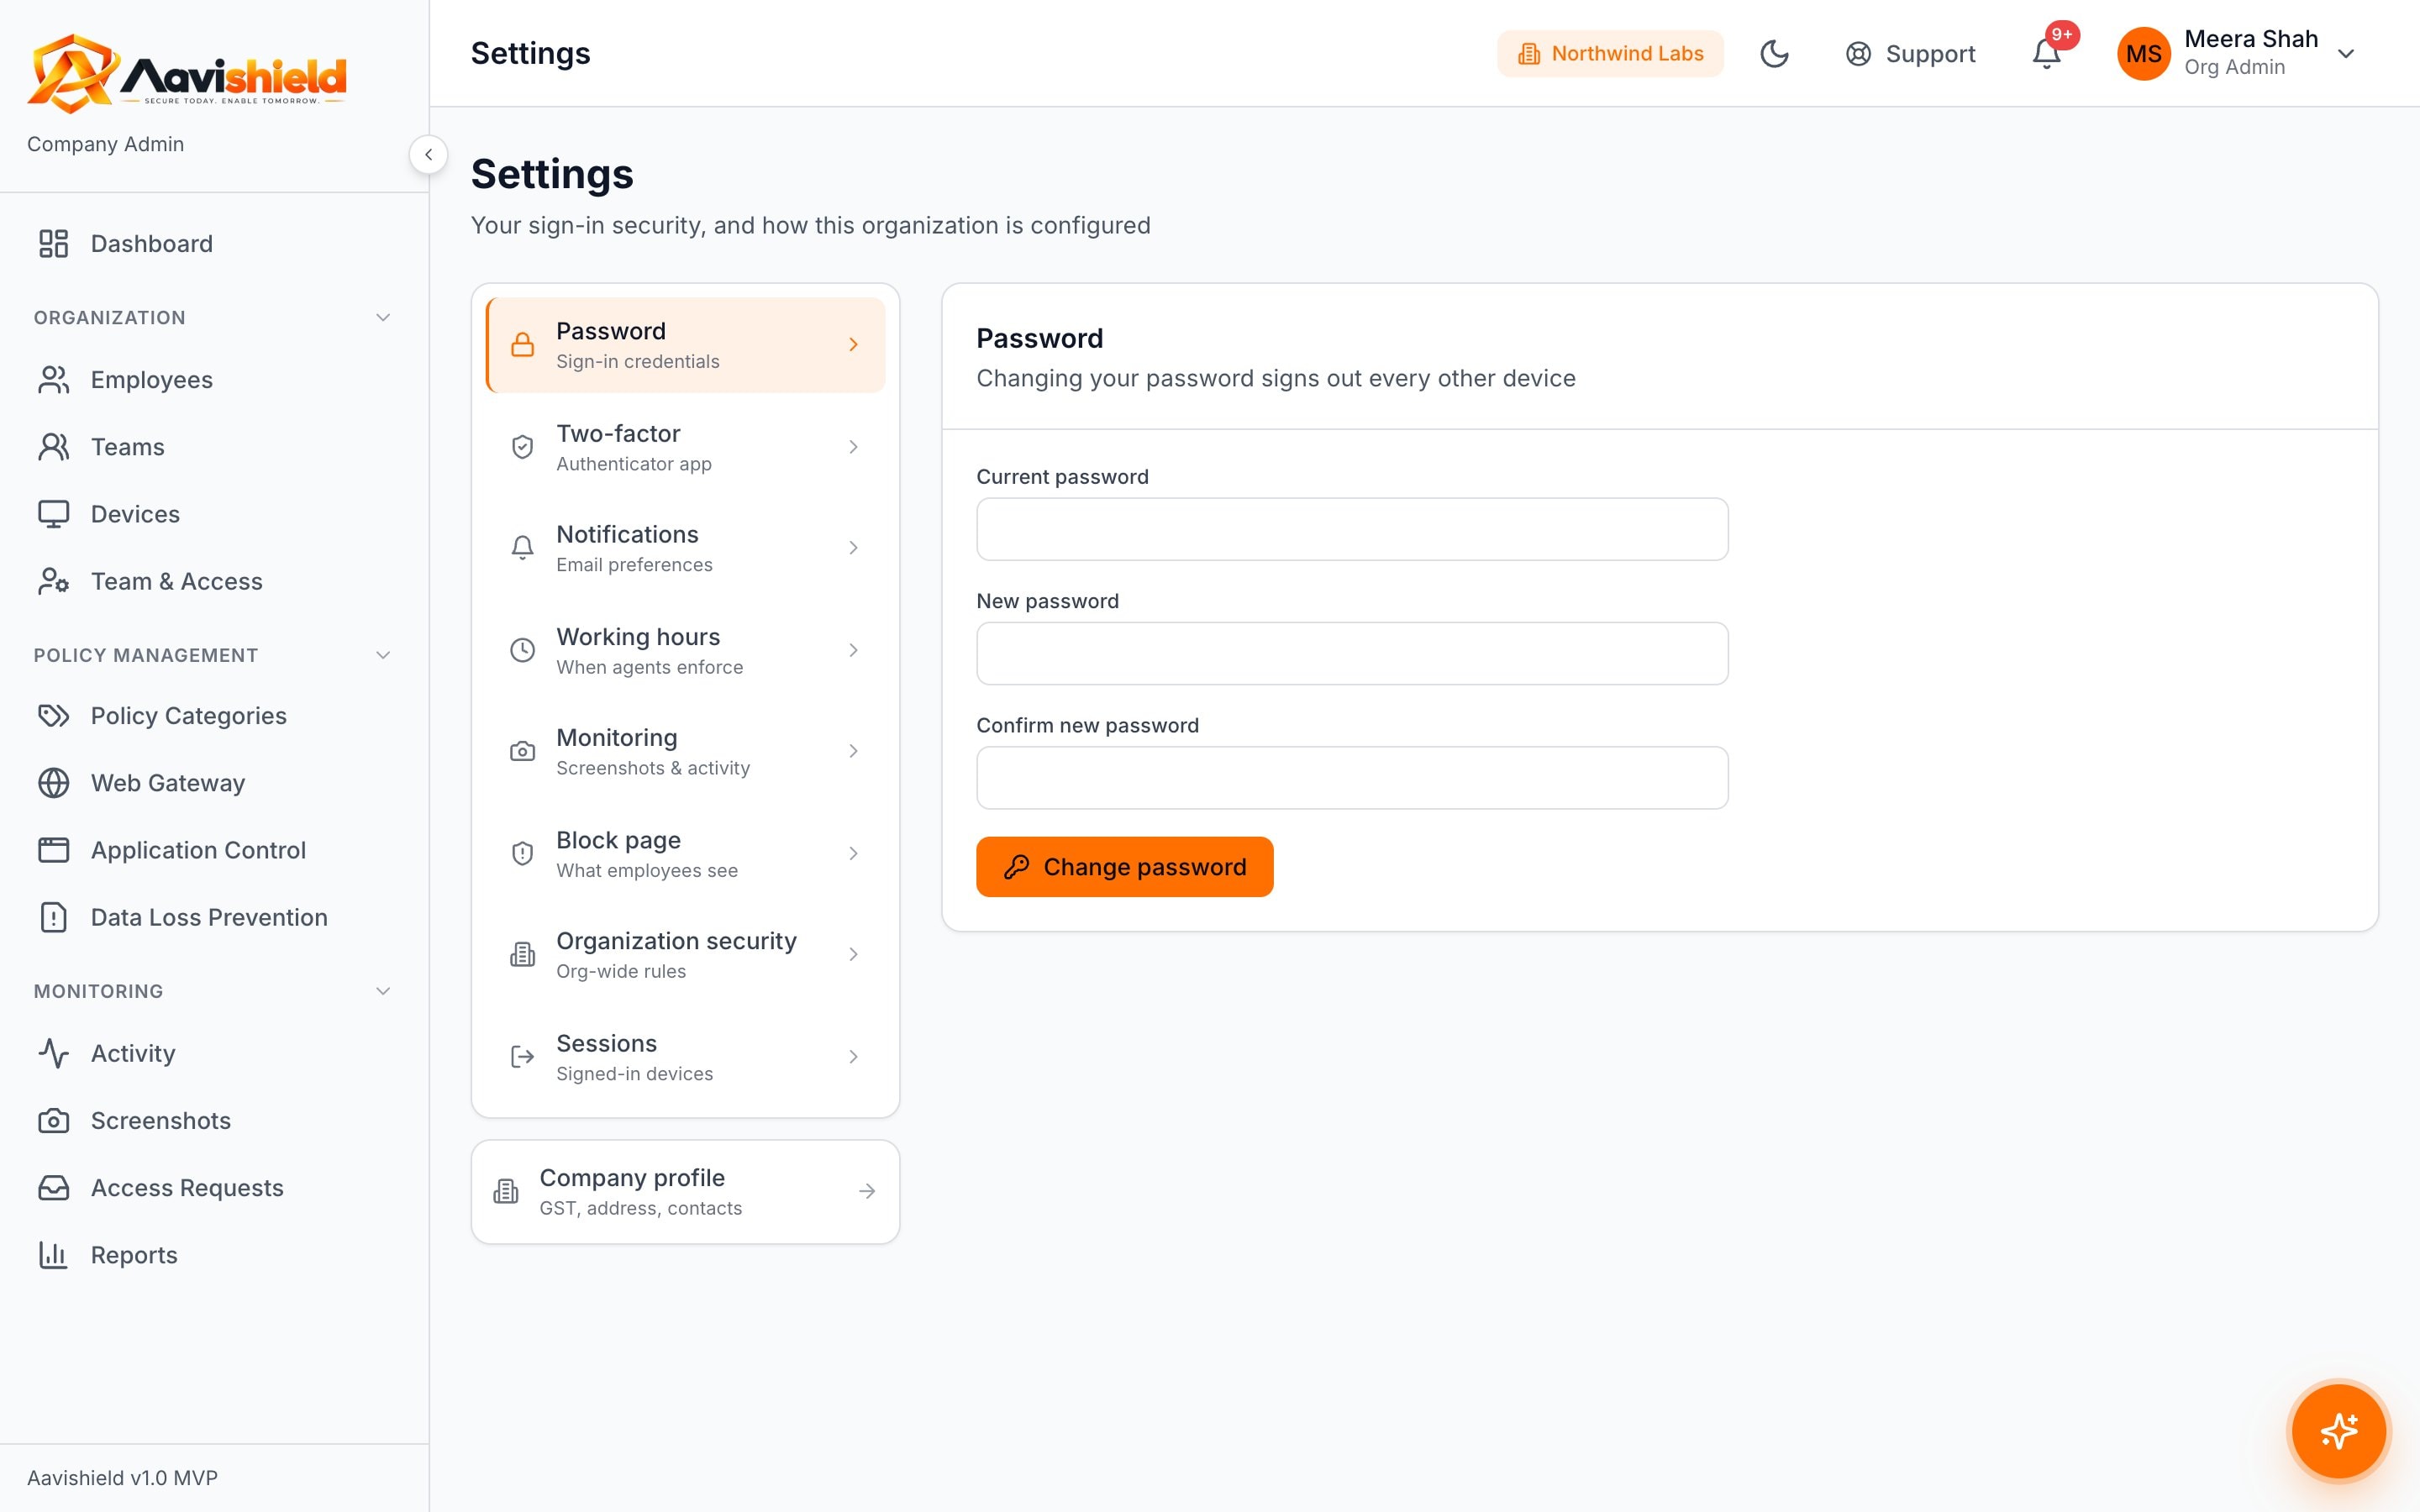
Password, two-factor, notifications, working hours, monitoring, block page, organisation security and sessions.
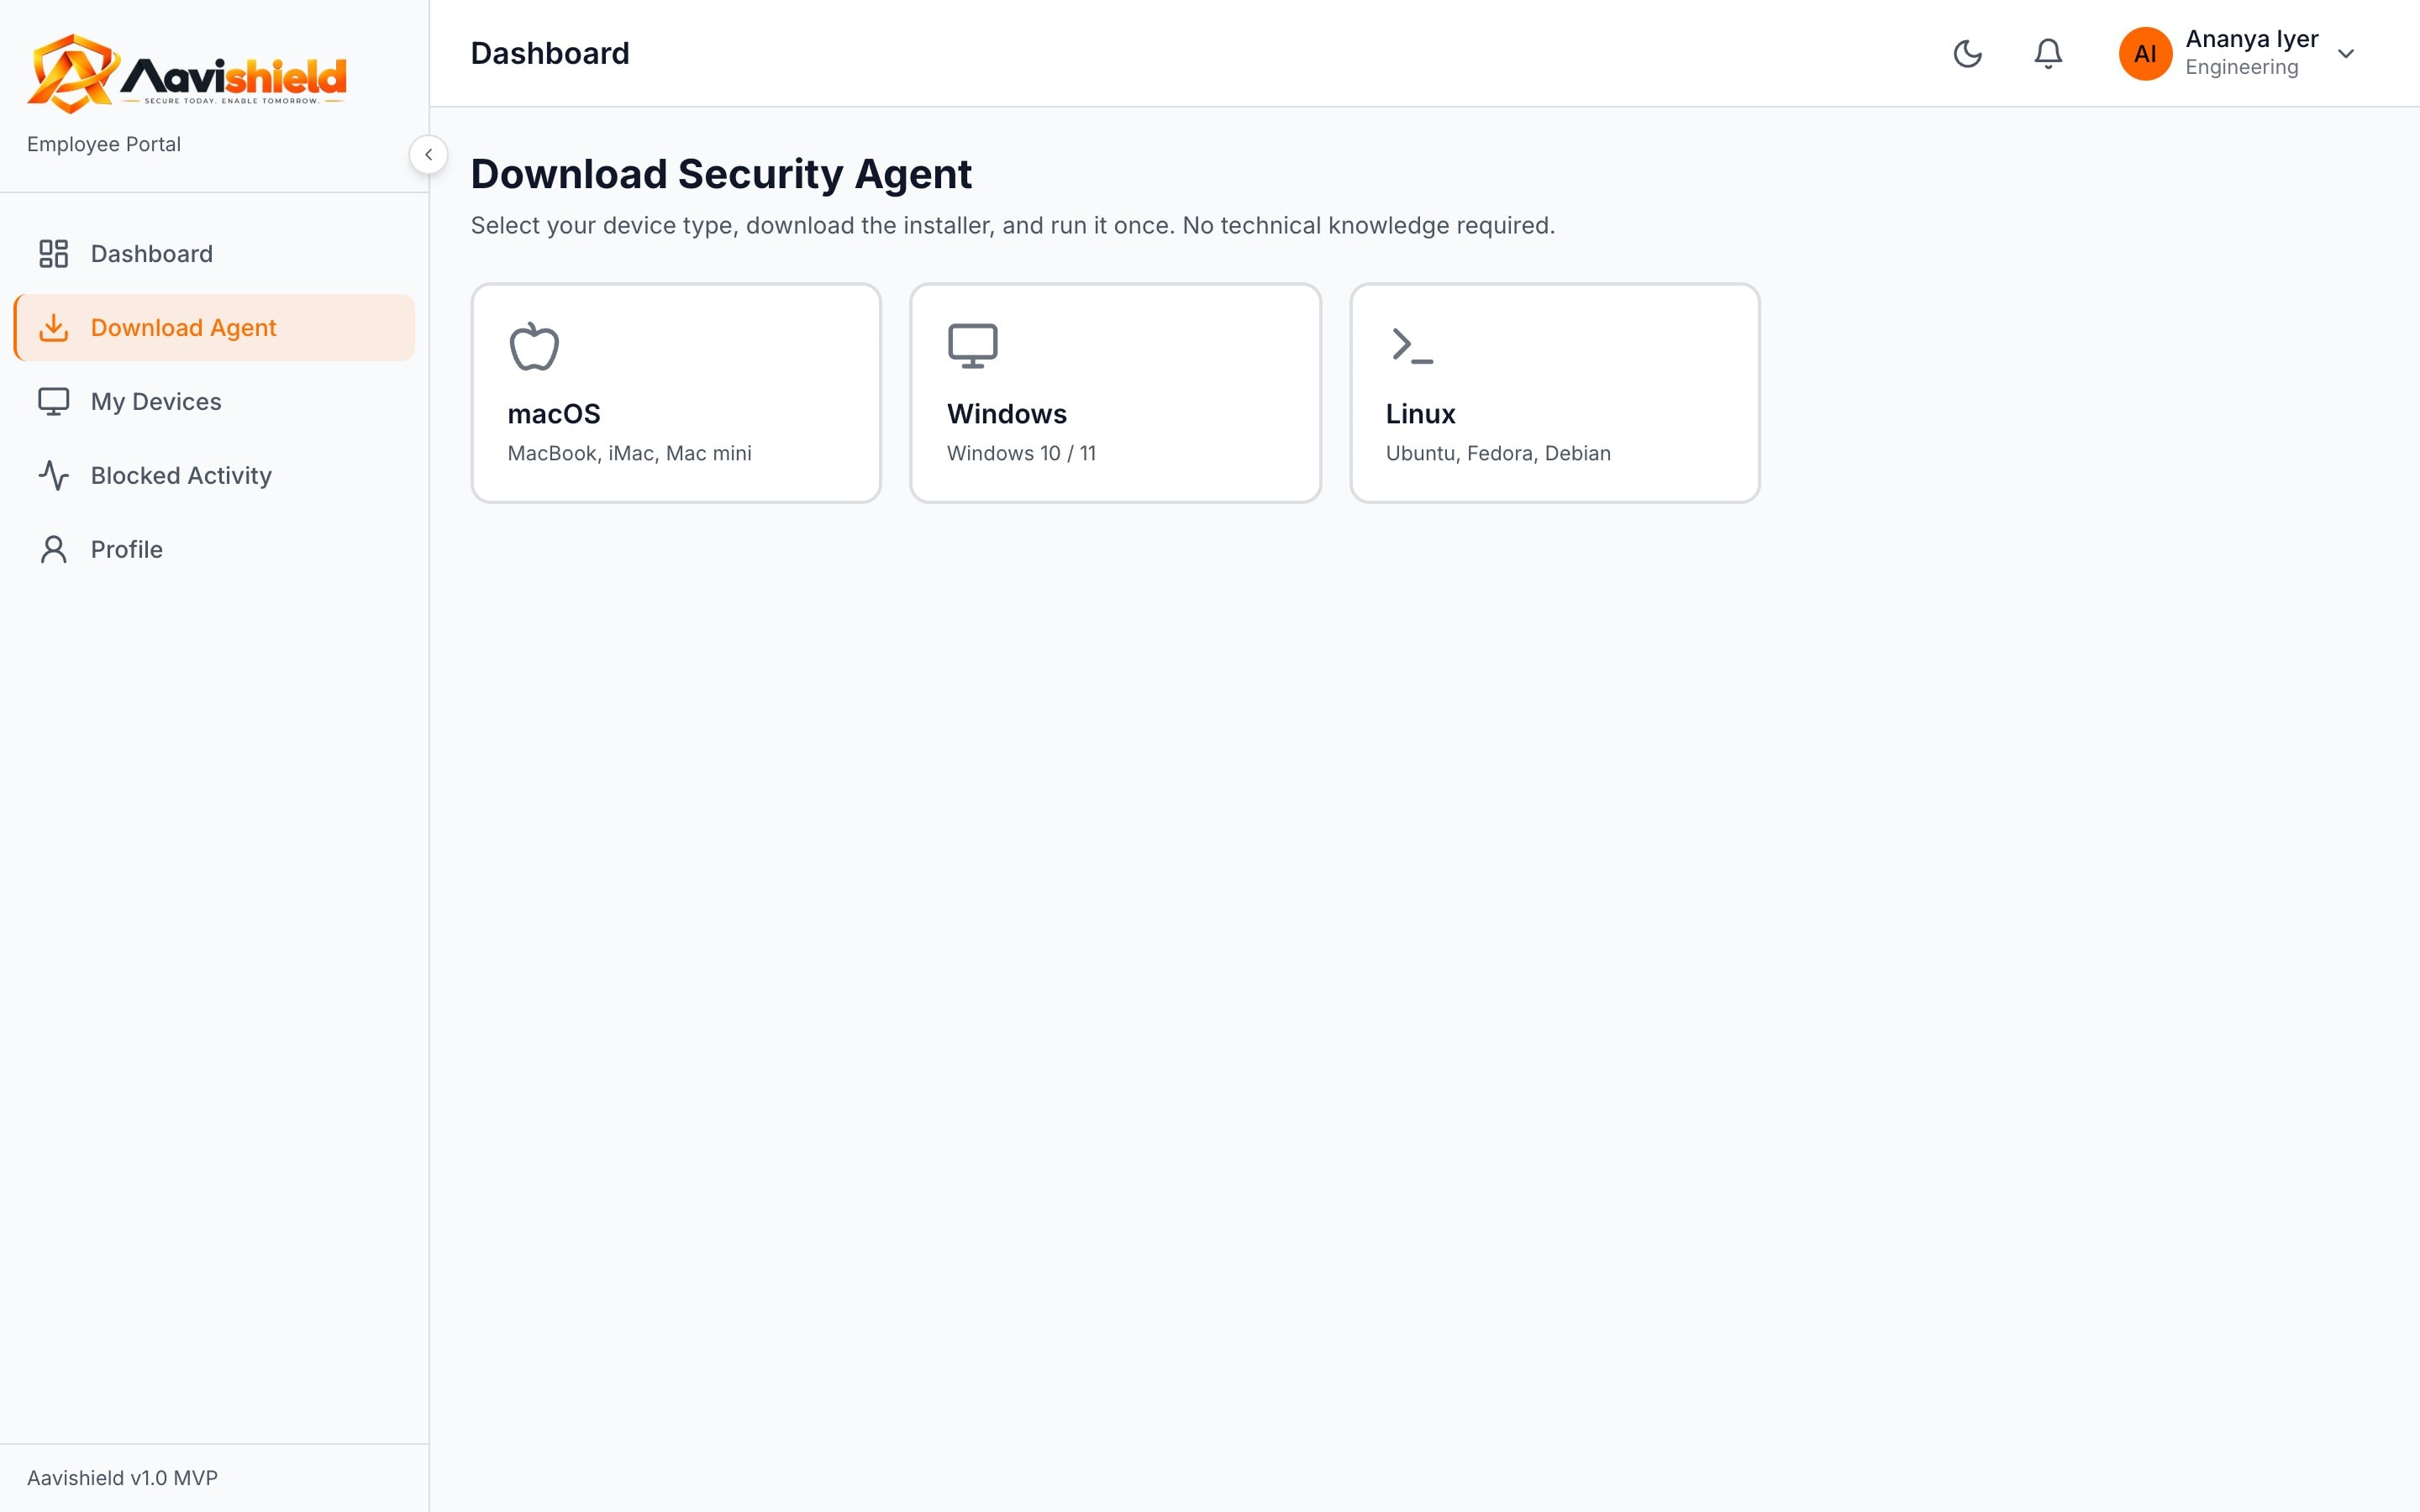
Employees install the agent, see their devices and understand what was blocked.
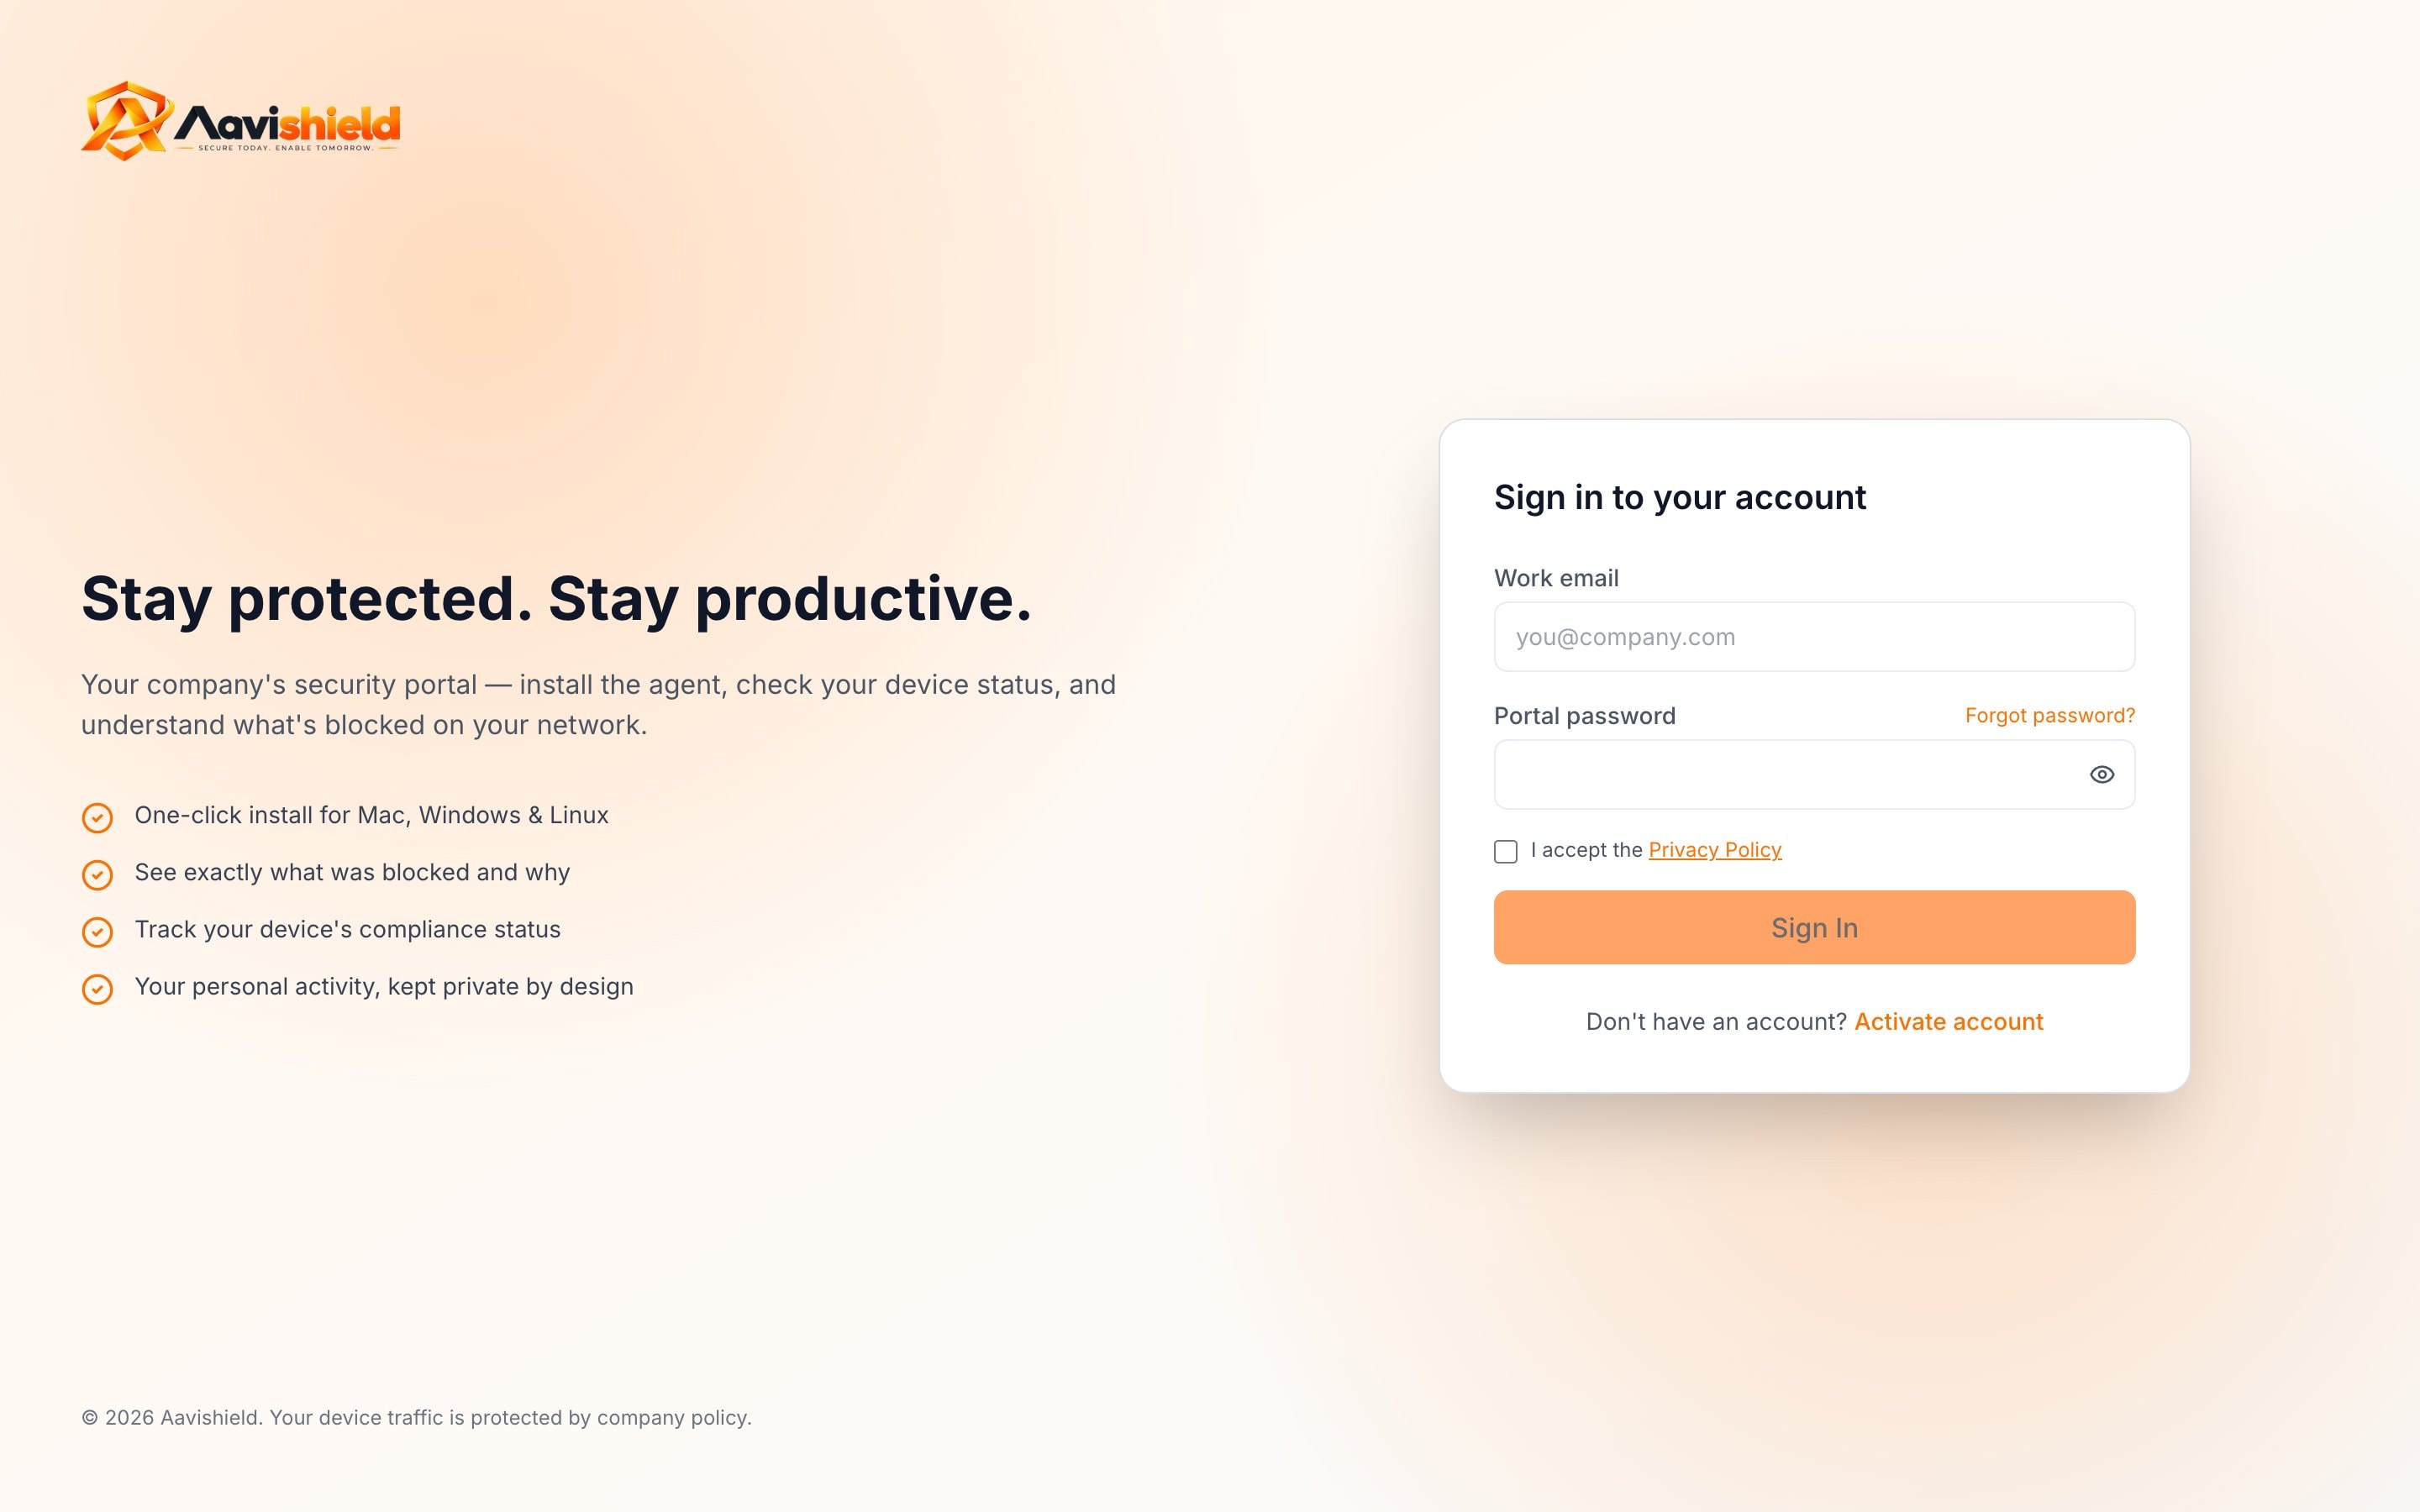
Employees activate their own account with their work email.
Native installers for macOS, Windows and Linux. No technical knowledge needed.
Install the agent, choose a policy, and see every decision in one console. A pilot can be live in an afternoon.